Computer - Software

Avast,enz.

Gestart door WillyV op 11 jun 2018, 16:45 17 berichten 4.431 keer gelezen Reageer
WillyV Startte dit onderwerp 11 jun 2018, 16:45 2030 Antwerpen 645 berichten
Beste leden,

Verleden week heb ik het programma Frostwire geupdated.Zonder dat ik er erg in had werden er 3 andere onderdelen mee geïnstalleerd : Avast,een uitgebreide Google Toolbar en nog een derde,waarvan ik me de naam niet meer herinner.
Met behulp van Revo Uninstaller Pro heb ik onmiddellijk deze onderdelen verwijderd.Ze werden verwijderd uit het Configuratiescherm en uit Revo Uninstaller Pro.
Tot mijn verbazing bleef Avast staan onder Program Files en kan ik het daar op geen enkele manier verwijderen,zoals je kan zien :


Afbeelding


Afbeelding


Afbeelding

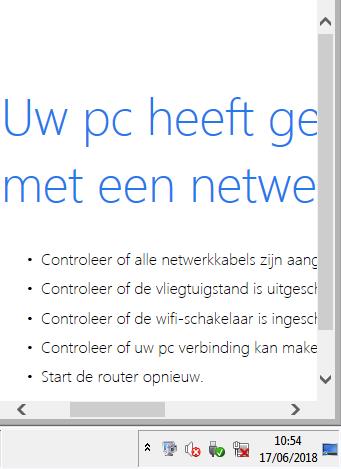
Ook  krijg ik nu regelmatig volgend bericht rechtsonderaan het scherm :


Afbeelding

Hoe kan ik dit alles verwijderd krijgen?


N.B.: Wanneer ik een nieuw onderwerp schrijf en ik ben onderaan het blad,scrolt het blad telkens terug naar boven en kan ik niet meer zien wat ik schrijf.

mvg,

WillyV
Intel Core i5-661/3,33GHz ; 2x2GB ; Windows 7 Home Premium 64 bit ; Microsoft Office 2010 Professional Plus ; HD1=500GB ; HD2=160GB ; Norton Security 5 ; CCleaner ; Malwarebytes Anti-Malware ;Windows Live Mail 2012.

    Citeer
    Danny. 11 jun 2018, 17:20 Vlaams Brabant 2.100 berichten
    Hey Willy, dat scrollen heb ik ook als mijn zoomniveau op 150% staat, probeer eens op 100%.

    't Is wel vervelend, maar het werkt, ik heb dit hier ook reeds gemeld maar nog geen antwoord erop bekomen, wel een antwoord, maar geen oplossing.

    Groetjes

    Danny
    Windows 11 Home 64-bit, Ram 8GB, Medion Akoya E23403 All-In-One, Microsoft Defender
      Citeer
      WillyV Startte dit onderwerp 12 jun 2018, 11:45 2030 Antwerpen 645 berichten
      Danny,

      Bij mij staat de zoom van I.E. 11 altijd op 100%.Dat kan de reden dus niet zijn.
      Is er dan geen andere mogelijkheid om dit scrollen te vermijden?Het is nogal frustrerend en voorheen had ik daar geen last van.

      mvg,
      WillyV
      Intel Core i5-661/3,33GHz ; 2x2GB ; Windows 7 Home Premium 64 bit ; Microsoft Office 2010 Professional Plus ; HD1=500GB ; HD2=160GB ; Norton Security 5 ; CCleaner ; Malwarebytes Anti-Malware ;Windows Live Mail 2012.

        Citeer
        abbs 12 jun 2018, 12:08 Leidschendam 1.589 berichten
        Hallo,


        Om je van al die extra programma's te verlossen voer het volgende uit:

        https://www.seniorennet.be/forum/viewtopic.php?t=197564

        Upload de twee logjes  (FRST.txt) & (Addition.txt) dan weet ik zeker dat ze compleet zijn:
        • Klik op: http://www.filedropper.com/.
        • Klik op die site op Afbeelding
        • Verkenner opent > klik links boven op Bureaublad > dubbel klik rechts  FRST.txt.
        • Kopieer nu de link die nu onder "Link To Share This File With Anyone" staat en plak die in je volgende antwoord.
        Doe dat ook met  Addition.txt.
        Groeten abbs
        Afbeelding
        Member of UNITE (Unified Network of Instructors and Trained Eliminators)
          Citeer
          WillyV Startte dit onderwerp 12 jun 2018, 16:42 2030 Antwerpen 645 berichten
          abbs,

          Het logje van FRST.txt

          Scanresultaten van Farbar Recovery Scan Tool (FRST) (x64) Versie: 06.06.2018 01
          Gestart door Gebruiker (Beheerder) op GEBRUIKER-PC (12-06-2018 16:34:53)
          Gestart vanaf C:\Users\Gebruiker\Desktop
          Geladen Profielen: Gebruiker (Beschikbare Profielen: Gebruiker)
          Platform: Windows 7 Home Premium Service Pack 1 (X64) Taal: Nederlands (Nederland)
          Internet Explorer Versie 11 (Standaardbrowser: IE)
          Boot Modus: Normal
          Handleiding voor Farbar Recovery Scan Tool: http://www.geekstogo.com/forum/topic/33 ... scan-tool/==================== Processen (gefilterd) =================(Als een item is opgenomen in de fixlist, zal het proces worden gesloten. Het bestand zal niet worden verplaatst.)(AVAST Software) C:\Program Files\AVAST Software\Avast\AvastSvc.exe
          (ArcSoft Inc.) C:\Program Files (x86)\Common Files\ArcSoft\Connection Service\Bin\ACService.exe
          (Apple Inc.) C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
          (Apple Inc.) C:\Program Files\Bonjour\mDNSResponder.exe
          (Microsoft Corporation) C:\Windows\SysWOW64\svchost.exe
          () C:\Program Files (x86)\Canon\IJPLM\ijplmsvc.exe
          (Intel Corporation) C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\LMS\LMS.exe
          (Symantec Corporation) C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\nortonsecurity.exe
          (Protexis Inc.) C:\Program Files (x86)\Common Files\Protexis\License Service\PsiService_2.exe
          (Paramount Software UK Ltd) C:\Program Files\Macrium\Reflect\ReflectService.exe
          () C:\Program Files (x86)\CyberLink\Shared files\RichVideo.exe
          (TeamViewer GmbH) C:\Program Files (x86)\TeamViewer\TeamViewer_Service.exe
          (TechSmith Corporation) C:\Program Files (x86)\Common Files\TechSmith Shared\Uploader\UploaderService.exe
          (Symantec Corporation) C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\nortonsecurity.exe
          (Microsoft Corp.) C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVC.EXE
          (Microsoft Corp.) C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVCM.EXE
          (Realtek Semiconductor) C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe
          (Microsoft Corporation) C:\Windows\WindowsMobile\wmdc.exe
          (Intel Corporation) C:\Windows\System32\igfxtray.exe
          (Intel Corporation) C:\Windows\System32\hkcmd.exe
          (Intel Corporation) C:\Windows\System32\igfxpers.exe
          (Oracle Corporation) C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe
          (AVAST Software) C:\Program Files\AVAST Software\Avast\AvastUI.exe
          (Microsoft Corporation) C:\Windows\System32\dllhost.exe
          (HP Inc.) C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\HPSupportSolutionsFrameworkService.exe
          (HP Inc.) C:\Program Files\HP\HP Touchpoint Analytics Client\TouchpointAnalyticsClientService.exe
          (Intel Corporation) C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\UNS\UNS.exe
          (Microsoft Corporation) C:\Program Files\Common Files\Microsoft Shared\OfficeSoftwareProtectionPlatform\OSPPSVC.EXE
          (Microsoft Corporation) C:\Program Files (x86)\Windows Live\Mail\wlmail.exe
          (Microsoft Corporation) C:\Program Files (x86)\Windows Live\Contacts\wlcomm.exe
          (Microsoft Corporation) C:\Program Files\Internet Explorer\iexplore.exe
          (Microsoft Corporation) C:\Windows\System32\dllhost.exe==================== Register (gefilterd) ===========================(Als een item is opgenomen in de fixlist, zal het registeritem worden teruggezet naar de standaardwaarden of verwijderd. Het bestand zal niet worden verplaatst.)HKLM\...\Run: [RtHDVCpl] => C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe [8306208 2009-10-21] (Realtek Semiconductor)
          HKLM\...\Run: [Windows Mobile Device Center] => C:\Windows\WindowsMobile\wmdc.exe [660360 2007-05-31] (Microsoft Corporation)
          HKLM\...\Run: [AvastUI.exe] => C:\Program Files\AVAST Software\Avast\AvLaunch.exe [242904 2018-06-10] (AVAST Software)
          HKLM-x32\...\Run: [SunJavaUpdateSched] => C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe [588704 2018-03-28] (Oracle Corporation)
          Winlogon\Notify\igfxcui: C:\Windows\system32\igfxdev.dll (Intel Corporation)==================== Internet (gefilterd) ====================(Als een item is opgenomen in de fixlist en een registeritem is, wordt het verwijderd of hersteld naar de standaard.)Hosts: Er zijn meer dan één item in Hosts. Zie Hosts deel van Addition.txt
          Tcpip\Parameters: [DhcpNameServer] 192.168.1.1
          Tcpip\..\Interfaces\{BA496367-23C3-4955-AD20-3F16728F21E8}: [DhcpNameServer] 192.168.1.1Internet Explorer:
          ==================
          HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = hxxp://www.google.com
          HKLM\Software\Wow6432Node\Microsoft\Internet Explorer\Main,Start Page = hxxp://www.google.com
          HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = hxxp://www.google.com
          HKLM\Software\Wow6432Node\Microsoft\Internet Explorer\Main,Search Page = hxxp://www.google.com
          HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = hxxp://www.google.com
          HKLM\Software\Wow6432Node\Microsoft\Internet Explorer\Main,Default_Page_URL = hxxp://www.google.com
          HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = hxxp://www.google.com
          HKLM\Software\Wow6432Node\Microsoft\Internet Explorer\Main,Default_Search_URL = hxxp://www.google.com
          HKU\.DEFAULT\Software\Microsoft\Internet Explorer\Main,Search Page = hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar=iesearch
          HKU\S-1-5-19\Software\Microsoft\Internet Explorer\Main,Search Page = hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar=iesearch
          HKU\S-1-5-20\Software\Microsoft\Internet Explorer\Main,Search Page = hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar=iesearch
          HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\Software\Microsoft\Internet Explorer\Main,Search Page = hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar=iesearch
          HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\Software\Microsoft\Internet Explorer\Main,Start Page = hxxps://www.google.be/
          SearchScopes: HKU\.DEFAULT -> DefaultScope {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL =
          SearchScopes: HKU\S-1-5-19 -> DefaultScope {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL =
          SearchScopes: HKU\S-1-5-20 -> DefaultScope {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL =
          SearchScopes: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> DefaultScope {AFBCB7E0-F91A-4951-9F31-58FEE57A25C4} URL =
          SearchScopes: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> {02105F3B-F216-447F-A401-0B869860D48B} URL = hxxp://www.google.com/search?q={searchTerms}&r ... GB_nlBE532
          SearchScopes: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> {AAED2EBD-CF76-4681-92B1-ACD877AD72B2} URL = hxxp://nl.wikipedia.org/w/index.php?title=Speciaal:Zoeken&search={searchTerms}
          SearchScopes: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> {ADA95078-BE2C-4564-9832-FDC71E3385F4} URL = hxxp://rover.ebay.com/rover/1/1346-71133-23097-1/4?satitle={searchTerms}
          SearchScopes: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> {FB6A9BE0-EFBF-4B32-A716-DD9E29EEABE5} URL = hxxp://kopen.marktplaats.nl/search.php?q={searchTerms}&p={startPage?}
          BHO: Norton Identity Safety -> {602ADB0E-4AFF-4217-8AA1-95DAC4DFA408} -> C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\coIEPlg.dll [2018-05-30] (Symantec Corporation)
          BHO: Groove GFS Browser Helper -> {72853161-30C5-4D22-B7F9-0BBC1D38A37E} -> C:\Program Files\Microsoft Office\Office14\GROOVEEX.DLL [2013-12-19] (Microsoft Corporation)
          BHO: eID Extension -> {89D6D363-6550-47C1-B83F-2433F6844EC6} -> C:\Program Files (x86)\eid-ie\eidie64.dll [2018-03-26] ()
          BHO: avast! Online Security -> {8E5E2654-AD2D-48bf-AC2D-D17F00898D06} -> C:\Program Files\AVAST Software\Avast\aswWebRepIE64.dll [2018-06-10] (AVAST Software)
          BHO: Windows Live ID Sign-in Helper -> {9030D464-4C02-4ABF-8ECC-5164760863C6} -> C:\Program Files\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll [2012-07-17] (Microsoft Corp.)
          BHO: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
          BHO: Office Document Cache Handler -> {B4F3A835-0E21-4959-BA22-42B3008E02FF} -> C:\Program Files\Microsoft Office\Office14\URLREDIR.DLL [2013-03-06] (Microsoft Corporation)
          BHO-x32: HP Print Enhancer -> {0347C33E-8762-4905-BF09-768834316C61} -> C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_printenhancer.dll [2009-09-20] (Hewlett-Packard Co.)
          BHO-x32: Norton Identity Safety -> {602ADB0E-4AFF-4217-8AA1-95DAC4DFA408} -> C:\Program Files (x86)\Norton Security with Backup\Engine32\22.14.2.13\coIEPlg.dll [2018-05-30] (Symantec Corporation)
          BHO-x32: Groove GFS Browser Helper -> {72853161-30C5-4D22-B7F9-0BBC1D38A37E} -> C:\Program Files (x86)\Microsoft Office\Office14\GROOVEEX.DLL [2013-12-19] (Microsoft Corporation)
          BHO-x32: Java(tm) Plug-In SSV Helper -> {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} -> C:\Program Files (x86)\Java\jre1.8.0_171\bin\ssv.dll [2018-05-04] (Oracle Corporation)
          BHO-x32: Aanmeldhulp voor Microsoft-account -> {9030D464-4C02-4ABF-8ECC-5164760863C6} -> C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll [2012-07-17] (Microsoft Corp.)
          BHO-x32: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
          BHO-x32: Office Document Cache Handler -> {B4F3A835-0E21-4959-BA22-42B3008E02FF} -> C:\Program Files (x86)\Microsoft Office\Office14\URLREDIR.DLL [2013-03-06] (Microsoft Corporation)
          BHO-x32: Java(tm) Plug-In 2 SSV Helper -> {DBC80044-A445-435b-BC74-9C25C1C588A9} -> C:\Program Files (x86)\Java\jre1.8.0_171\bin\jp2ssv.dll [2018-05-04] (Oracle Corporation)
          BHO-x32: HP Smart BHO Class -> {FFFFFFFF-CF4E-4F2B-BDC2-0E72E116A856} -> C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_BHO.dll [2009-09-20] (Hewlett-Packard Co.)
          Toolbar: HKLM - Norton Toolbar - {7FEBEFE3-6B19-4349-98D2-FFB09D4B49CA} - C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\coIEPlg.dll [2018-05-30] (Symantec Corporation)
          Toolbar: HKLM - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
          Toolbar: HKLM-x32 - Norton Toolbar - {7FEBEFE3-6B19-4349-98D2-FFB09D4B49CA} - C:\Program Files (x86)\Norton Security with Backup\Engine32\22.14.2.13\coIEPlg.dll [2018-05-30] (Symantec Corporation)
          Toolbar: HKLM-x32 - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
          Toolbar: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> Norton Toolbar - {7FEBEFE3-6B19-4349-98D2-FFB09D4B49CA} - C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\coIEPlg.dll [2018-05-30] (Symantec Corporation)
          Toolbar: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> Google Toolbar - {2318C2B1-4965-11D4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
          DPF: HKLM-x32 {17492023-C23A-453E-A040-C7C580BBF700} hxxp://download.microsoft.com/download/E/5/6/E5611B10-0D6D-4117-8430-A67417AA88CD/LegitCheckControl.cab
          DPF: HKLM-x32 {73ECB3AA-4717-450C-A2AB-D00DAD9EE203} hxxp://h20270.www2.hp.com/ediags/gmn2/install/HPProductDetection2.cab
          DPF: HKLM-x32 {80AEEC0E-A2BE-4B8D-985F-350FE869DC40} hxxp://h20264.www2.hp.com/ediags/dd/install/HPDriverDiagnosticsVista.cab
          DPF: HKLM-x32 {E2883E8F-472F-4FB0-9522-AC9BF37916A7} hxxp://platformdl.adobe.com/NOS/getPlusPlus/1.6/gp.cabFireFox:
          ========
          FF HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\...\Firefox\Extensions: [smartwebprinting@hp.com] - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\MozillaAddOn3
          FF Extension: (HP Smart Web Printing) - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\MozillaAddOn3 [2010-09-26] [Verouderd] [ niet getekend]
          FF Plugin: @divx.com/DivX VOD Helper,version=1.0.0 -> C:\Program Files\DivX\DivX OVS Helper\npovshelper.dll [2011-06-20] (DivX, LLC.)
          FF Plugin: @microsoft.com/GENUINE -> disabled [Geen bestand]
          FF Plugin: @Microsoft.com/NpCtrl,version=1.0 -> C:\Program Files\Microsoft Silverlight\5.1.50907.0\npctrl.dll [2017-05-03] ( Microsoft Corporation)
          FF Plugin: @microsoft.com/OfficeAuthz,version=14.0 -> C:\PROGRA~1\MICROS~2\Office14\NPAUTHZ.DLL [2010-01-09] (Microsoft Corporation)
          FF Plugin: adobe.com/AdobeAAMDetect -> C:\Program Files (x86)\Common Files\Adobe\OOBE\PDApp\CCM\Utilities\npAdobeAAMDetect64.dll [Geen bestand]
          FF Plugin: adobe.com/AdobeAAMDetect_x86_64 -> C:\Program Files (x86)\Adobe\Adobe Creative Cloud\Utils\npAdobeAAMDetect64.dll [2014-10-15] (Adobe Systems)
          FF Plugin-x32: @divx.com/DivX Browser Plugin,version=1.0.0 -> C:\Program Files (x86)\DivX\DivX Plus Web Player\npdivx32.dll [2010-08-25] (DivX,Inc.)
          FF Plugin-x32: @divx.com/DivX VOD Helper,version=1.0.0 -> C:\Program Files (x86)\DivX\DivX OVS Helper\npovshelper.dll [2011-06-20] (DivX, LLC.)
          FF Plugin-x32: @Google.com/GoogleEarthPlugin -> C:\Program Files (x86)\Google\Google Earth\plugin\npgeplugin.dll [2010-09-01] (Google)
          FF Plugin-x32: @java.com/DTPlugin,version=11.171.2 -> C:\Program Files (x86)\Java\jre1.8.0_171\bin\dtplugin\npDeployJava1.dll [2018-05-04] (Oracle Corporation)
          FF Plugin-x32: @java.com/JavaPlugin,version=11.171.2 -> C:\Program Files (x86)\Java\jre1.8.0_171\bin\plugin2\npjp2.dll [2018-05-04] (Oracle Corporation)
          FF Plugin-x32: @microsoft.com/GENUINE -> disabled [Geen bestand]
          FF Plugin-x32: @Microsoft.com/NpCtrl,version=1.0 -> C:\Program Files (x86)\Microsoft Silverlight\5.1.50907.0\npctrl.dll [2017-05-03] ( Microsoft Corporation)
          FF Plugin-x32: @microsoft.com/OfficeAuthz,version=14.0 -> C:\PROGRA~2\MICROS~2\Office14\NPAUTHZ.DLL [2010-01-09] (Microsoft Corporation)
          FF Plugin-x32: @microsoft.com/SharePoint,version=14.0 -> C:\PROGRA~2\MICROS~2\Office14\NPSPWRAP.DLL [2010-03-24] (Microsoft Corporation)
          FF Plugin-x32: @microsoft.com/WLPG,version=16.4.3528.0331 -> C:\Program Files (x86)\Windows Live\Photo Gallery\NPWLPG.dll [2014-03-31] (Microsoft Corporation)
          FF Plugin-x32: @tools.google.com/Google Update;version=3 -> C:\Program Files (x86)\Google\Update\1.3.33.17\npGoogleUpdate3.dll [2018-05-18] (Google Inc.)
          FF Plugin-x32: @tools.google.com/Google Update;version=9 -> C:\Program Files (x86)\Google\Update\1.3.33.17\npGoogleUpdate3.dll [2018-05-18] (Google Inc.)
          FF Plugin-x32: @videolan.org/vlc,version=2.2.0 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2017-05-24] (VideoLAN)
          FF Plugin-x32: @videolan.org/vlc,version=2.2.1 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2017-05-24] (VideoLAN)
          FF Plugin-x32: @videolan.org/vlc,version=2.2.4 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2017-05-24] (VideoLAN)
          FF Plugin-x32: @videolan.org/vlc,version=2.2.6 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2017-05-24] (VideoLAN)
          FF Plugin-x32: Adobe Reader -> C:\Program Files (x86)\Adobe\Acrobat Reader DC\Reader\AIR\nppdf32.dll [2018-05-11] (Adobe Systems Inc.)
          FF Plugin-x32: adobe.com/AdobeAAMDetect -> C:\Program Files (x86)\Adobe\Adobe Creative Cloud\Utils\npAdobeAAMDetect32.dll [2014-10-15] (Adobe Systems)Chrome:
          =======
          CHR Profile: C:\Users\Gebruiker\AppData\Local\Google\Chrome\User Data\Default [2018-05-30]
          CHR Extension: (Docs) - C:\Users\Gebruiker\AppData\Local\Google\Chrome\User Data\Default\Extensions\aohghmighlieiainnegkcijnfilokake [2018-03-25]
          CHR Extension: (Google Drive) - C:\Users\Gebruiker\AppData\Local\Google\Chrome\User Data\Default\Extensions\apdfllckaahabafndbhieahigkjlhalf [2018-03-25]
          CHR Extension: (YouTube) - C:\Users\Gebruiker\AppData\Local\Google\Chrome\User Data\Default\Extensions\blpcfgokakmgnkcojhhkbfbldkacnbeo [2018-03-25]
          CHR Extension: (Gmail) - C:\Users\Gebruiker\AppData\Local\Google\Chrome\User Data\Default\Extensions\pjkljhegncpnkpknbcohdijeoejaedia [2018-03-25]
          CHR Extension: (Chrome Media Router) - C:\Users\Gebruiker\AppData\Local\Google\Chrome\User Data\Default\Extensions\pkedcjkdefgpdelpbcmbmeomcjbeemfm [2018-03-25]
          CHR HKLM\...\Chrome\Extension: [cjabmdjcfcfdmffimndhafhblfmpjdpe] - C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\Exts\Chrome.crx <niet gevonden>
          CHR HKLM\...\Chrome\Extension: [iikflkcanblccfahdhdonehdalibjnif] - hxxps://clients2.google.com/service/update2/crx
          CHR HKLM-x32\...\Chrome\Extension: [cjabmdjcfcfdmffimndhafhblfmpjdpe] - C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\Exts\Chrome.crx <niet gevonden>
          CHR HKLM-x32\...\Chrome\Extension: [iikflkcanblccfahdhdonehdalibjnif] - hxxps://clients2.google.com/service/update2/crx
          CHR HKLM-x32\...\Chrome\Extension: [nneajnkjbffgblleaoojgaacokifdkhm] - <geen Path/update_url>==================== Services (gefilterd) ====================(Als een item is opgenomen in de fixlist, wordt het uit het register verwijderd. Het bestand zal niet worden verplaatst tenzij apart vermeld.)R2 ACDaemon; C:\Program Files (x86)\Common Files\ArcSoft\Connection Service\Bin\ACService.exe [113152 2010-03-18] (ArcSoft Inc.)
          R2 Apple Mobile Device Service; C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe [83768 2017-11-27] (Apple Inc.)
          S3 aswbIDSAgent; C:\Program Files\AVAST Software\Avast\x64\aswidsagenta.exe [7620096 2018-06-10] (AVAST Software)
          R2 avast! Antivirus; C:\Program Files\AVAST Software\Avast\AvastSvc.exe [317280 2018-06-10] (AVAST Software)
          R3 hpqcxs08; C:\Program Files (x86)\HP\Digital Imaging\bin\hpqcxs08.dll [249344 2009-09-20] (Hewlett-Packard Co.) [Bestand niet getekend]
          R2 hpqddsvc; C:\Program Files (x86)\HP\Digital Imaging\bin\hpqddsvc.dll [133120 2009-09-20] (Hewlett-Packard Co.) [Bestand niet getekend]
          R2 HPSLPSVC; C:\Program Files (x86)\HP\Digital Imaging\bin\HPSLPSVC64.DLL [1039360 2010-10-22] (Hewlett-Packard Co.) [Bestand niet getekend]
          R2 HPSupportSolutionsFrameworkService; C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\HPSupportSolutionsFrameworkService.exe [332656 2018-05-02] (HP Inc.)
          R2 HPTouchpointAnalyticsService; C:\Program Files\HP\HP Touchpoint Analytics Client\TouchpointAnalyticsClientService.exe [332216 2017-11-22] (HP Inc.)
          R2 IJPLMSVC; C:\Program Files (x86)\Canon\IJPLM\IJPLMSVC.EXE [103808 2008-01-22] ()
          S3 LiveUpdate; C:\Program Files (x86)\Symantec\LiveUpdate\LuComServer_3_2.EXE [2999664 2007-09-12] (Symantec Corporation)
          S3 MBAMService; C:\Program Files\Malwarebytes\Anti-Malware\mbamservice.exe [6058960 2017-08-21] (Malwarebytes)
          R2 Net Driver HPZ12; C:\Windows\system32\HPZinw12.dll [71680 2010-08-06] (Hewlett-Packard) [Bestand niet getekend]
          R2 NortonSecurity; C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\NortonSecurity.exe [328648 2018-05-30] (Symantec Corporation)
          R2 Pml Driver HPZ12; C:\Windows\system32\HPZipm12.dll [89600 2010-08-06] (Hewlett-Packard) [Bestand niet getekend]
          R2 RapiMgr; C:\Windows\WindowsMobile\rapimgr.dll [225672 2007-05-31] (Microsoft Corporation)
          R2 ReflectService.exe; C:\Program Files\Macrium\Reflect\ReflectService.exe [3476432 2015-10-12] (Paramount Software UK Ltd)
          R2 RichVideo; C:\Program Files (x86)\CyberLink\Shared files\RichVideo.exe [271760 2009-04-15] ()
          R2 TeamViewer; C:\Program Files (x86)\TeamViewer\TeamViewer_Service.exe [7500048 2016-09-20] (TeamViewer GmbH)
          R2 TechSmith Uploader Service; C:\Program Files (x86)\Common Files\TechSmith Shared\Uploader\UploaderService.exe [3661096 2015-09-14] (TechSmith Corporation)
          R2 WcesComm; C:\Windows\WindowsMobile\wcescomm.dll [443784 2007-05-31] (Microsoft Corporation)
          S3 WinDefend; C:\Program Files\Windows Defender\mpsvc.dll [1011712 2013-05-27] (Microsoft Corporation)
          S3 Symantec SymSnap VSS Provider; C:\Windows\system32\dllhost.exe /Processid:{690284BC-CC0C-4FE9-820F-0D2186CEE77A}===================== Drivers (gefilterd) ======================(Als een item is opgenomen in de fixlist, wordt het uit het register verwijderd. Het bestand zal niet worden verplaatst tenzij apart vermeld.)R3 ACSSCR; C:\Windows\System32\DRIVERS\a38usb.sys [82480 2015-08-19] (Advanced Card Systems Ltd.)
          U5 AppMgmt; C:\Windows\system32\svchost.exe [27136 2009-07-14] (Microsoft Corporation) <==== AANDACHT (geen ServiceDLL)
          S3 aswArPot; C:\Windows\System32\drivers\aswArPot.sys [196640 2018-06-10] (AVAST Software)
          S3 aswbidsdriver; C:\Windows\System32\drivers\aswbidsdrivera.sys [227504 2018-06-10] (AVAST Software)
          S3 aswbidsh; C:\Windows\System32\drivers\aswbidsha.sys [199440 2018-06-10] (AVAST Software)
          S3 aswblog; C:\Windows\System32\drivers\aswbloga.sys [343752 2018-06-10] (AVAST Software)
          S3 aswbuniv; C:\Windows\System32\drivers\aswbuniva.sys [57680 2018-06-10] (AVAST Software)
          R1 aswHdsKe; C:\Windows\System32\drivers\aswHdsKe.sys [234560 2018-06-10] (AVAST Software)
          S3 aswHwid; C:\Windows\System32\drivers\aswHwid.sys [46968 2018-06-10] (AVAST Software)
          R2 aswMonFlt; C:\Windows\System32\drivers\aswMonFlt.sys [159120 2018-06-10] (AVAST Software)
          S3 aswRdr; C:\Windows\System32\drivers\aswRdr2.sys [111360 2018-06-10] (AVAST Software)
          R0 aswRvrt; C:\Windows\System32\drivers\aswRvrt.sys [85968 2018-06-10] (AVAST Software)
          S3 aswSnx; C:\Windows\System32\drivers\aswSnx.sys [1027720 2018-06-10] (AVAST Software)
          R1 aswSP; C:\Windows\System32\drivers\aswSP.sys [460520 2018-06-10] (AVAST Software)
          S3 aswStm; C:\Windows\System32\drivers\aswStm.sys [205976 2018-06-10] (AVAST Software)
          S3 aswVmm; C:\Windows\System32\drivers\aswVmm.sys [381552 2018-06-10] (AVAST Software)
          R1 BHDrvx64; C:\Program Files (x86)\Norton Security with Backup\NortonData\22.8.0.50\Definitions\BASHDefs\20180606.001\BHDrvx64.sys [1879632 2018-05-01] (Symantec Corporation)
          R1 ccSet_NGC; C:\Windows\system32\drivers\NGCx64\160E020.00D\ccSetx64.sys [187520 2018-05-30] (Symantec Corporation)
          R1 dtsoftbus01; C:\Windows\System32\DRIVERS\dtsoftbus01.sys [283064 2014-12-24] (Disc Soft Ltd)
          R1 eeCtrl; C:\Program Files (x86)\Common Files\Symantec Shared\EENGINE\eeCtrl64.sys [507984 2018-03-23] (Symantec Corporation)
          R3 EraserUtilRebootDrv; C:\Program Files (x86)\Common Files\Symantec Shared\EENGINE\EraserUtilRebootDrv.sys [153168 2018-03-24] (Symantec Corporation)
          R3 GenericMount; C:\Windows\System32\DRIVERS\GenericMount.sys [66608 2010-02-12] (Symantec Corporation)
          R1 IDSVia64; C:\Program Files (x86)\Norton Security with Backup\NortonData\22.8.0.50\Definitions\IPSDefs\20180611.061\IDSvia64.sys [1298000 2018-05-23] (Symantec Corporation)
          S3 MBAMSwissArmy; C:\Windows\System32\Drivers\mbamswissarmy.sys [252232 2018-06-10] (Malwarebytes)
          S3 pcouffin; C:\Windows\System32\Drivers\pcouffin.sys [82048 2011-11-06] (VSO Software) [Bestand niet getekend]
          S3 SQTECH905C; C:\Windows\System32\Drivers\Capt905c.sys [47680 2007-11-20] (Service & Quality Technology.)
          R1 SRTSP; C:\Windows\System32\Drivers\NGCx64\160E020.00D\SRTSP64.SYS [838224 2018-05-30] (Symantec Corporation)
          R1 SRTSPX; C:\Windows\system32\drivers\NGCx64\160E020.00D\SRTSPX64.SYS [49232 2018-05-30] (Symantec Corporation)
          R0 SymEFASI; C:\Windows\System32\drivers\NGCx64\160E020.00D\SYMEFASI64.SYS [1942096 2018-05-30] (Symantec Corporation)
          R3 SymEvent; C:\Windows\system32\Drivers\SYMEVENT64x86.SYS [99920 2018-06-09] (Symantec Corporation)
          R1 SymIRON; C:\Windows\system32\drivers\NGCx64\160E020.00D\Ironx64.SYS [307792 2018-05-30] (Symantec Corporation)
          R1 SymNetS; C:\Windows\System32\Drivers\NGCx64\160E020.00D\SYMNETS.SYS [566912 2018-05-30] (Symantec Corporation)
          R0 symsnap; C:\Windows\System32\DRIVERS\symsnap.sys [170032 2010-02-11] (StorageCraft)
          S1 UimBus; C:\Windows\System32\DRIVERS\UimBus.sys [102576 2015-08-21] ()
          S1 Uim_DEVIM; C:\Windows\System32\DRIVERS\uim_devim.sys [25904 2015-08-21] ()
          S1 Uim_IM; C:\Windows\System32\DRIVERS\uim_im.sys [701232 2015-08-21] ()
          S3 VProEventMonitor; C:\Windows\System32\DRIVERS\vproeventmonitor.sys [20528 2009-09-21] (Symantec Corporation)
          S3 wpCtrlDrv_NGC; C:\Windows\System32\Drivers\NGCx64\160E020.00D\wpCtrlDrv.sys [1015592 2018-05-30] (Symantec Corporation)
          U3 aswbdisk; geen ImagePath
          S3 NAVENG; \??\C:\Program Files (x86)\Norton Security with Backup\NortonData\22.8.0.50\Definitions\SDSDefs\20170324.018\ENG64.SYS [X]
          S3 NAVEX15; \??\C:\Program Files (x86)\Norton Security with Backup\NortonData\22.8.0.50\Definitions\SDSDefs\20170324.018\EX64.SYS [X]==================== NetSvcs (gefilterd) ===================(Als een item is opgenomen in de fixlist, wordt het uit het register verwijderd. Het bestand zal niet worden verplaatst tenzij apart vermeld.)
          ==================== Een Maand Aangemaakt bestanden en mappen ========(Als een item is opgenomen in de fixlist, word de map of het bestand verplaatst.)2018-06-12 16:34 - 2018-06-12 16:35 - 000024699 _____ C:\Users\Gebruiker\Desktop\FRST.txt
          2018-06-12 16:34 - 2018-06-12 16:34 - 000000000 ____D C:\FRST
          2018-06-12 16:33 - 2018-06-12 16:33 - 002413056 _____ (Farbar) C:\Users\Gebruiker\Desktop\FRST64.exe
          2018-06-12 15:08 - 2018-06-12 15:08 - 000000000 ____D C:\Windows\System32\Tasks\Remediation
          2018-06-11 16:56 - 2018-06-11 16:56 - 000001469 _____ C:\Users\Gebruiker\Desktop\SnagIt_handleiding - Snelkoppeling.lnk
          2018-06-10 14:25 - 2018-06-10 14:25 - 000002583 _____ C:\Users\Gebruiker\Desktop\Snagit 2018.lnk
          2018-06-10 14:21 - 2018-06-10 14:21 - 000000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\TechSmith
          2018-06-10 14:20 - 2018-06-10 14:20 - 000000000 ____D C:\ProgramData\ABBYY
          2018-06-10 14:20 - 2018-06-10 14:20 - 000000000 ____D C:\Program Files\TechSmith
          2018-06-10 14:20 - 2018-06-10 14:20 - 000000000 ____D C:\Program Files\Common Files\TechSmith Shared
          2018-06-10 12:53 - 2018-06-10 12:53 - 000099976 _____ C:\Users\Gebruiker\Documents\cc_20180610_125257.reg
          2018-06-10 12:45 - 2018-06-10 12:45 - 000001473 _____ C:\Users\Gebruiker\Desktop\adwcleaner_7.2.0 - Snelkoppeling.lnk
          2018-06-10 10:41 - 2018-06-10 10:41 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\AVAST Software
          2018-06-10 10:30 - 2018-06-10 10:40 - 000000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\AVAST Software
          2018-06-10 10:28 - 2018-06-10 10:28 - 000000000 ____D C:\Program Files\Common Files\AVAST Software
          2018-06-10 10:28 - 2018-06-10 10:27 - 001027720 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSnx.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000460520 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSP.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000381552 _____ (AVAST Software) C:\Windows\system32\Drivers\aswVmm.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000376536 _____ (AVAST Software) C:\Windows\system32\aswBoot.exe
          2018-06-10 10:28 - 2018-06-10 10:27 - 000343752 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbloga.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000234560 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHdsKe.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000227504 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsdrivera.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000205976 _____ (AVAST Software) C:\Windows\system32\Drivers\aswStm.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000199440 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsha.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000196640 _____ (AVAST Software) C:\Windows\system32\Drivers\aswArPot.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000159120 _____ (AVAST Software) C:\Windows\system32\Drivers\aswMonFlt.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000111360 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRdr2.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000085968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRvrt.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000057680 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbuniva.sys
          2018-06-10 10:28 - 2018-06-10 10:27 - 000046968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHwid.sys
          2018-06-10 10:26 - 2018-06-10 12:21 - 000000000 ____D C:\ProgramData\AVAST Software
          2018-06-10 10:26 - 2018-06-10 10:26 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\FrostWire 6
          2018-06-10 10:26 - 2018-06-10 10:26 - 000000000 ____D C:\Program Files\AVAST Software
          2018-06-09 12:22 - 2018-06-09 12:22 - 000003242 _____ C:\Windows\System32\Tasks\Norton WSC Integration
          2018-06-09 12:22 - 2018-06-09 12:22 - 000000000 ___RD C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Norton Security
          2018-06-05 15:45 - 2018-06-05 15:45 - 000001431 _____ C:\Users\Gebruiker\Desktop\HijackThis - Snelkoppeling.lnk
          2018-06-05 15:45 - 2018-06-05 15:45 - 000001399 _____ C:\Users\Gebruiker\Desktop\ComboFix - Snelkoppeling.lnk
          2018-06-05 15:45 - 2018-06-05 15:45 - 000001307 _____ C:\Users\Gebruiker\Desktop\JRT - Snelkoppeling.lnk
          2018-06-05 15:44 - 2018-06-05 15:44 - 000001343 _____ C:\Users\Gebruiker\Desktop\FRST64 - Snelkoppeling.lnk
          2018-06-05 15:42 - 2018-06-05 15:43 - 000000000 ___SD C:\ComboFix
          2018-06-05 15:42 - 2018-06-05 15:42 - 000000000 ____D C:\Qoobox
          2018-06-05 15:42 - 2011-06-26 08:45 - 000256000 _____ C:\Windows\PEV.exe
          2018-06-05 15:42 - 2010-11-07 19:20 - 000208896 _____ C:\Windows\MBR.exe
          2018-06-05 15:42 - 2009-04-20 06:56 - 000060416 _____ (NirSoft) C:\Windows\NIRCMD.exe
          2018-06-05 15:42 - 2000-08-31 02:00 - 000518144 _____ (SteelWerX) C:\Windows\SWREG.exe
          2018-06-05 15:42 - 2000-08-31 02:00 - 000406528 _____ (SteelWerX) C:\Windows\SWSC.exe
          2018-06-05 15:42 - 2000-08-31 02:00 - 000098816 _____ C:\Windows\sed.exe
          2018-06-05 15:42 - 2000-08-31 02:00 - 000080412 _____ C:\Windows\grep.exe
          2018-06-05 15:42 - 2000-08-31 02:00 - 000068096 _____ C:\Windows\zip.exe
          2018-06-05 15:41 - 2018-06-10 12:46 - 000000000 ____D C:\AdwCleaner
          2018-06-05 15:29 - 2018-06-05 15:29 - 000002128 _____ C:\Users\Gebruiker\Desktop\DiskInfo - Snelkoppeling.lnk
          2018-06-05 15:18 - 2018-06-05 15:20 - 000000968 _____ C:\Users\Gebruiker\Desktop\RegCleaner.lnk
          2018-06-05 15:18 - 2018-06-05 15:19 - 000000000 ____D C:\Program Files (x86)\RegCleaner
          2018-06-05 14:34 - 2018-06-05 14:34 - 000001693 _____ C:\Users\Gebruiker\Desktop\DelFix.txt
          2018-06-05 14:33 - 2018-06-05 15:39 - 000001254 _____ C:\DelFix.txt
          2018-06-05 09:56 - 2018-06-05 09:56 - 000012791 _____ C:\Users\Gebruiker\Documents\Smartcard.pdf
          2018-06-04 11:54 - 2018-06-04 11:31 - 000000255 _____ C:\Users\Gebruiker\Desktop\mypension.url
          2018-06-03 14:17 - 2018-06-03 14:17 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\Google
          2018-06-02 15:22 - 2018-06-02 15:22 - 000001786 _____ C:\Users\Gebruiker\Documents\revouninstallerpro.lic
          2018-06-02 15:19 - 2018-06-02 15:19 - 000001043 _____ C:\Users\Public\Desktop\Revo Uninstaller Pro.lnk
          2018-06-02 15:19 - 2018-06-02 15:19 - 000000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Revo Uninstaller Pro
          2018-06-02 15:19 - 2018-06-02 15:19 - 000000000 ____D C:\Program Files\VS Revo Group
          2018-06-02 15:19 - 2016-12-21 14:52 - 000040240 _____ (VS Revo Group) C:\Windows\system32\Drivers\revoflt.sys
          2018-06-02 15:09 - 2018-06-03 11:57 - 000000000 ____D C:\Users\Gebruiker\Downloads\Revo Uninstaller Pro 3.2.1 + Crack [CracksNow]
          2018-06-02 14:36 - 2018-06-02 14:36 - 000000000 ____D C:\Program Files (x86)\VS Revo Group
          2018-05-30 15:24 - 2016-12-16 16:35 - 000000265 _____ C:\Users\Gebruiker\Desktop\WeTransfer.url
          2018-05-29 12:41 - 2018-05-29 12:41 - 000000000 ____D C:\ProgramData\DirPrint
          2018-05-27 21:08 - 2018-05-27 21:08 - 000011392 _____ C:\Users\Gebruiker\Documents\startup2.txt
          2018-05-27 21:08 - 2018-05-27 21:08 - 000004498 _____ C:\Users\Gebruiker\Documents\startup3.txt
          2018-05-27 17:43 - 2018-05-27 17:43 - 000010070 _____ C:\Users\Gebruiker\Documents\startup1.txt
          2018-05-27 14:53 - 2018-05-27 14:54 - 000008630 _____ C:\Users\Gebruiker\Documents\cc_20180527_145355.reg
          2018-05-27 14:49 - 2018-05-27 14:49 - 000003870 _____ C:\Windows\System32\Tasks\CCleaner Update
          2018-05-27 14:49 - 2018-05-27 14:49 - 000002806 _____ C:\Windows\System32\Tasks\CCleanerSkipUAC
          2018-05-27 14:49 - 2018-05-27 14:49 - 000000788 _____ C:\Users\Public\Desktop\CCleaner.lnk
          2018-05-27 14:49 - 2018-05-27 14:49 - 000000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\CCleaner
          2018-05-27 14:49 - 2018-05-27 14:49 - 000000000 ____D C:\Program Files\CCleaner==================== Een Maand Gewijzigd bestanden en mappen ========(Als een item is opgenomen in de fixlist, word de map of het bestand verplaatst.)2018-06-12 14:51 - 2009-07-14 06:45 - 000023392 ____H C:\Windows\system32\7B296FB0-376B-497e-B012-9C450E1B7327-5P-1.C7483456-A289-439d-8115-601632D005A0
          2018-06-12 14:51 - 2009-07-14 06:45 - 000023392 ____H C:\Windows\system32\7B296FB0-376B-497e-B012-9C450E1B7327-5P-0.C7483456-A289-439d-8115-601632D005A0
          2018-06-12 14:42 - 2009-07-14 07:08 - 000000006 ____H C:\Windows\Tasks\SA.DAT
          2018-06-12 12:04 - 2011-11-10 18:36 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\vlc
          2018-06-12 12:00 - 2014-12-28 15:26 - 000000500 _____ C:\Windows\Tasks\VSO Software Updater.job
          2018-06-12 11:33 - 2016-09-11 10:44 - 000000000 ____D C:\Users\Gebruiker\AppData\Local\Adobe
          2018-06-11 16:36 - 2011-08-01 17:13 - 000003990 _____ C:\Windows\System32\Tasks\User_Feed_Synchronization-{35B2A9F9-F47D-4B3F-AD5C-DC15C13DB198}
          2018-06-10 14:22 - 2018-01-07 11:19 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\TechSmith
          2018-06-10 14:20 - 2015-07-26 10:33 - 000000000 ____D C:\ProgramData\TechSmith
          2018-06-10 14:19 - 2014-12-24 15:57 - 000000000 ____D C:\ProgramData\Package Cache
          2018-06-10 14:09 - 2009-07-14 11:16 - 000745764 _____ C:\Windows\system32\perfh013.dat
          2018-06-10 14:09 - 2009-07-14 11:16 - 000153716 _____ C:\Windows\system32\perfc013.dat
          2018-06-10 14:09 - 2009-07-14 07:13 - 001670960 _____ C:\Windows\system32\PerfStringBackup.INI
          2018-06-10 14:09 - 2009-07-14 05:20 - 000000000 ____D C:\Windows\inf
          2018-06-10 13:29 - 2015-04-02 14:16 - 001026048 ___SH C:\Users\Gebruiker\Desktop\Thumbs.db
          2018-06-10 13:00 - 2017-10-24 12:01 - 000252232 _____ (Malwarebytes) C:\Windows\system32\Drivers\mbamswissarmy.sys
          2018-06-10 13:00 - 2010-09-15 15:51 - 000000000 ____D C:\Users\Gebruiker\AppData\Local\CrashDumps
          2018-06-10 12:51 - 2016-10-23 17:12 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\uTorrent
          2018-06-10 12:51 - 2015-11-01 10:50 - 000000000 ____D C:\Program Files (x86)\TeamViewer
          2018-06-10 10:27 - 2012-01-11 13:29 - 000000000 ____D C:\Users\Gebruiker\.frostwire5
          2018-06-10 10:26 - 2017-10-13 10:39 - 000001229 _____ C:\Users\Gebruiker\Desktop\FrostWire 6.lnk
          2018-06-10 10:26 - 2017-03-10 17:31 - 000000000 ____D C:\Program Files (x86)\FrostWire 6
          2018-06-10 09:35 - 2017-11-17 17:15 - 000000348 _____ C:\Windows\Tasks\HPCeeScheduleForGebruiker.job
          2018-06-09 12:52 - 2015-06-13 09:52 - 000000000 ____D C:\Program Files\Common Files\AV
          2018-06-09 12:33 - 2016-12-14 13:04 - 000003210 _____ C:\Windows\System32\Tasks\HPCeeScheduleForGebruiker
          2018-06-09 12:29 - 2018-04-16 09:11 - 000000000 ____D C:\Windows\System32\Tasks\Norton Security with Backup
          2018-06-09 12:22 - 2018-02-01 14:59 - 000000000 ____D C:\Windows\system32\Drivers\NGCx64
          2018-06-09 12:22 - 2017-03-25 11:02 - 000099920 _____ (Symantec Corporation) C:\Windows\system32\Drivers\SYMEVENT64x86.SYS
          2018-06-09 12:22 - 2017-03-25 11:02 - 000010396 _____ C:\Windows\system32\Drivers\SYMEVENT64x86.CAT
          2018-06-07 16:40 - 2012-08-26 13:52 - 000004422 _____ C:\Windows\System32\Tasks\Adobe Flash Player Updater
          2018-06-07 16:39 - 2012-08-26 13:52 - 000842240 _____ (Adobe Systems Incorporated) C:\Windows\SysWOW64\FlashPlayerApp.exe
          2018-06-07 16:39 - 2011-11-21 12:17 - 000000000 ____D C:\Windows\system32\Macromed
          2018-06-07 16:39 - 2011-05-18 13:14 - 000175104 _____ (Adobe Systems Incorporated) C:\Windows\SysWOW64\FlashPlayerCPLApp.cpl
          2018-06-07 16:39 - 2010-09-07 15:54 - 000000000 ____D C:\Windows\SysWOW64\Macromed
          2018-06-05 09:49 - 2010-09-07 14:16 - 000000000 ____D C:\Users\Gebruiker
          2018-06-03 14:17 - 2010-09-18 10:40 - 000000000 ____D C:\Users\Gebruiker\AppData\Local\Google
          2018-06-02 15:06 - 2018-04-14 10:36 - 000000000 ____D C:\Users\Gebruiker\AppData\LocalLow\uTorrent
          2018-05-30 12:31 - 2010-11-01 12:44 - 000000000 ____D C:\Users\Gebruiker\AppData\LocalLow\Temp
          2018-05-25 11:57 - 2010-10-22 10:51 - 000000000 ____D C:\Users\Gebruiker\AppData\Local\Windows Live
          2018-05-18 16:10 - 2017-08-25 13:32 - 000003490 _____ C:\Windows\System32\Tasks\GoogleUpdateTaskMachineUA
          2018-05-18 16:10 - 2017-08-25 13:32 - 000003362 _____ C:\Windows\System32\Tasks\GoogleUpdateTaskMachineCore
          2018-05-18 10:45 - 2015-05-04 11:33 - 000004476 _____ C:\Windows\System32\Tasks\Adobe Acrobat Update Task
          2018-05-18 10:44 - 2015-05-04 11:32 - 000002441 _____ C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Acrobat Reader DC.lnk==================== Bestanden in de root van sommige mappen =======2017-01-21 13:59 - 2017-01-21 13:59 - 000011114 _____ () C:\ProgramData\MainApp.dll
          2011-01-10 18:25 - 2012-09-09 15:45 - 000000157 _____ () C:\Users\Gebruiker\AppData\Roaming\default.rss
          2011-11-06 10:49 - 2011-11-06 10:49 - 000093696 _____ () C:\Users\Gebruiker\AppData\Roaming\ezpinst.exe
          2015-03-20 16:25 - 2016-11-13 11:44 - 000099384 _____ () C:\Users\Gebruiker\AppData\Roaming\inst.exe
          2010-09-13 14:51 - 2016-11-13 11:44 - 000007859 _____ () C:\Users\Gebruiker\AppData\Roaming\pcouffin.cat
          2010-09-13 14:51 - 2016-11-13 11:44 - 000001167 _____ () C:\Users\Gebruiker\AppData\Roaming\pcouffin.inf
          2010-09-13 14:51 - 2016-11-13 11:44 - 000000055 _____ () C:\Users\Gebruiker\AppData\Roaming\pcouffin.log
          2010-09-13 14:51 - 2016-11-13 11:44 - 000082816 _____ (VSO Software) C:\Users\Gebruiker\AppData\Roaming\pcouffin.sys
          2010-09-12 10:05 - 2010-09-12 10:05 - 000033134 _____ () C:\Users\Gebruiker\AppData\Roaming\UserTile.png
          2015-06-07 09:51 - 2015-06-07 09:52 - 000001057 _____ () C:\Users\Gebruiker\AppData\Roaming\vso_ts_preview.xml
          2016-07-24 11:08 - 2016-07-24 11:08 - 000003584 _____ () C:\Users\Gebruiker\AppData\Local\DCBC2A71-70D8-4DAN-EHR8-E0D61DEA3FDF.ini
          2008-02-05 13:28 - 2008-02-05 13:28 - 000000051 _____ () C:\Users\Gebruiker\AppData\Local\setup.txt==================== Bamital & volsnap ======================(Er is geen automatische fix voor bestanden die de verificatie niet doorkomen.)C:\Windows\system32\winlogon.exe => Bestand is getekend
          C:\Windows\system32\wininit.exe => Bestand is getekend
          C:\Windows\SysWOW64\wininit.exe => Bestand is getekend
          C:\Windows\explorer.exe => Bestand is getekend
          C:\Windows\SysWOW64\explorer.exe => Bestand is getekend
          C:\Windows\system32\svchost.exe => Bestand is getekend
          C:\Windows\SysWOW64\svchost.exe => Bestand is getekend
          C:\Windows\system32\services.exe => Bestand is getekend
          C:\Windows\system32\User32.dll => Bestand is getekend
          C:\Windows\SysWOW64\User32.dll => Bestand is getekend
          C:\Windows\system32\userinit.exe => Bestand is getekend
          C:\Windows\SysWOW64\userinit.exe => Bestand is getekend
          C:\Windows\system32\rpcss.dll => Bestand is getekend
          C:\Windows\system32\dnsapi.dll => Bestand is getekend
          C:\Windows\SysWOW64\dnsapi.dll => Bestand is getekend
          C:\Windows\system32\Drivers\volsnap.sys => Bestand is getekendLastRegBack: 2018-06-09 14:47==================== Eind van FRST.txt ============================
          Intel Core i5-661/3,33GHz ; 2x2GB ; Windows 7 Home Premium 64 bit ; Microsoft Office 2010 Professional Plus ; HD1=500GB ; HD2=160GB ; Norton Security 5 ; CCleaner ; Malwarebytes Anti-Malware ;Windows Live Mail 2012.

            Citeer
            WillyV Startte dit onderwerp 12 jun 2018, 16:45 2030 Antwerpen 645 berichten
            abbs,


            Het logje van Addition.txt

            Extra scanresultaten van Farbar Recovery Scan Tool (x64) Versie: 06.06.2018 01
            Gestart door Gebruiker (12-06-2018 16:35:31)
            Gestart vanaf C:\Users\Gebruiker\Desktop
            Windows 7 Home Premium Service Pack 1 (X64) (2010-09-07 12:16:48)
            Boot Modus: Normal
            ==========================================================
            ==================== Accounts: =============================Administrator (S-1-5-21-3233923740-3587472772-2755484448-500 - Administrator - Disabled)
            Gast (S-1-5-21-3233923740-3587472772-2755484448-501 - Limited - Disabled)
            Gebruiker (S-1-5-21-3233923740-3587472772-2755484448-1000 - Administrator - Enabled) => C:\Users\Gebruiker
            HomeGroupUser$ (S-1-5-21-3233923740-3587472772-2755484448-1002 - Limited - Enabled)==================== Security Center ========================(Als een item is opgenomen in de fixlist, zal het worden verwijderd.)AV: Avast Antivirus (Disabled - Up to date) {8EA8924E-BC81-DC44-8BB0-8BAE75D86EBF}
            AV: Norton Security Online (Enabled - Up to date) {E3FDBD9F-8140-1400-F32B-8B58923F7C4D}
            AS: Norton Security Online (Enabled - Up to date) {589C5C7B-A77A-1B8E-C99B-B02AE9B836F0}
            AS: Windows Defender (Disabled - Out of date) {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
            AS: Avast Antivirus (Disabled - Up to date) {35C973AA-9ABB-D3CA-B100-B0DC0E5F2402}
            FW: Norton Security Online (Enabled) {DBC63CBA-CB2F-1558-D874-226D6CEC3B36}==================== Geïnstalleerde programma's ======================(Alleen de adware-programma's met 'verborgen' vlag kunnen worden toegevoegd aan de fixlist om ze zichtbaar te maken. De adware-programma's moeten handmatig gedeïnstalleerd worden.)µTorrent (HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\...\uTorrent) (Version: 3.4.9.43085 - BitTorrent Inc.)
            64 Bit HP CIO Components Installer (HKLM\...\{FF21C3E6-97FD-474F-9518-8DCBE94C2854}) (Version: 7.2.8 - Hewlett-Packard) Hidden
            Adobe Acrobat Reader DC - Nederlands (HKLM-x32\...\{AC76BA86-7AD7-1043-7B44-AC0F074E4100}) (Version: 18.011.20040 - Adobe Systems Incorporated)
            Adobe Creative Cloud (HKLM-x32\...\Adobe Creative Cloud) (Version: 2.8.1.451 - Adobe Systems Incorporated)
            Adobe Flash Player 30 ActiveX (HKLM-x32\...\Adobe Flash Player ActiveX) (Version: 30.0.0.113 - Adobe Systems Incorporated)
            Adobe Photoshop CC 2014 (HKLM-x32\...\{D7A4F897-B20A-42D0-862D-CB5F6DB7391D}) (Version: 15.0 - Adobe Systems Incorporated)
            AIO_CDA_ProductContext (HKLM-x32\...\{2A7EF808-14F3-4E93-BE3A-1675EE5332A4}) (Version: 130.0.365.000 - Hewlett-Packard) Hidden
            AIO_CDA_Software (HKLM-x32\...\{A7AEE29F-839E-46B5-B347-6D430618129F}) (Version: 130.0.365.000 - Hewlett-Packard) Hidden
            AIO_Scan (HKLM-x32\...\{D86B0E2E-DF9A-441C-AF77-8D1A0FF00FA6}) (Version: 130.0.365.000 - Hewlett-Packard) Hidden
            Any DVD Cloner Platinum 1.1.2 (HKLM-x32\...\Any DVD Cloner Platinum_is1) (Version:  - dvdsmith.com)
            Apple Application Support (32-bit) (HKLM-x32\...\{BC7C46A4-D7A7-48EC-A98C-32A7762B5EFA}) (Version: 6.2.1 - Apple Inc.)
            Apple Application Support (64-bit) (HKLM\...\{F0C4B709-8BF4-4A72-B527-12E7BF5482F8}) (Version: 6.2.1 - Apple Inc.)
            Apple Mobile Device Support (HKLM\...\{BD6778C5-6FA5-492A-ADD6-E706339C2A7B}) (Version: 11.0.2.4 - Apple Inc.)
            Apple Software Update (HKLM-x32\...\{C1BBFD2A-BCDD-45B3-8C0B-66BD434970A8}) (Version: 2.4.8.1 - Apple Inc.)
            ArcSoft PhotoImpression 6 (HKLM-x32\...\{D56401D6-E356-4CA5-97A3-024D666F5E5C}) (Version: 6.1.7.129 - ArcSoft)
            Belgium e-ID middleware 4.2.8 (build 3252) (HKLM\...\{DB942AEA-93D6-4FE4-8862-180D35A73252}) (Version: 4.2.3252 - Belgian Government)
            Bonjour (HKLM\...\{56DDDFB8-7F79-4480-89D5-25E1F52AB28F}) (Version: 3.1.0.1 - Apple Inc.)
            BufferChm (HKLM-x32\...\{2EEA7AA4-C203-4b90-A34F-19FB7EF1C81C}) (Version: 130.0.331.000 - Hewlett-Packard) Hidden
            C4100 (HKLM-x32\...\{B6916E4B-FD07-47E7-B906-B3F734F08E29}) (Version: 130.0.365.000 - Hewlett-Packard) Hidden
            c4100_Help (HKLM-x32\...\{3260D61B-DCA6-4ec6-8A41-DCCE01BC6EE4}) (Version: 82.0.256.000 - Hewlett-Packard) Hidden
            CCleaner (HKLM\...\CCleaner) (Version: 5.43 - Piriform)
            CDBurnerXP (HKLM\...\{7E265513-8CDA-4631-B696-F40D983F3B07}_is1) (Version: 4.5.4.5306 - CDBurnerXP)
            CloneDVD 4.1.0.23 (HKLM-x32\...\MainApp.exe_is1) (Version:  - Copyright (C) 2003-2007 DVD X Studios.)
            Copy (HKLM-x32\...\{3C92B2E6-380D-4fef-B4DF-4A3B4B669771}) (Version: 130.0.428.000 - Hewlett-Packard) Hidden
            Corel Graphics - Windows Shell Extension (HKLM\...\_{3CAAE169-6001-48ED-B2C6-5B6F511552FD}) (Version: 18.0.0.448 - Corel Corporation)
            Corel Graphics - Windows Shell Extension (HKLM\...\{3CAAE169-6001-48ED-B2C6-5B6F511552FD}) (Version: 18.0.448 - Corel Corporation) Hidden
            Corel Graphics - Windows Shell Extension 32 Bit Keys (HKLM\...\{C8730B1A-133D-4546-8E21-9EC186341F20}) (Version: 18.0.448 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Capture (HKLM-x32\...\{7F05E704-30A6-421A-97A7-8EEB1C7FF012}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Content (HKLM-x32\...\{7F05E704-30A6-421A-97A7-8EEB1C7FF016}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Draw (HKLM-x32\...\{7F05E704-30A6-421A-97A7-8EEB1C7FF013}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Filters (HKLM-x32\...\{7F05E704-30A6-421A-97A7-8EEB1C7FF017}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - FontNav (HKLM-x32\...\{7F05E704-30A6-421A-97A7-8EEB1C7FF019}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - IPM (HKLM-x32\...\{9D0798D0-AF6C-4E62-94B1-AEBF1A43E00A}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Lang BR (HKLM-x32\...\{1A9DAB4D-46CD-4CBF-A9FC-28D8AA8D2FCF}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Lang DE (HKLM-x32\...\{AEFBAC58-2DDD-4CEF-BDFD-52A5A5F432ED}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Lang EN (HKLM-x32\...\{7F05E704-30A6-421A-97A7-8EEB1C7FF100}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Lang ES (HKLM-x32\...\{D2827848-7D2A-4547-9AD1-C965FB3E6344}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Lang FR (HKLM-x32\...\{9D306690-3173-42CD-94C6-9EF9318AF24B}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Lang IT (HKLM-x32\...\{D0160DD3-6F62-4F1E-B999-6C68D3AE7390}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - Lang NL (HKLM-x32\...\{A6C27FFF-75EF-4B5B-A64E-F9E128994908}) (Version: 14.0 - Uw bedrijfsnaam) Hidden
            CorelDRAW Graphics Suite X4 - PP (HKLM-x32\...\{7F05E704-30A6-421A-97A7-8EEB1C7FF014}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 - VBA (HKLM-x32\...\{BF439B41-0252-48DE-8B8B-0430CB26A181}) (Version: 14.0 - Corel Corporation) Hidden
            CorelDRAW Graphics Suite X4 (HKLM-x32\...\{44A27085-0616-4181-A0C3-81C7ECA17F73}) (Version: 14.0 - Corel Corporation) Hidden
            D3DX10 (HKLM-x32\...\{E09C4DB7-630C-4F06-A631-8EA7239923AF}) (Version: 15.4.2368.0902 - Microsoft) Hidden
            Destinations (HKLM-x32\...\{BD7204BA-DD64-499E-9B55-6A282CDF4FA4}) (Version: 140.0.77.000 - Hewlett-Packard) Hidden
            DeviceDiscovery (HKLM-x32\...\{2FF8C687-DB7D-4adc-A5DC-57983EC25046}) (Version: 130.0.465.000 - Hewlett-Packard) Hidden
            DivX Setup (HKLM-x32\...\DivX Setup) (Version: 2.6.0.34 - DivX, LLC)
            DocProc (HKLM-x32\...\{9B362566-EC1B-4700-BB9C-EC661BDE2175}) (Version: 13.0.0.0 - Hewlett-Packard) Hidden
            eID Internet Explorer plugin 1.0.5 (HKLM-x32\...\eid-ie) (Version: 1.0.5 - e-Contract.be BVBA)
            Fax (HKLM-x32\...\{440B915A-0C85-45DB-92AE-75AE14704A64}) (Version: 130.0.418.000 - Hewlett-Packard) Hidden
            FrostWire 6.6.7 (HKLM-x32\...\FrostWire 6) (Version: 6.6.7.259 - FrostWire LLC)
            Gadwin PrintScreen (64-Bit) (HKLM\...\{819A52E1-0929-469A-BEB6-1AEBE0873CFC}) (Version: 5.4.2.0 - Gadwin Systems)
            Gadwin PrintScreen (HKLM-x32\...\Gadwin PrintScreen) (Version: 4.4 - Gadwin Systems, Inc.)
            Ghostscript GPL 8.64 (Msi Setup) (HKLM-x32\...\_{06CD45E6-FF5E-4D8E-BC01-B276A90DADF2}) (Version: 8.64 - Corel Corporation)
            Ghostscript GPL 8.64 (Msi Setup) (HKLM-x32\...\{06CD45E6-FF5E-4D8E-BC01-B276A90DADF2}) (Version: 8.64 - Corel Corporation) Hidden
            Google Earth (HKLM-x32\...\{4286E640-B5FB-11DF-AC4B-005056C00008}) (Version: 5.2.1.1588 - Google)
            Google Toolbar for Internet Explorer (HKLM-x32\...\{18455581-E099-4BA8-BC6B-F34B2F06600C}) (Version: 1.0.0 - Google Inc.) Hidden
            Google Toolbar for Internet Explorer (HKLM-x32\...\{2318C2B1-4965-11d4-9B18-009027A5CD4F}) (Version: 7.5.8231.2252 - Google Inc.)
            Google Update Helper (HKLM-x32\...\{60EC980A-BDA2-4CB6-A427-B07A5498B4CA}) (Version: 1.3.33.17 - Google Inc.) Hidden
            Google Update Helper (HKLM-x32\...\{A92DAB39-4E2C-4304-9AB6-BC44E68B55E2}) (Version: 1.3.21.169 - Google Inc.) Hidden
            GPBaseService2 (HKLM-x32\...\{63FF21C9-A810-464F-B60A-3111747B1A6D}) (Version: 130.0.371.000 - Hewlett-Packard) Hidden
            HP Customer Participation Program 13.0 (HKLM\...\HPExtendedCapabilities) (Version: 13.0 - HP)
            HP Driver Diagnostics (HKLM-x32\...\{0EC7C406-B592-4686-BAC1-AD29A85EAE6A}) (Version: 1.03.0005 - Hewlett-Packard Company)
            HP Dropbox Plugin (HKLM-x32\...\{2E5A25A3-C329-40FB-9A09-E2C75B746935}) (Version: 36.0.41.58587 - HP)
            HP Google Drive Plugin (HKLM-x32\...\{CF37027C-AA2E-46B8-B741-6205E001C4F4}) (Version: 36.0.41.58587 - HP)
            HP Imaging Device Functions 13.0 (HKLM\...\HP Imaging Device Functions) (Version: 13.0 - HP)
            HP Officejet 5740 series Basissoftware van het apparaat (HKLM\...\{26912E93-BB8C-4303-891C-87DBD3EF9C32}) (Version: 40.11.1135.17143 - HP Inc.)
            HP Officejet 5740 series Help (HKLM-x32\...\{9B49B742-F990-4501-AF0B-7DED35E46722}) (Version: 34.0.0 - Hewlett Packard)
            HP Photo Creations (HKLM-x32\...\HP Photo Creations) (Version: 1.0.0.7702 - HP)
            HP Photosmart All-In-One Driver Software 13.0 Rel. A (HKLM\...\{17016DA1-F040-4032-BD36-34DD317BC9D5}) (Version: 13.0 - HP)
            HP Photosmart Essential 3.5 (HKLM\...\HP Photosmart Essential) (Version: 3.5 - HP)
            HP Product Detection (HKLM-x32\...\{A436F67F-687E-4736-BD2B-537121A804CF}) (Version: 11.14.0001 - HP)
            HP Smart Web Printing 4.51 (HKLM\...\HP Smart Web Printing) (Version: 4.51 - HP)
            HP Solution Center 13.0 (HKLM\...\HP Solution Center & Imaging Support Tools) (Version: 13.0 - HP)
            HP Support Assistant (HKLM-x32\...\{4780AF24-213D-4187-86F2-0014A6D6077B}) (Version: 8.6.18.11 - HP Inc.)
            HP Support Solutions Framework (HKLM-x32\...\{FEC61634-7B6D-4859-83FD-DDF2E76570F9}) (Version: 12.9.18.3 - HP Inc.)
            HP Touchpoint Analytics Client (HKLM\...\{E5FB98E0-0784-44F0-8CEC-95CD4690C43F}) (Version: 4.0.2.1439 - HP Inc.)
            HP Update (HKLM-x32\...\{912D30CF-F39E-4B31-AD9A-123C6B794EE2}) (Version: 5.005.002.002 - Hewlett-Packard)
            HPDiagnosticAlert (HKLM-x32\...\{846B5DED-DC8C-4E1A-B5B4-9F5B39A0CACE}) (Version: 1.00.0000 - Microsoft) Hidden
            HPDiagnosticCoreDll (HKLM-x32\...\{9262B08F-E183-4FED-A2BD-23FF1A84EB79}) (Version: 1.0.15.0 - Hewlett Packard)
            HPPhotoGadget (HKLM-x32\...\{CAE4213F-F797-439D-BD9E-79B71D115BE3}) (Version: 130.0.282.000 - Hewlett-Packard) Hidden
            HPPhotoSmartDiscLabelContent1 (HKLM-x32\...\{681B698F-C997-42C3-B184-B489C6CA24C9}) (Version: 2.04.0000 - Hewlett-Packard) Hidden
            HPPhotosmartEssential (HKLM-x32\...\{D79113E7-274C-470B-BD46-01B10219DF6A}) (Version: 2.04.0000 - Hewlett-Packard) Hidden
            HPProductAssistant (HKLM-x32\...\{C43326F5-F135-4551-8270-7F7ABA0462E1}) (Version: 130.0.371.000 - Hewlett-Packard) Hidden
            HPSSupply (HKLM-x32\...\{6B2FFB21-AC88-45C3-9A7D-4BB3E744EC91}) (Version: 130.0.371.000 - Hewlett-Packard) Hidden
            I.R.I.S. OCR (HKLM-x32\...\{4A843560-44FA-4D79-9F11-BE95B588990F}) (Version: 12.3.7.0 - HP)
            I.R.I.S. OCR (HKLM-x32\...\{CA6BCA2F-EDEB-408F-850B-31404BE16A61}) (Version: 12.3.4.0 - HP)
            ImagXpress (HKLM-x32\...\{A8F2089B-1F79-4BF6-B385-A2C2B0B9A74D}) (Version: 7.0.74.0 - Nero AG) Hidden
            ImgBurn (HKLM-x32\...\ImgBurn) (Version: 2.5.8.0 - LIGHTNING UK!)
            Inkjet Printer/Scanner Extended Survey Program (HKLM-x32\...\CANONIJPLM100) (Version:  - )
            Intel(R) C++ Redistributables for Windows* on Intel(R) 64 (HKLM-x32\...\{D2437C5C-2D8C-40D2-8059-689AD7239FA3}) (Version: 11.1.048 - Intel Corporation)
            Intel(R) Control Center (HKLM-x32\...\{F8A9085D-4C7A-41a9-8A77-C8998A96C421}) (Version: 1.2.0.1006 - Intel Corporation)
            Intel(R) Graphics Media Accelerator Driver (HKLM-x32\...\{F0E3AD40-2BBD-4360-9C76-B9AC9A5886EA}) (Version: 8.15.10.1995 - Intel Corporation)
            Intel(R) Management Engine Components (HKLM-x32\...\{65153EA5-8B6E-43B6-857B-C6E4FC25798A}) (Version: 6.0.0.1179 - Intel Corporation)
            Intel(R) Network Connections 14.8.43.0 (HKLM\...\PROSetDX) (Version: 14.8.43.0 - Intel)
            iTunes (HKLM\...\{4CC2D6D2-E563-4C37-B009-80E7E455387F}) (Version: 12.7.2.60 - Apple Inc.)
            Java 8 Update 171 (HKLM-x32\...\{26A24AE4-039D-4CA4-87B4-2F32180171F0}) (Version: 8.0.1710.11 - Oracle Corporation)
            Junk Mail filter update (HKLM-x32\...\{0BE9E708-5DC0-4963-9CFD-0AA519090E79}) (Version: 16.4.3528.0331 - Microsoft Corporation) Hidden
            K-Lite Mega Codec Pack 7.1.0 (HKLM-x32\...\KLiteCodecPack_is1) (Version: 7.1.0 - )
            LAME v3.99.3 (for Windows) (HKLM-x32\...\LAME_is1) (Version:  - )
            LG CyberLink LabelPrint (HKLM-x32\...\{C59C179C-668D-49A9-B6EA-0121CCFC1243}) (Version: 2.5.2111 - CyberLink Corp.) Hidden
            LG CyberLink LabelPrint (HKLM-x32\...\InstallShield_{C59C179C-668D-49A9-B6EA-0121CCFC1243}) (Version: 2.5.2111 - CyberLink Corp.)
            LG CyberLink Power2Go (HKLM-x32\...\{40BF1E83-20EB-11D8-97C5-0009C5020658}) (Version: 6.2.3325 - CyberLink Corp.) Hidden
            LG CyberLink Power2Go (HKLM-x32\...\InstallShield_{40BF1E83-20EB-11D8-97C5-0009C5020658}) (Version: 6.2.3325 - CyberLink Corp.)
            LG CyberLink PowerBackup (HKLM-x32\...\{ADD5DB49-72CF-11D8-9D75-000129760D75}) (Version: 2.5.5529 - CyberLink Corp.)
            LG CyberLink PowerDVD (HKLM-x32\...\{2BF2E31F-B8BB-40A7-B650-98D28E0F7D47}) (Version: 8.0.2815d - CyberLink Corp.) Hidden
            LG CyberLink PowerDVD (HKLM-x32\...\InstallShield_{2BF2E31F-B8BB-40A7-B650-98D28E0F7D47}) (Version: 8.0.2815d - CyberLink Corp.)
            LG CyberLink PowerProducer (HKLM-x32\...\{B7A0CE06-068E-11D6-97FD-0050BACBF861}) (Version: 5.0.2.2130 - CyberLink Corp.) Hidden
            LG CyberLink PowerProducer (HKLM-x32\...\InstallShield_{B7A0CE06-068E-11D6-97FD-0050BACBF861}) (Version: 5.0.2.2130 - CyberLink Corp.)
            LG CyberLink YouCam (HKLM-x32\...\{01FB4998-33C4-4431-85ED-079E3EEFE75D}) (Version: 2.0.3123 - CyberLink Corp.) Hidden
            LG CyberLink YouCam (HKLM-x32\...\InstallShield_{01FB4998-33C4-4431-85ED-079E3EEFE75D}) (Version: 2.0.3123 - CyberLink Corp.)
            LG Power Tools (HKLM-x32\...\{1FBF6C24-C1FD-4101-A42B-0C564F9E8E79}) (Version: 6.0.3316 - CyberLink Corp.) Hidden
            LG Power Tools (HKLM-x32\...\InstallShield_{1FBF6C24-C1FD-4101-A42B-0C564F9E8E79}) (Version: 6.0.3316 - CyberLink Corp.)
            LiveUpdate 3.2 (Symantec Corporation) (HKLM-x32\...\LiveUpdate) (Version: 3.2.0.68 - Symantec Corporation)
            Macrium Reflect Free Edition (HKLM\...\{A163A86C-9EBB-4DCB-B02E-35CF63002F39}) (Version: 6.1.909 - Paramount Software (UK) Ltd.) Hidden
            Macrium Reflect Free Edition (HKLM\...\MacriumReflect) (Version: 6.1 - Paramount Software (UK) Ltd.)
            Malwarebytes versie 3.2.2.2018 (HKLM\...\{35065F43-4BB2-439A-BFF7-0F1014F2E0CD}_is1) (Version: 3.2.2.2018 - Malwarebytes)
            MarketResearch (HKLM-x32\...\{175F0111-2968-4935-8F70-33108C6A4DE3}) (Version: 130.0.374.000 - Hewlett-Packard) Hidden
            Microsoft .NET Framework 4.7 (HKLM\...\{92FB6C44-E685-45AD-9B20-CADF4CABA132} - 1033) (Version: 4.7.02053 - Microsoft Corporation)
            Microsoft .NET Framework 4.7 (Nederlands) (HKLM\...\{92FB6C44-E685-45AD-9B20-CADF4CABA132} - 1043) (Version: 4.7.02053 - Microsoft Corporation)
            Microsoft Office Professional Plus 2010 (HKLM-x32\...\Office14.PROPLUSR) (Version: 14.0.7015.1000 - Microsoft Corporation)
            Microsoft OneDrive (HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\...\OneDriveSetup.exe) (Version: 18.065.0329.0002 - Microsoft Corporation)
            Microsoft Silverlight (HKLM\...\{89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}) (Version: 5.1.50907.0 - Microsoft Corporation)
            Microsoft SQL Server 2005 Compact Edition [ENU] (HKLM-x32\...\{F0B430D1-B6AA-473D-9B06-AA3DD01FD0B8}) (Version: 3.1.0000 - Microsoft Corporation)
            Microsoft Visual C++ 2005 ATL Update kb973923 - x86 8.0.50727.4053 (HKLM-x32\...\{770657D0-A123-3C07-8E44-1C83EC895118}) (Version: 8.0.50727.4053 - Microsoft Corporation)
            Microsoft Visual C++ 2005 Redistributable (HKLM-x32\...\{710f4c1c-cc18-4c49-8cbf-51240c89a1a2}) (Version: 8.0.61001 - Microsoft Corporation)
            Microsoft Visual C++ 2005 Redistributable (HKLM-x32\...\{837b34e3-7c30-493c-8f6a-2b0f04e2912c}) (Version: 8.0.59193 - Microsoft Corporation)
            Microsoft Visual C++ 2008 Redistributable - KB2467174 - x86 9.0.30729.5570 (HKLM-x32\...\{86CE85E6-DBAC-3FFD-B977-E4B79F83C909}) (Version: 9.0.30729.5570 - Microsoft Corporation)
            Microsoft Visual C++ 2008 Redistributable - x64 9.0.30729.17 (HKLM\...\{8220EEFE-38CD-377E-8595-13398D740ACE}) (Version: 9.0.30729 - Microsoft Corporation)
            Microsoft Visual C++ 2008 Redistributable - x64 9.0.30729.6161 (HKLM\...\{5FCE6D76-F5DC-37AB-B2B8-22AB8CEDB1D4}) (Version: 9.0.30729.6161 - Microsoft Corporation)
            Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.4148 (HKLM-x32\...\{1F1C2DFC-2D24-3E06-BCB8-725134ADF989}) (Version: 9.0.30729.4148 - Microsoft Corporation)
            Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.6161 (HKLM-x32\...\{9BE518E6-ECC6-35A9-88E4-87755C07200F}) (Version: 9.0.30729.6161 - Microsoft Corporation)
            Microsoft Visual C++ 2010  x64 Redistributable - 10.0.40219 (HKLM\...\{1D8E6291-B0D5-35EC-8441-6616F567A0F7}) (Version: 10.0.40219 - Microsoft Corporation)
            Microsoft Visual C++ 2010  x86 Redistributable - 10.0.40219 (HKLM-x32\...\{F0C3E5D1-1ADE-321E-8167-68EF0DE699A5}) (Version: 10.0.40219 - Microsoft Corporation)
            Microsoft Visual C++ 2012 Redistributable (x64) - 11.0.61030 (HKLM-x32\...\{ca67548a-5ebe-413a-b50c-4b9ceb6d66c6}) (Version: 11.0.61030.0 - Microsoft Corporation)
            Microsoft Visual C++ 2012 Redistributable (x86) - 11.0.61030 (HKLM-x32\...\{33d1fd90-4274-48a1-9bc1-97e33d9c2d6f}) (Version: 11.0.61030.0 - Microsoft Corporation)
            Microsoft Visual Studio 2010 Tools for Office Runtime (x64) (HKLM\...\Microsoft Visual Studio 2010 Tools for Office Runtime (x64)) (Version: 10.0.50903 - Microsoft Corporation)
            Microsoft Visual Studio Tools for Applications 2.0 - ENU (HKLM-x32\...\{AA4A4B2C-0465-3CF8-BA76-27A027D8ACAB}) (Version: 9.0.30729 - Microsoft Corporation)
            Microsoft Visual Studio Tools for Applications 2.0 Runtime (HKLM-x32\...\{299C0434-4F4E-341F-A916-4E07AEB35E79}) (Version: 9.0.30729 - Microsoft Corporation)
            Microsoft Visual Studio Tools for Applications 2012 (HKLM-x32\...\{89ca2a32-2b52-4595-8dfd-6fe4757958d0}) (Version: 11.0.51108 - Microsoft Corporation)
            Microsoft Visual Studio Tools for Applications 2015 (HKLM-x32\...\{dd8b09df-3ef8-49f1-bd1a-65278435860b}) (Version: 14.0.23217 - Microsoft Corporation)
            Movie Maker (HKLM-x32\...\{DC5E5027-65E8-41CB-815C-9AAB48BFB8E2}) (Version: 16.4.3528.0331 - Microsoft Corporation) Hidden
            Movie Maker (HKLM-x32\...\{DD67BE4B-7E62-4215-AFA3-F123A800A389}) (Version: 16.4.3528.0331 - Microsoft Corporation) Hidden
            MSXML 4.0 SP2 (KB954430) (HKLM-x32\...\{86493ADD-824D-4B8E-BD72-8C5DCDC52A71}) (Version: 4.20.9870.0 - Microsoft Corporation)
            MSXML 4.0 SP2 (KB973688) (HKLM-x32\...\{F662A8E6-F4DC-41A2-901E-8C11F044BDEC}) (Version: 4.20.9876.0 - Microsoft Corporation)
            MSXML 4.0 SP2 Parser and SDK (HKLM-x32\...\{716E0306-8318-4364-8B8F-0CC4E9376BAC}) (Version: 4.20.9818.0 - Microsoft Corporation)
            Network64 (HKLM\...\{05EFBF37-0E52-4579-875C-7EEF0DFB4FCB}) (Version: 130.0.572.000 - Hewlett-Packard) Hidden
            Network64 (HKLM\...\{6BFAB6C1-6D46-46DB-A538-A269907C9F2F}) (Version: 140.0.221.000 - Hewlett-Packard) Hidden
            Norton Security Online (HKLM-x32\...\NGC) (Version: 22.14.2.13 - Symantec Corporation)
            OCR Software by I.R.I.S. 13.0 (HKLM\...\HPOCR) (Version: 13.0 - HP)
            OVT Scanner X86 (HKLM-x32\...\{6B566EFE-DC1D-471F-93DD-84832663F140}) (Version: 1.00.0000 - Uw bedrijfsnaam)
            Pacote de Idiomas do Microsoft Visual Studio Tools for Applications 2012 x64 Hosting Support - PTB (HKLM\...\{E237254B-36A1-3D27-815E-B37C13BE0796}) (Version: 11.0.51108 - Microsoft Corporation) Hidden
            Pacote de Idiomas do Microsoft Visual Studio Tools for Applications 2012 x86 Hosting Support - PTB (HKLM-x32\...\{03077B58-6ACF-32CA-B42A-EAA458C295A1}) (Version: 11.0.51108 - Microsoft Corporation) Hidden
            Patient HealthViewer  6.1.3 (HKLM-x32\...\2683-5993-8159-9128) (Version: 6.1.3 - Nationaal Intermutualistisch College)
            Productverbeteringsonderzoek voor HP Officejet 5740 series (HKLM\...\{6788471B-0871-403E-9822-087E62AE84BE}) (Version: 40.11.1135.17143 - HP Inc.)
            Realtek High Definition Audio Driver (HKLM-x32\...\{F132AF7F-7BCA-4EDE-8A7C-958108FE7DBC}) (Version: 6.0.1.5964 - Realtek Semiconductor Corp.)
            Revo Uninstaller Pro 3.2.1 (HKLM\...\{67579783-0FB7-4F7B-B881-E5BE47C9DBE0}_is1) (Version: 3.2.1 - VS Revo Group, Ltd.)
            Scan (HKLM-x32\...\{06A1D88C-E102-4527-AF70-29FFD7AF215A}) (Version: 140.0.80.000 - Hewlett-Packard) Hidden
            Service Pack 2 for Microsoft Office 2010 (KB2687455) 32-Bit Edition (HKLM-x32\...\{91140000-0011-0000-0000-0000000FF1CE}_Office14.PROPLUSR_{DE28B448-32E8-4E8F-84F0-A52B21A49B5B}) (Version:  - Microsoft)
            Shop for HP Supplies (HKLM\...\Shop for HP Supplies) (Version: 13.0 - HP)
            SmartWebPrinting (HKLM-x32\...\{DC635845-46D3-404B-BCB1-FC4A91091AFA}) (Version: 130.0.457.000 - Hewlett-Packard) Hidden
            Snagit 2018 (HKLM\...\{4B41B2EC-8221-46AE-A787-AE8737506065}) (Version: 18.0.0 - TechSmith Corporation) Hidden
            Snagit 2018 (HKLM-x32\...\{74cae71f-2e10-4e7e-b3e2-945d9096a6f5}) (Version: 18.0.0.462 - TechSmith Corporation)
            SolutionCenter (HKLM-x32\...\{4A70EF07-7F88-4434-BB61-D1DE8AE93DD4}) (Version: 130.0.373.000 - Hewlett-Packard) Hidden
            Spelling Dictionaries Support For Adobe Reader 9 (HKLM-x32\...\{AC76BA86-7AD7-5464-3428-900000000004}) (Version: 9.0.0 - Adobe Systems Incorporated)
            Status (HKLM-x32\...\{0EF5BEA9-B9D3-46d7-8958-FB69A0BAEACC}) (Version: 130.0.469.000 - Hewlett-Packard) Hidden
            Stuurprogrammapakket voor Windows - Fedict SmartCard  (08/08/2015 4.1.5) (HKLM\...\9F46F7AB1E3B1B5F5482EA8D97F401B04FBF7958) (Version: 08/08/2015 4.1.5 - Fedict)
            Taalpakket voor Microsoft Visual Studio 2010 Tools for Office Runtime (x64) - NLD (HKLM\...\Microsoft Visual Studio 2010 Tools for Office Runtime (x64) Language Pack - NLD) (Version: 10.0.50903 - Microsoft Corporation)
            TeamViewer 11 (HKLM-x32\...\TeamViewer) (Version: 11.0.66695 - TeamViewer)
            Toolbox (HKLM-x32\...\{6BBA26E9-AB03-4FE7-831A-3535584CA002}) (Version: 130.0.648.000 - Hewlett-Packard) Hidden
            TrayApp (HKLM-x32\...\{1EC71BFB-01A3-4239-B6AF-B1AE656B15C0}) (Version: 130.0.422.000 - Hewlett-Packard) Hidden
            UnloadSupport (HKLM-x32\...\{4E7C28C7-D5DA-4E9F-A1CA-60490B54AE35}) (Version: 11.0.0 - Hewlett-Packard) Hidden
            Update voor het stuurprogramma voor Windows Mobile Apparaatcentrum (HKLM\...\{92DBCA36-9B41-4DD1-941A-AED149DD37F0}) (Version: 6.1.6965.0 - Microsoft Corporation)
            VC80CRTRedist - 8.0.50727.6195 (HKLM-x32\...\{933B4015-4618-4716-A828-5289FC03165F}) (Version: 1.2.0 - DivX, Inc) Hidden
            VLC media player (HKLM-x32\...\VLC media player) (Version: 2.2.6 - VideoLAN)
            VSO ConvertXToDVD 6 (HKLM-x32\...\{8FC36FA6-C508-44FB-B137-1CB46D8258B2}_is1) (Version: 6.0.0.75 - VSO Software)
            WebReg (HKLM-x32\...\{43CDF946-F5D9-4292-B006-BA0D92013021}) (Version: 130.0.132.017 - Hewlett-Packard) Hidden
            Windows Live Essentials (HKLM-x32\...\WinLiveSuite) (Version: 16.4.3528.0331 - Microsoft Corporation)
            Windows Mobile Apparaatcentrum (HKLM\...\{626672CD-BFCF-49A9-AEFE-AB0FED3BFC5B}) (Version: 6.1.6965.0 - Microsoft Corporation)
            WinRAR 4.20 (64-bit) (HKLM\...\WinRAR archiver) (Version: 4.20.0 - win.rar GmbH)
            Языковой пакет для поддержки размещения набора средств Microsoft Visual Studio Tools для работы с приложениями 2012 (x64) - RUS (HKLM\...\{25FB53C5-BE4C-3B6C-A0C9-D49A39227E1E}) (Version: 11.0.51108 - Microsoft Corporation) Hidden
            Языковой пакет для поддержки размещения набора средств Microsoft Visual Studio Tools для работы с приложениями 2012 (x86) - RUS (HKLM-x32\...\{68DC347D-C1C0-3DE2-A53E-CCC71DA53E57}) (Version: 11.0.51108 - Microsoft Corporation) Hidden==================== Aangepaste CLSID (gefilterd): ==========================(Als een item is opgenomen in de fixlist, wordt het uit het register verwijderd. Het bestand zal niet worden verplaatst tenzij apart vermeld.)ShellIconOverlayIdentifiers: [  OverlayExcluded] -> {4433A54A-1AC8-432F-90FC-85F045CF383C} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\buShell.dll [2018-05-30] (Symantec Corporation)
            ShellIconOverlayIdentifiers: [  OverlayPending] -> {F17C0B1E-EF8E-4AD4-8E1B-7D7E8CB23225} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\buShell.dll [2018-05-30] (Symantec Corporation)
            ShellIconOverlayIdentifiers: [  OverlayProtected] -> {476D0EA3-80F9-48B5-B70B-05E677C9C148} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\buShell.dll [2018-05-30] (Symantec Corporation)
            ShellIconOverlayIdentifiers: [ AccExtIco1] -> {AB9CF9F8-8A96-4F9D-BF21-CE85714C3A47} => C:\Program Files (x86)\Adobe\Adobe Creative Cloud\CoreSyncExtension\CoreSync_x64.dll [2014-09-26] ()
            ShellIconOverlayIdentifiers: [ AccExtIco2] -> {853B7E05-C47D-4985-909A-D0DC5C6D7303} => C:\Program Files (x86)\Adobe\Adobe Creative Cloud\CoreSyncExtension\CoreSync_x64.dll [2014-09-26] ()
            ShellIconOverlayIdentifiers: [ AccExtIco3] -> {42D38F2E-98E9-4382-B546-E24E4D6D04BB} => C:\Program Files (x86)\Adobe\Adobe Creative Cloud\CoreSyncExtension\CoreSync_x64.dll [2014-09-26] ()
            ShellIconOverlayIdentifiers: [00asw] -> {472083B0-C522-11CF-8763-00608CC02F24} => C:\Program Files\AVAST Software\Avast\ashShA64.dll [2018-06-10] (AVAST Software)
            ShellIconOverlayIdentifiers-x32: [  OverlayExcluded] -> {4433A54A-1AC8-432F-90FC-85F045CF383C} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\buShell.dll [2018-05-30] (Symantec Corporation)
            ShellIconOverlayIdentifiers-x32: [  OverlayPending] -> {F17C0B1E-EF8E-4AD4-8E1B-7D7E8CB23225} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\buShell.dll [2018-05-30] (Symantec Corporation)
            ShellIconOverlayIdentifiers-x32: [  OverlayProtected] -> {476D0EA3-80F9-48B5-B70B-05E677C9C148} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\buShell.dll [2018-05-30] (Symantec Corporation)
            ContextMenuHandlers1: [AccExt] -> {2A118EB5-5797-4F5E-8B3D-F4ECBA3C98E4} => C:\Program Files (x86)\Adobe\Adobe Creative Cloud\CoreSyncExtension\CoreSync_x64.dll [2014-09-26] ()
            ContextMenuHandlers1: [BUContextMenu] -> {F7CAA2A1-67A2-44BB-B20F-202FD8EB1DAB} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\buShell.dll [2018-05-30] (Symantec Corporation)
            ContextMenuHandlers1: [ReflectShellExt] -> {DEBB9B79-B3DD-47F4-9E5C-EA6975BAB611} => C:\Program Files\Macrium\Reflect\RContextMenu.dll [2015-10-12] (Paramount Software UK Ltd)
            ContextMenuHandlers1: [SnagItMainShellExt] -> {CF74B903-3389-469c-B3B6-0204D204FCBD} => C:\Program Files\TechSmith\Snagit 2018\DLLx64\SnagitShellExt64.dll [2017-10-13] (TechSmith Corporation)
            ContextMenuHandlers1: [Symantec.Norton.Antivirus.IEContextMenu] -> {FAD61B3D-699D-49B2-BE16-7F82CB4C59CA} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\NavShExt.dll [2018-05-30] (Symantec Corporation)
            ContextMenuHandlers1: [WinRAR] -> {B41DB860-64E4-11D2-9906-E49FADC173CA} => C:\Program Files\WinRAR\rarext.dll [2012-06-09] (Alexander Roshal)
            ContextMenuHandlers1-x32: [WinRAR32] -> {B41DB860-8EE4-11D2-9906-E49FADC173CA} => C:\Program Files\WinRAR\rarext32.dll [2012-06-09] (Alexander Roshal)
            ContextMenuHandlers2: [ReflectShellExt] -> {DEBB9B79-B3DD-47F4-9E5C-EA6975BAB611} => C:\Program Files\Macrium\Reflect\RContextMenu.dll [2015-10-12] (Paramount Software UK Ltd)
            ContextMenuHandlers2: [Symantec.Norton.Antivirus.IEContextMenu] -> {FAD61B3D-699D-49B2-BE16-7F82CB4C59CA} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\NavShExt.dll [2018-05-30] (Symantec Corporation)
            ContextMenuHandlers3: [MBAMShlExt] -> {57CE581A-0CB6-4266-9CA0-19364C90A0B3} => C:\Program Files\Malwarebytes\Anti-Malware\mbshlext.dll [2017-08-21] (Malwarebytes)
            ContextMenuHandlers4: [SnagItMainShellExt] -> {CF74B903-3389-469c-B3B6-0204D204FCBD} => C:\Program Files\TechSmith\Snagit 2018\DLLx64\SnagitShellExt64.dll [2017-10-13] (TechSmith Corporation)
            ContextMenuHandlers4: [WinRAR] -> {B41DB860-64E4-11D2-9906-E49FADC173CA} => C:\Program Files\WinRAR\rarext.dll [2012-06-09] (Alexander Roshal)
            ContextMenuHandlers4-x32: [WinRAR32] -> {B41DB860-8EE4-11D2-9906-E49FADC173CA} => C:\Program Files\WinRAR\rarext32.dll [2012-06-09] (Alexander Roshal)
            ContextMenuHandlers5: [igfxcui] -> {3AB1675A-CCFF-11D2-8B20-00A0C93CB1F4} => C:\Windows\system32\igfxpph.dll [2012-01-10] (Intel Corporation)
            ContextMenuHandlers6: [AccExt] -> {2A118EB5-5797-4F5E-8B3D-F4ECBA3C98E4} => C:\Program Files (x86)\Adobe\Adobe Creative Cloud\CoreSyncExtension\CoreSync_x64.dll [2014-09-26] ()
            ContextMenuHandlers6: [BUContextMenu] -> {F7CAA2A1-67A2-44BB-B20F-202FD8EB1DAB} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\buShell.dll [2018-05-30] (Symantec Corporation)
            ContextMenuHandlers6: [MBAMShlExt] -> {57CE581A-0CB6-4266-9CA0-19364C90A0B3} => C:\Program Files\Malwarebytes\Anti-Malware\mbshlext.dll [2017-08-21] (Malwarebytes)
            ContextMenuHandlers6: [RUShellExt] -> {2C5515DC-2A7E-4BFD-B813-CACC2B685EB7} => C:\Program Files\VS Revo Group\Revo Uninstaller Pro\RUExt.dll [2016-12-15] (VS Revo Group)
            ContextMenuHandlers6: [Symantec.Norton.Antivirus.IEContextMenu] -> {FAD61B3D-699D-49B2-BE16-7F82CB4C59CA} => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\NavShExt.dll [2018-05-30] (Symantec Corporation)
            ContextMenuHandlers6: [WinRAR] -> {B41DB860-64E4-11D2-9906-E49FADC173CA} => C:\Program Files\WinRAR\rarext.dll [2012-06-09] (Alexander Roshal)
            ContextMenuHandlers6-x32: [WinRAR32] -> {B41DB860-8EE4-11D2-9906-E49FADC173CA} => C:\Program Files\WinRAR\rarext32.dll [2012-06-09] (Alexander Roshal)==================== Geplande Taken (gefilterd) =============(Als een item is opgenomen in de fixlist, wordt het uit het register verwijderd. Het bestand zal niet worden verplaatst tenzij apart vermeld.)Task: {014A1268-3A4C-4790-9DBD-0165CDADD641} - System32\Tasks\{47C3FA91-F676-4410-9BF1-09E0C997123E} => C:\Users\Gebruiker\Desktop\adwcleaner.exe
            Task: {0284354D-C1DB-4849-816E-11D2D9F554E9} - System32\Tasks\{8180F6A2-22ED-40FA-B4CA-5F69C526A5ED} => C:\Windows\system32\pcalua.exe -a "C:\Program Files (x86)\AVS4YOU\Uninstall.exe"
            Task: {10A81937-FA5D-4FEA-B2CD-4DDE185CB86E} - System32\Tasks\Norton Security with Backup\Norton Security Online Error Analyzer => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\SymErr.exe [2018-05-30] (Symantec Corporation)
            Task: {1BFD3E32-441C-44BC-A209-C0441834C8CF} - System32\Tasks\Adobe Acrobat Update Task => C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe [2018-02-09] (Adobe Systems Incorporated)
            Task: {1DB5E6F0-90DB-4B4D-8C81-D4C2B6D217C1} - System32\Tasks\{88C34C03-4ABA-48E8-8234-5E4A03D8B227} => C:\Windows\system32\pcalua.exe -a "D:\Downloads van Internet\Download-programma's\MP3Gain 1_2_5\mp3gain-win-1_2_5.exe" -d "D:\Downloads van Internet\Download-programma's\MP3Gain 1_2_5"
            Task: {23866746-7C70-41B0-8720-2CE75B7F5636} - System32\Tasks\GoogleUpdateTaskMachineCore => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2017-08-25] (Google Inc.)
            Task: {257F243B-764F-4E13-9395-25BFAC0DA17D} - System32\Tasks\{F98693DF-1467-468D-B16A-80289B75734E} => C:\Windows\system32\pcalua.exe -a E:\DRIVER\Setup.exe -d E:\DRIVER
            Task: {2D0D3DC9-228A-4402-B062-FBCB270F4C4D} - System32\Tasks\CCleaner Update => C:\Program Files\CCleaner\CCUpdate.exe [2018-05-24] (Piriform Ltd)
            Task: {2DCBC935-468E-4936-8763-53CCFC192FBA} - System32\Tasks\{55F7A489-17F0-4B92-A216-BA13F6DC41F5} => C:\Windows\system32\pcalua.exe -a C:\Users\Gebruiker\Downloads\aomwin200ea24.exe -d C:\Users\Gebruiker\Desktop
            Task: {3C7CBFF3-11F9-4FC1-AD40-C0A6D7347509} - System32\Tasks\{259500CC-994D-4012-BE6F-8E8873AF04D2} => C:\Windows\system32\pcalua.exe -a "D:\Downloads van Internet\Programma's\iTunes\iTunesSetupAdmin.exe" -d "D:\Downloads van Internet\Programma's\iTunes"
            Task: {3E432DC0-0D5A-4CAF-B014-2A04133311AC} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Solutions Framework Updater => C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\Modules\HPSSFUpdater.exe [2017-09-20] (HP Inc.)
            Task: {4AA191D6-B9D6-4E62-9D85-1D687B8B4605} - System32\Tasks\Apple\AppleSoftwareUpdate => C:\Program Files (x86)\Apple Software Update\SoftwareUpdate.exe [2017-07-24] (Apple Inc.)
            Task: {4FF72F0E-7576-4CDE-B993-795F59DD2818} - System32\Tasks\Hewlett-Packard\HP Support Assistant\WarrantyChecker_DeviceScan => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPWarrantyCheck\HPWarrantyChecker.exe [2018-05-02] (HP Inc.)
            Task: {536EE588-23AD-42BF-A78A-AE7F18E0CBA2} - System32\Tasks\{E81C7686-7E55-4EE2-923A-FEFFC22F76BE} => C:\Windows\system32\pcalua.exe -a "D:\Downloads van Internet\Drivers\HP DeskJet 970 Cxi\HP_900_Inkjet_enu.exe" -d "D:\Downloads van Internet\Drivers\HP DeskJet 970 Cxi"
            Task: {594E3F60-7AA7-49A1-BCF8-4A50480F557F} - System32\Tasks\Norton WSC Integration => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\WSCStub.exe [2018-05-30] (Symantec Corporation)
            Task: {5F068EFB-889E-462C-B567-4A9557F2195E} - System32\Tasks\{D9043C71-32B0-4940-ADF7-DA806C40FFE9} => C:\Windows\system32\pcalua.exe -a "D:\Downloads van Internet\Download-programma's\Paragon Free\br14-free_eng.exe" -d "D:\Downloads van Internet\Download-programma's\Paragon Free"
            Task: {647CC88E-586F-43A2-9F8F-BC560AACDC6B} - System32\Tasks\{88CDEA7C-EAC5-458F-B23D-4197AF33B62D} => C:\Windows\system32\pcalua.exe -a E:\setup.exe -d E:\
            Task: {74F418F6-1F6E-488F-A445-18E58F2F956F} - System32\Tasks\hpUrlLauncher.exe_{5E0FAD80-5C19-4AFA-AA56-6A963A3DC6B4} => C:\Program Files\HP\HP Officejet 5740 series\Bin\utils\hpUrlLauncher.exe [2017-05-24] (HP Inc.)
            Task: {7FB967FD-9D15-43B4-9B59-28B1596C4930} - System32\Tasks\Norton Security with Backup\Norton Security Online Error Processor => C:\Program Files (x86)\Norton Security with Backup\Engine\22.14.2.13\SymErr.exe [2018-05-30] (Symantec Corporation)
            Task: {7FCD3366-7F01-4CC8-B199-531A59C17982} - System32\Tasks\{66CE0A10-D4E0-4CF0-8F52-4B4969DB7201} => C:\Windows\system32\pcalua.exe -a "C:\Program Files (x86)\NCH Swift Sound\Switch\uninst.exe" -d "C:\Program Files (x86)\NCH Swift Sound\Switch"
            Task: {93937031-01B7-4C9C-87C1-C50258A86217} - System32\Tasks\HPCustParticipation HP Officejet 5740 series => C:\Program Files\HP\HP Officejet 5740 series\Bin\HPCustPartic.exe [2017-05-23] (HP Inc.)
            Task: {9791E5A8-963A-4715-AED9-EB8D921E9EFD} - System32\Tasks\{2EEB9309-43B0-492C-935E-F58972840EFD} => C:\Users\Gebruiker\Desktop\adwcleaner.exe
            Task: {9FF31DC3-C18C-4B5A-A181-1ED548A9D578} - System32\Tasks\HPCeeScheduleForGebruiker => C:\Program Files (x86)\Hewlett-Packard\HP Ceement\HPCEE.exe [2016-05-12] (HP Development Company, L.P.)
            Task: {A9A83DE7-2664-4790-B423-CBB5C7342895} - System32\Tasks\CCleanerSkipUAC => C:\Program Files\CCleaner\CCleaner.exe [2018-05-24] (Piriform Ltd)
            Task: {AD1CC8C8-5671-4F3B-9761-DBE4C1BF07E1} - System32\Tasks\{19D90AD0-404E-48F6-BA48-645A461CEDF4} => C:\Windows\system32\pcalua.exe -a "C:\Program Files (x86)\Common Files\Nero\Nero ProductInstaller 4\SetupX.exe" -c REMOVESERIALNUMBER="2M0M-K08C-2LTT-MKWH-MM4K-6767-6TT9-C0XM-U6EE-P288-08EX-HU66-4602-2WM2-0LCE-M69L-L0CA-225W-213L-392Z-4UA0-1U89-3T7H-884M-774W-3C00"
            Task: {B5973CDC-22ED-469E-8ECD-3082B1E83E14} - System32\Tasks\Hewlett-Packard\HP Support Assistant\PC Health Analysis => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\HPSF.exe [2018-05-04] (HP Inc.)
            Task: {B770ED30-F298-4AF1-B4E1-3FE16FD524CB} - System32\Tasks\VSO Software Updater => C:\Windows\system32\wscript.exe //nologo //E:jscript //B "C:\Program Files (x86)\VSO Software Updater\updater.ini" <==== AANDACHT
            Task: {BF6BC82F-F158-49C9-B578-81043A6B124A} - System32\Tasks\Remediation\AntimalwareMigrationTask => C:\Program Files\Common Files\AV\Norton Security Online\Upgrade.exe [2018-05-30] (Symantec Corporation)
            Task: {C592F34D-E9AB-4E42-B43C-A3D724554490} - System32\Tasks\Hewlett-Packard\HP Support Assistant\Product Configurator => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\ProductConfig.exe [2018-05-11] (HP Inc.)
            Task: {C80EBC05-8E12-4122-A661-9511ED2282C0} - \Avast Emergency Update -> Geen bestand <==== AANDACHT
            Task: {C9F4663E-BA89-476A-A5DF-82DF5CE4930B} - System32\Tasks\GoogleUpdateTaskMachineUA => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2017-08-25] (Google Inc.)
            Task: {D12AD514-4F84-45B1-AA98-2844A99EA1E0} - System32\Tasks\Hewlett-Packard\HP Active Health\HP Active Health Scan (HPSA) => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPActiveHealth\ActiveHealth.exe [2017-11-17] ()
            Task: {D51B4B72-B2B8-4124-A55F-F56059298A19} - System32\Tasks\Adobe Flash Player Updater => C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe [2018-06-07] (Adobe Systems Incorporated)
            Task: {DA0B0664-66CC-4D0C-B405-B3DE67CE844D} - System32\Tasks\{6BC80AF3-56D7-41C8-9F62-D98B5448A946} => C:\Windows\system32\pcalua.exe -a E:\INSTALL\SETUP.EXE -d E:\INSTALL
            Task: {DB8D02F6-E124-4EA1-9DDA-5CCCF408BCB4} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Assistant printer driver installation => C:\Windows\TEMP\OJ5740_Full_WebPack_40.11.1135.exe <==== AANDACHT
            Task: {DD766CB7-5675-4C7C-9808-6676A217BF77} - System32\Tasks\{D6F4A0C1-FD1F-4610-8B58-FE7F3662E114} => C:\Windows\system32\pcalua.exe -a "C:\Program Files (x86)\QuickTime\QTSystem\QuickTime.cpl" -c QuickTime
            Task: {E32882F4-B347-47EA-BED0-CC99AB4E20E4} - System32\Tasks\Games\UpdateCheck_S-1-5-21-3233923740-3587472772-2755484448-1000
            Task: {E4BC3588-5ADB-49D2-9F80-E0E7238FB521} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Solutions Framework Report => C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\Modules\HPSFReport.exe [2017-06-22] (HP Inc.)
            Task: {E5D8F59D-0D4B-4613-96F8-C849D664E6DE} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Solutions Framework Updater - Resources => C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\Modules\HPSSFUpdater.exe [2017-09-20] (HP Inc.)
            Task: {EF793534-8E44-446C-9E04-BEA25AA01B1F} - System32\Tasks\{979D8242-8CFB-4E88-B7FF-E0C5B4D2D1D2} => C:\Windows\system32\pcalua.exe -a "C:\Users\Gebruiker\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\WO1EMYB8\JavaSetup8u121.exe" -d C:\Users\Gebruiker\Desktop
            Task: {F2B19AFA-2BB0-4745-8D19-84084493EFD2} - System32\Tasks\Hewlett-Packard\HP Support Assistant\WarrantyChecker_TH5A74Y131 => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPWarrantyCheck\HPWarrantyChecker.exe [2018-05-02] (HP Inc.)
            Task: {F5F3CA84-C17C-47BD-898E-A2D8E7B0CAE6} - System32\Tasks\AdobeAAMUpdater-1.0-Gebruiker-PC-Gebruiker => C:\Program Files (x86)\Common Files\Adobe\OOBE\PDApp\UWA\UpdaterStartupUtility.exe [2014-10-14] (Adobe Systems Incorporated)
            Task: {F7B242F6-C1CF-41F0-95E6-793D923F0530} - System32\Tasks\{B6FA4B46-38CE-46F6-8512-E2903503F129} => C:\Windows\system32\pcalua.exe -a "C:\Users\Gebruiker\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\DWBHNCF4\VobSub_2.23[1].exe" -d C:\Users\Gebruiker\Desktop
            Task: {FD192191-0AA7-4370-960E-3BB27BB0CD63} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Assistant Quick Start => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\HPSF.exe [2018-05-04] (HP Inc.)(Als een item is opgenomen in de fixlist, wordt de taak (job) bestand verplaatst. Het bestand dat wordt uitgevoerd door de taak zal niet worden verplaatst.)Task: C:\Windows\Tasks\HPCeeScheduleForGebruiker.job => C:\Program Files (x86)\Hewlett-Packard\HP Ceement\HPCEE.exe
            Task: C:\Windows\Tasks\VSO Software Updater.job => Wscript.exe S/nologo /E:jscript /B C:\Program Files (x86)\VSO Software Updater\updater.ini <==== AANDACHT==================== Snelkoppelingen & WMI ========================(De items kunnen worden opgenomen in de fixlist.txt om hersteld of verwijderd te worden.)
            Shortcut: C:\Users\Gebruiker\Favorites\Muziek\NCH Software Download Site.lnk -> hxxp://www.nch.com.au/index.htm
            Shortcut: C:\Users\Gebruiker\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\FrostWire 6\FrostWire 6.6.7-SafeMode.lnk -> C:\Program Files (x86)\FrostWire 6\frostwire.bat ()==================== Geladen Modules (gefilterd) ==============2014-09-26 15:41 - 2014-09-26 15:41 - 001021088 _____ () C:\Program Files (x86)\Adobe\Adobe Creative Cloud\CoreSyncExtension\CoreSync_x64.dll
            2013-09-05 01:17 - 2013-09-05 01:17 - 004300456 _____ () C:\Program Files\Common Files\Microsoft Shared\OFFICE14\Cultures\OFFICE.ODF
            2017-12-08 02:48 - 2017-12-08 02:48 - 001356088 _____ () C:\Program Files\Common Files\Apple\Apple Application Support\libxml2.dll
            2017-12-08 02:48 - 2017-12-08 02:48 - 000088888 _____ () C:\Program Files\Common Files\Apple\Apple Application Support\zlib1.dll
            2015-05-20 10:16 - 2008-01-22 19:35 - 000103808 _____ () C:\Program Files (x86)\Canon\IJPLM\IJPLMSVC.EXE
            2010-10-30 12:13 - 2009-04-15 16:56 - 000271760 ____N () C:\Program Files (x86)\CyberLink\Shared files\RichVideo.exe
            2012-01-10 21:12 - 2012-01-10 21:12 - 000094208 _____ () C:\Windows\System32\IccLibDll_x64.dll
            2018-06-10 10:27 - 2018-06-10 10:27 - 000482520 _____ () C:\Program Files\AVAST Software\Avast\streamback.dll
            2018-06-10 10:27 - 2018-06-10 10:27 - 000889048 _____ () C:\Program Files\AVAST Software\Avast\ffl2.dll
            2018-06-10 10:30 - 2018-06-10 10:30 - 000924888 _____ () C:\Program Files\AVAST Software\Avast\anen.dll
            2018-06-10 10:27 - 2018-06-10 10:27 - 000150744 _____ () C:\Program Files\AVAST Software\Avast\hns_tools.dll
            2018-06-10 10:27 - 2018-06-10 10:27 - 000982744 _____ () C:\Program Files\AVAST Software\Avast\shepherdsync.dll
            2018-06-10 10:27 - 2018-06-10 10:27 - 000519896 _____ () C:\Program Files\AVAST Software\Avast\gui_cache.dll
            2018-06-12 14:44 - 2018-06-12 14:44 - 005839504 _____ () C:\Program Files\AVAST Software\Avast\defs\18061202\algo.dll
            2018-06-10 10:30 - 2018-06-10 10:30 - 067126928 _____ () C:\Program Files\AVAST Software\Avast\libcef.dll
            2018-06-10 10:27 - 2018-06-10 10:27 - 000293592 _____ () C:\Program Files\AVAST Software\Avast\gaming_mode_ui.dll
            2014-03-31 22:35 - 2014-03-31 22:35 - 000278208 _____ () C:\Program Files (x86)\Windows Live\Writer\nl\WindowsLive.Writer.Localization.resources.dll==================== Alternate Data Streams (gefilterd) =========(Als een item is opgenomen in de fixlist, wordt alleen de ADS verwijderd.)
            ==================== Veilige Modus (gefilterd) ===================(Als een item is opgenomen in de fixlist, wordt het uit het register verwijderd. De waarde van "AlternateShell" wordt hersteld.)HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\MBAMService => ""="Service"
            HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\PEVSystemStart => ""="Service"
            HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\procexp90.Sys => ""="Driver"
            HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Network\MBAMService => ""="Service"
            HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Network\PEVSystemStart => ""="Service"
            HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Network\procexp90.Sys => ""="Driver"==================== Bestandskoppeling (gefilterd) ===============(Als een item is opgenomen in de fixlist, zal het registeritem worden teruggezet naar de standaardwaarden of verwijderd.)
            ==================== Internet Explorer vertrouwde/beperkte toegang ===============(Als een item is opgenomen in de fixlist, wordt het uit het register verwijderd.)IE trusted site: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\...\fgov.be -> hxxps://mypension.onprvp.fgov.be
            IE trusted site: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\...\google.be -> hxxps://www.google.be
            IE trusted site: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\...\kbc.be -> hxxps://www.kbc.be
            IE trusted site: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\...\localhost -> localhost==================== Hosts inhoud: ==========================(Indien nodig kan Hosts:-opdracht worden opgenomen in de fixlist om Hosts te resetten.)2009-07-14 04:34 - 2016-12-25 10:55 - 000000158 ____N C:\Windows\system32\Drivers\etc\hosts127.0.0.1       localhost
            127.0.0.1 lm.licenses.adobe.com
            0.0.0.0 apps.corel.com
            0.0.0.0 mc.corel.com
            0.0.0.0 origin-mc.corel.com
            0.0.0.0 iws.corel.com==================== Andere gebieden ============================(Momenteel is er geen automatische fix voor dit onderdeel.)HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\Control Panel\Desktop\\Wallpaper -> C:\Users\Gebruiker\AppData\Roaming\Microsoft\Windows\Themes\TranscodedWallpaper.jpg
            DNS Servers: 192.168.1.1
            HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System => (ConsentPromptBehaviorAdmin: 5) (ConsentPromptBehaviorUser: 3) (EnableLUA: 1)
            Windows Firewall is ingeschakeld.==================== MSCONFIG/TASK MANAGER Uitgeschakelde items ==MSCONFIG\startupfolder: C:^ProgramData^Microsoft^Windows^Start Menu^Programs^Startup^HP Digital Imaging Monitor.lnk => C:\Windows\pss\HP Digital Imaging Monitor.lnk.CommonStartup
            MSCONFIG\startupfolder: C:^Users^Gebruiker^AppData^Roaming^Microsoft^Windows^Start Menu^Programs^Startup^OneNote 2010 Schermopname en Snel starten.lnk => C:\Windows\pss\OneNote 2010 Schermopname en Snel starten.lnk.Startup
            MSCONFIG\startupreg: Acronis Scheduler2 Service => "C:\Program Files (x86)\Common Files\Acronis\Schedule2\schedhlp.exe"
            MSCONFIG\startupreg: AcronisTibMounterMonitor => C:\Program Files (x86)\Common Files\Acronis\TibMounter\TibMounterMonitor.exe
            MSCONFIG\startupreg: Adobe Creative Cloud => "C:\Program Files (x86)\Adobe\Adobe Creative Cloud\ACC\Creative Cloud.exe" --showwindow=false --onOSstartup=true
            MSCONFIG\startupreg: AdobeAAMUpdater-1.0 => "C:\Program Files (x86)\Common Files\Adobe\OOBE\PDApp\UWA\UpdaterStartupUtility.exe"
            MSCONFIG\startupreg: APSDaemon => "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe"
            MSCONFIG\startupreg: ArcSoft Connection Service => C:\Program Files (x86)\Common Files\ArcSoft\Connection Service\Bin\ACDaemon.exe
            MSCONFIG\startupreg: BCSSync => "C:\Program Files (x86)\Microsoft Office\Office14\BCSSync.exe" /DelayServices
            MSCONFIG\startupreg: CanonMyPrinter => C:\Program Files\Canon\MyPrinter\BJMyPrt.exe /logon
            MSCONFIG\startupreg: CanonSolutionMenu => C:\Program Files (x86)\Canon\SolutionMenu\CNSLMAIN.exe /logon
            MSCONFIG\startupreg: CCleaner Monitoring => "C:\Program Files\CCleaner\CCleaner64.exe" /MONITOR
            MSCONFIG\startupreg: CLMLServer => "C:\Program Files (x86)\CyberLink\Power2Go\CLMLSvc.exe"
            MSCONFIG\startupreg: DivXUpdate => "C:\Program Files (x86)\DivX\DivX Update\DivXUpdate.exe" /CHECKNOW
            MSCONFIG\startupreg: HP Software Update => C:\Program Files (x86)\HP\HP Software Update\HPWuSchd2.exe
            MSCONFIG\startupreg: hpqSRMon => C:\Program Files (x86)\HP\Digital Imaging\bin\hpqSRMon.exe
            MSCONFIG\startupreg: IMSS => "C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\IMSS\PIconStartup.exe"
            MSCONFIG\startupreg: iTunesHelper => "C:\Program Files\iTunes\iTunesHelper.exe"
            MSCONFIG\startupreg: Lync => "C:\Program Files\Microsoft Office\Office15\lync.exe" /fromrunkey
            MSCONFIG\startupreg: Malwarebytes TrayApp => C:\PROGRAM FILES\MALWAREBYTES\ANTI-MALWARE\mbamtray.exe
            MSCONFIG\startupreg: msnmsgr => "C:\Program Files (x86)\Windows Live\Messenger\msnmsgr.exe" /background
            MSCONFIG\startupreg: OfficeSyncProcess => "C:\Program Files (x86)\Microsoft Office\Office14\MSOSYNC.EXE"
            MSCONFIG\startupreg: PDVD8LanguageShortcut => "C:\Program Files (x86)\CyberLink\PowerDVD8\Language\Language.exe"
            MSCONFIG\startupreg: QuickTime Task => "C:\Program Files (x86)\QuickTime\QTTask.exe" -atboottime
            MSCONFIG\startupreg: RemoteControl8 => "C:\Program Files (x86)\CyberLink\PowerDVD8\PDVD8Serv.exe"
            MSCONFIG\startupreg: SunJavaUpdateSched => "C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe"
            MSCONFIG\startupreg: TechSmithSnagit => "C:\Program Files\TechSmith\Snagit 2018\Snagit32.exe" /i
            MSCONFIG\startupreg: TrueImageMonitor.exe => "C:\Program Files (x86)\Acronis\TrueImageHome\TrueImageMonitor.exe"
            MSCONFIG\startupreg: UCam_Menu => "C:\Program Files (x86)\CyberLink\YouCam\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\YouCam" UpdateWithCreateOnce "Software\CyberLink\YouCam\2.0"
            MSCONFIG\startupreg: UpdateLBPShortCut => "C:\Program Files (x86)\CyberLink\LabelPrint\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\LabelPrint" UpdateWithCreateOnce "Software\CyberLink\LabelPrint\2.5"
            MSCONFIG\startupreg: UpdateP2GoShortCut => "C:\Program Files (x86)\CyberLink\Power2Go\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\Power2Go" UpdateWithCreateOnce "SOFTWARE\CyberLink\Power2Go\6.0"
            MSCONFIG\startupreg: UpdatePPShortCut => "C:\Program Files (x86)\CyberLink\PowerProducer\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\PowerProducer" UpdateWithCreateOnce "Software\CyberLink\PowerProducer\5.0"
            MSCONFIG\startupreg: UpdatePSTShortCut => "C:\Program Files (x86)\CyberLink\DVD Suite\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\DVD Suite" UpdateWithCreateOnce "Software\CyberLink\PowerStarter"==================== Firewall regels (gefilterd) ===============(Als een item is opgenomen in de fixlist, wordt het uit het register verwijderd. Het bestand zal niet worden verplaatst tenzij apart vermeld.)FirewallRules: [{2957149F-503E-477A-B19E-B6DB4DA8E8D5}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqtra08.exe
            FirewallRules: [{DDF15079-12C2-4AB4-B1EE-CCE695A9C1B7}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqste08.exe
            FirewallRules: [{A5665EB7-25A7-4406-AC31-C3AF3BBC6516}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpofxm08.exe
            FirewallRules: [{E23F29A7-EBF5-40A0-8447-FF6F2E687200}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hposfx08.exe
            FirewallRules: [{B5B86196-3A84-4F60-96AE-02C5ABD714B8}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hposid01.exe
            FirewallRules: [{95310302-C81A-435F-81B6-C608C08482BC}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqkygrp.exe
            FirewallRules: [{74543E1E-AF1E-4167-8DFB-B286D451A9E4}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqcopy2.exe
            FirewallRules: [{58E1253E-ADF9-4C38-99D8-33B1CF76A55A}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpfccopy.exe
            FirewallRules: [{0A382F08-BAF9-485F-9F4A-5C90D098BE6A}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpzwiz01.exe
            FirewallRules: [{C5D8874C-CE02-4EB9-A6CF-9E9E6C68F533}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpoews01.exe
            FirewallRules: [{7CBC6C31-B3AE-40A1-B195-2904B8055DA6}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqnrs08.exe
            FirewallRules: [{7E797775-471C-4682-BB93-E34D47CE16FD}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpiscnapp.exe
            FirewallRules: [{BDA34243-87F1-4F29-B85D-F261ACE6C3B4}] => (Allow) C:\Program Files (x86)\common files\hp\digital imaging\bin\hpqphotocrm.exe
            FirewallRules: [{972E9414-F435-4A67-881D-6B4B99887D19}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqsudi.exe
            FirewallRules: [{E480A595-F45E-4514-8840-476280F0EF71}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqpsapp.exe
            FirewallRules: [{EF82F603-7630-4D0E-A8A4-9858D7B5A880}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpofxs08.exe
            FirewallRules: [{B1291874-5C06-4DFD-9865-D4EC985BB0DA}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqfxt08.exe
            FirewallRules: [{A210CBB4-8A18-4C9C-8683-DAA5755AB529}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqpse.exe
            FirewallRules: [{58F3A9E4-E23F-478A-9B3F-FD4E8716CDAD}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqgplgtupl.exe
            FirewallRules: [{BE60F804-848E-44AA-BDC7-3558F03A5E59}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqgpc01.exe
            FirewallRules: [{C9D854BF-4C2B-42D5-ABDB-A2DC09F25AF6}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqusgm.exe
            FirewallRules: [{E0A8C2E6-EC39-4B94-B4F8-9C10DEC9932F}] => (Allow) C:\Program Files (x86)\HP\Digital Imaging\bin\hpqusgh.exe
            FirewallRules: [{1E44B39C-7F8F-4CC3-A00D-5C57E75BB105}] => (Allow) C:\Program Files (x86)\HP\hp software update\hpwucli.exe
            FirewallRules: [{FFBDDDBE-42D4-46D1-A1CA-DD86D10F561E}] => (Allow) C:\Program Files (x86)\HP\digital imaging\smart web printing\smartwebprintexe.exe
            FirewallRules: [{C814956D-87B7-4129-AFAE-692586DC36EC}] => (Allow) C:\Program Files (x86)\CyberLink\PowerDVD8\PowerDVD8.EXE
            FirewallRules: [{DD8351CF-820F-44EE-AADC-16BB45568D37}] => (Allow) C:\Program Files (x86)\Windows Live\Contacts\wlcomm.exe
            FirewallRules: [{95F026F5-0A80-4B88-B798-54A4821DB453}] => (Allow) LPort=2869
            FirewallRules: [{83747881-A824-4F49-9B61-A96B781F3C7E}] => (Allow) LPort=1900
            FirewallRules: [{603DDFFA-6C14-4717-96AD-E0C313D8347D}] => (Allow) C:\Program Files (x86)\Windows Live\Messenger\msnmsgr.exe
            FirewallRules: [{3A09CA39-255B-4698-8E93-7D7DB2AAAC8A}] => (Allow) C:\Program Files (x86)\FormatFactory\FormatFactory.exe
            FirewallRules: [{2E4D7D18-2366-4399-B84A-8CD7AE0DB414}] => (Allow) C:\Program Files\Bonjour\mDNSResponder.exe
            FirewallRules: [{01570F76-090F-4E07-B799-B57DC94C2FF5}] => (Allow) C:\Program Files\Bonjour\mDNSResponder.exe
            FirewallRules: [{28A1F96A-9FC3-426C-A52A-FEF561067521}] => (Allow) C:\Program Files (x86)\Bonjour\mDNSResponder.exe
            FirewallRules: [{D6C837CC-76A1-4557-AD44-960D75E00A43}] => (Allow) C:\Program Files (x86)\Bonjour\mDNSResponder.exe
            FirewallRules: [{0A3A643B-DDA4-4B35-AFFF-3BFA6811B3CE}] => (Allow) C:\Program Files (x86)\FormatFactory\FFModules\Encoder\Doc\EBookCodec.exe
            FirewallRules: [{51F6E12C-5179-4302-A938-F5913E274E14}] => (Allow) C:\Program Files (x86)\FormatFactory\FormatFactory.exe
            FirewallRules: [{605A04A8-4348-42AF-9B1B-AEE0C5ED8C89}] => (Allow) C:\Users\Gebruiker\AppData\Roaming\uTorrent\uTorrent.exe
            FirewallRules: [{6AFF81F6-CB2E-4AED-8B05-7B584A195D72}] => (Allow) C:\Users\Gebruiker\AppData\Roaming\uTorrent\uTorrent.exe
            FirewallRules: [{61C069E9-7BD9-4A3B-87B0-5EAE730FEEA5}] => (Allow) C:\Users\Gebruiker\AppData\Roaming\uTorrent\uTorrent.exe
            FirewallRules: [{0F4D3C10-1905-4B29-9A41-8C50BE4FF595}] => (Allow) C:\Users\Gebruiker\AppData\Roaming\uTorrent\uTorrent.exe
            FirewallRules: [{53AD1D98-A713-4ABB-A765-7ECF688AA398}] => (Allow) C:\Users\Gebruiker\AppData\Roaming\uTorrent\uTorrent.exe
            FirewallRules: [{8B274332-9B78-4059-950F-8D3E1BE1CF86}] => (Allow) C:\Users\Gebruiker\AppData\Roaming\uTorrent\uTorrent.exe
            FirewallRules: [{FBC6A035-7685-4126-8B05-D45A03EED80F}] => (Allow) C:\Program Files (x86)\TeamViewer\TeamViewer.exe
            FirewallRules: [{E06DB689-EB88-4957-AA05-9E5327BCD8D0}] => (Allow) C:\Program Files (x86)\TeamViewer\TeamViewer.exe
            FirewallRules: [{BB21D1AE-D8B5-4E28-8591-5998E526858B}] => (Allow) C:\Program Files (x86)\TeamViewer\TeamViewer_Service.exe
            FirewallRules: [{FEC66051-19FA-4807-9B37-68386FD22481}] => (Allow) C:\Program Files (x86)\TeamViewer\TeamViewer_Service.exe
            FirewallRules: [{F53B94C5-E6CA-4C23-B0F7-35F71B9A21AC}] => (Allow) C:\Program Files (x86)\FormatFactory\FFModules\Encoder\Doc\EBookCodec.exe
            FirewallRules: [{6B2AC0BB-ADCE-4BDA-B021-E98450C75B18}] => (Allow) C:\Program Files (x86)\FormatFactory\FormatFactory.exe
            FirewallRules: [{DAD47BF1-4BC0-40B7-A013-E92685FCF8EA}] => (Allow) C:\Program Files\HP\HP Officejet 5740 series\bin\FaxApplications.exe
            FirewallRules: [{9195381F-5C92-44DF-A78A-1F27C00B7C8B}] => (Allow) C:\Program Files\HP\HP Officejet 5740 series\bin\DigitalWizards.exe
            FirewallRules: [{3A11064B-E108-435B-BF6C-63B46881ACBC}] => (Allow) C:\Program Files\HP\HP Officejet 5740 series\bin\SendAFax.exe
            FirewallRules: [{31ABF216-D550-4533-ACA5-1EB7D47A4045}] => (Allow) C:\Program Files\HP\HP Officejet 5740 series\bin\FaxPrinterUtility.exe
            FirewallRules: [{39C1C97C-BDFF-4E08-9B60-E9B21B87CD9D}] => (Allow) C:\Program Files\HP\HP Officejet 5740 series\Bin\DeviceSetup.exe
            FirewallRules: [{A634BB22-EF76-4FAC-A1C1-CABEAAC4E926}] => (Allow) LPort=5357
            FirewallRules: [{44ED72F2-F9BC-4E04-80E1-3E2EC5D8125C}] => (Allow) C:\Program Files\HP\HP Officejet 5740 series\Bin\HPNetworkCommunicatorCom.exe
            FirewallRules: [{A1F34C07-C2F8-4D59-ACC2-AFB8A24C9375}] => (Allow) C:\Program Files (x86)\FrostWire 6\FrostWire.exe
            FirewallRules: [{27816B3B-6FB3-4D3F-B371-05F23C5290E2}] => (Allow) C:\Program Files (x86)\FrostWire 6\FrostWire.exe
            FirewallRules: [{738CA252-2CA8-41E6-80E0-73C1144DD081}] => (Allow) C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe
            FirewallRules: [{5567F6E3-16E0-49DF-8929-CD7ECCB5F841}] => (Allow) C:\Program Files\iTunes\iTunes.exe
            FirewallRules: [{9A526735-DA6A-4DDA-8C28-A4089165297C}] => (Allow) C:\Program Files\CCleaner\CCUpdate.exe
            FirewallRules: [{340EE719-4FBD-4620-AC54-80F054CA3162}] => (Allow) C:\Program Files\CCleaner\CCUpdate.exe
            FirewallRules: [{BAD14B1B-3ED2-4EBD-9E95-A54A421AC958}] => (Allow) LPort=8298==================== Herstelpunten =========================02-06-2018 15:49:22 Revo Uninstaller Pro's restore point - CrystalDiskInfo 6.2.1
            02-06-2018 15:52:18 Revo Uninstaller Pro's restore point - Paragon Backup and Recovery™ 14 Free
            02-06-2018 15:54:29 Revo Uninstaller Pro's restore point - Speccy
            03-06-2018 14:00:19 Windows Back-up
            05-06-2018 09:45:43 Installed Snagit 10.0.1
            05-06-2018 09:49:02 Installed Snagit 10.0.1
            05-06-2018 10:17:26 Removed Snagit 10.0.1
            05-06-2018 10:28:22 Snagit 2018
            05-06-2018 10:41:00 Snagit 2018
            05-06-2018 10:50:47 Snagit 2018
            05-06-2018 10:51:47 Revo Uninstaller Pro's restore point - Snagit 2018
            05-06-2018 10:58:20 Snagit 2018
            10-06-2018 10:33:20 Revo Uninstaller Pro's restore point - Avast Free Antivirus
            10-06-2018 10:44:06 Revo Uninstaller Pro's restore point - WebDiscover Browser 4.26.2
            10-06-2018 10:46:29 Revo Uninstaller Pro's restore point - WinZip Registry Optimizer
            10-06-2018 12:53:57 JRT Pre-Junkware Removal
            10-06-2018 14:00:28 Windows Back-up
            10-06-2018 14:17:48 Snagit 2018
            11-06-2018 15:05:41 Revo Uninstaller Pro's restore point - Norton Ghost==================== Defecte Apparaatbeheer Apparaten =============
            ==================== Eventlog fouten: =========================Applicatiefouten:
            ==================
            Error: (06/11/2018 03:05:41 PM) (Source: VSS) (EventID: 8194) (User: )
            Description: Fout in de Volume Shadow Copy-service: onverwachte fout bij het uitvoeren van een query voor de IVssWriterCallback-interface. hr = 0x80070005, Toegang geweigerd.
            .
            Dit wordt vaak veroorzaakt door onjuiste beveiligingsinstellingen in het writer- of requestorproces.
            Bewerking:
               Schrijvergegevens verzamelenContext:
               Klasse-id van schrijver: {e8132975-6f93-4464-a53e-1050253ae220}
               Naam van schrijver: System Writer
               Instantie-id van schrijver: {5406eb3b-6e21-4d50-8736-dd2904f65f57}Error: (06/10/2018 02:51:47 PM) (Source: VSS) (EventID: 12292) (User: )
            Description: Fout in de Volume Shadow Copy-service: fout bij het maken van de COM-klasse van de schaduwkopieprovider met CLSID {790f2886-9889-4c99-8ef5-531add05d044} [0x80110802].
            Bewerking:
               Aanroepbare interface voor deze provider verkrijgen
               Interfaces van alle providers die deze context ondersteunen, weergeven
               Eigenschappen van schaduwkopieën verkrijgenContext:
               Provider-id: {262b716e-bb23-41b5-aaef-e2c15e767167}
               Klasse-id: {790f2886-9889-4c99-8ef5-531add05d044}
               Context van snapshot: 25
               Context van snapshot: 25
               Uitvoeringscontext: CoordinatorError: (06/10/2018 02:51:47 PM) (Source: VSS) (EventID: 13) (User: )
            Description: Informatie voor de Volume Shadow Copy-service: de COM-server met CLSID {790f2886-9889-4c99-8ef5-531add05d044} en de naam SW_PROV kan niet worden gestart. [0x80110802]
            Bewerking:
               Aanroepbare interface voor deze provider verkrijgen
               Interfaces van alle providers die deze context ondersteunen, weergeven
               Eigenschappen van schaduwkopieën verkrijgenContext:
               Provider-id: {262b716e-bb23-41b5-aaef-e2c15e767167}
               Klasse-id: {790f2886-9889-4c99-8ef5-531add05d044}
               Context van snapshot: 25
               Context van snapshot: 25
               Uitvoeringscontext: CoordinatorError: (06/10/2018 02:51:47 PM) (Source: VSS) (EventID: 12292) (User: )
            Description: Fout in de Volume Shadow Copy-service: fout bij het maken van de COM-klasse van de schaduwkopieprovider met CLSID {790f2886-9889-4c99-8ef5-531add05d044} [0x80110802].
            Bewerking:
               Aanroepbare interface voor deze provider verkrijgen
               Interfaces van alle providers die deze context ondersteunen, weergeven
               Eigenschappen van schaduwkopieën verkrijgenContext:
               Provider-id: {262b716e-bb23-41b5-aaef-e2c15e767167}
               Klasse-id: {790f2886-9889-4c99-8ef5-531add05d044}
               Context van snapshot: 25
               Context van snapshot: 25
               Uitvoeringscontext: CoordinatorError: (06/10/2018 02:51:47 PM) (Source: VSS) (EventID: 13) (User: )
            Description: Informatie voor de Volume Shadow Copy-service: de COM-server met CLSID {790f2886-9889-4c99-8ef5-531add05d044} en de naam SW_PROV kan niet worden gestart. [0x80110802]
            Bewerking:
               Aanroepbare interface voor deze provider verkrijgen
               Interfaces van alle providers die deze context ondersteunen, weergeven
               Eigenschappen van schaduwkopieën verkrijgenContext:
               Provider-id: {262b716e-bb23-41b5-aaef-e2c15e767167}
               Klasse-id: {790f2886-9889-4c99-8ef5-531add05d044}
               Context van snapshot: 25
               Context van snapshot: 25
               Uitvoeringscontext: CoordinatorError: (06/10/2018 02:51:44 PM) (Source: VSS) (EventID: 12292) (User: )
            Description: Fout in de Volume Shadow Copy-service: fout bij het maken van de COM-klasse van de schaduwkopieprovider met CLSID {790f2886-9889-4c99-8ef5-531add05d044} [0x80110802].
            Bewerking:
               Aanroepbare interface voor deze provider verkrijgen
               Interfaces van alle providers die deze context ondersteunen, weergeven
               Eigenschappen van schaduwkopieën verkrijgenContext:
               Provider-id: {262b716e-bb23-41b5-aaef-e2c15e767167}
               Klasse-id: {790f2886-9889-4c99-8ef5-531add05d044}
               Context van snapshot: 25
               Context van snapshot: 25
               Uitvoeringscontext: CoordinatorError: (06/10/2018 02:51:44 PM) (Source: VSS) (EventID: 13) (User: )
            Description: Informatie voor de Volume Shadow Copy-service: de COM-server met CLSID {790f2886-9889-4c99-8ef5-531add05d044} en de naam SW_PROV kan niet worden gestart. [0x80110802]
            Bewerking:
               Aanroepbare interface voor deze provider verkrijgen
               Interfaces van alle providers die deze context ondersteunen, weergeven
               Eigenschappen van schaduwkopieën verkrijgenContext:
               Provider-id: {262b716e
            Intel Core i5-661/3,33GHz ; 2x2GB ; Windows 7 Home Premium 64 bit ; Microsoft Office 2010 Professional Plus ; HD1=500GB ; HD2=160GB ; Norton Security 5 ; CCleaner ; Malwarebytes Anti-Malware ;Windows Live Mail 2012.
              Citeer
              abbs 13 jun 2018, 11:12 Leidschendam 1.589 berichten
              Hallo,

              Ik zie dat je ook illegale programma's gebruikt kijk daar mee uit want je bent een open verbinding voor meer problemen.

              Lees eerst de handleiding en voer daarna de fix uit Handleiding Fix

              Note: Dit script is speciaal bedoeld voor deze computer, gebruik dit dan ook niet op andere computers met een gelijkaardig probleem.

              Klik Windows knop plus R tegelijk in. Afbeelding
              "Uitvoeren" opent vul daar Notepad in en klik daarna op "OK", Kladblok opent.
              Kopieer onderstaande code en plak dat in "Kladblok"

              Code: Selecteer alles

              start
              CreateRestorePoint:
              (AVAST Software) C:\Program Files\AVAST Software\Avast\AvastUI.exe
              HKLM\...\Run: [AvastUI.exe] => C:\Program Files\AVAST Software\Avast\AvLaunch.exe [242904 2018-06-10] (AVAST Software)
              SearchScopes: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> DefaultScope {AFBCB7E0-F91A-4951-9F31-58FEE57A25C4} URL =
              BHO: avast! Online Security -> {8E5E2654-AD2D-48bf-AC2D-D17F00898D06} -> C:\Program Files\AVAST Software\Avast\aswWebRepIE64.dll [2018-06-10] (AVAST Software)
              BHO-x32: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
              BHO: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
              Toolbar: HKLM - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
              Toolbar: HKLM-x32 - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
              CHR HKLM-x32\...\Chrome\Extension: [nneajnkjbffgblleaoojgaacokifdkhm] - <geen Path/update_url>
              S3 aswbIDSAgent; C:\Program Files\AVAST Software\Avast\x64\aswidsagenta.exe [7620096 2018-06-10] (AVAST Software)
              R2 avast! Antivirus; C:\Program Files\AVAST Software\Avast\AvastSvc.exe [317280 2018-06-10] (AVAST Software)
              U5 AppMgmt; C:\Windows\system32\svchost.exe [27136 2009-07-14] (Microsoft Corporation) <==== AANDACHT (geen ServiceDLL)
              S3 aswArPot; C:\Windows\System32\drivers\aswArPot.sys [196640 2018-06-10] (AVAST Software)
              S3 aswbidsdriver; C:\Windows\System32\drivers\aswbidsdrivera.sys [227504 2018-06-10] (AVAST Software)
              S3 aswbidsh; C:\Windows\System32\drivers\aswbidsha.sys [199440 2018-06-10] (AVAST Software)
              S3 aswblog; C:\Windows\System32\drivers\aswbloga.sys [343752 2018-06-10] (AVAST Software)
              S3 aswbuniv; C:\Windows\System32\drivers\aswbuniva.sys [57680 2018-06-10] (AVAST Software)
              R1 aswHdsKe; C:\Windows\System32\drivers\aswHdsKe.sys [234560 2018-06-10] (AVAST Software)
              S3 aswHwid; C:\Windows\System32\drivers\aswHwid.sys [46968 2018-06-10] (AVAST Software)
              R2 aswMonFlt; C:\Windows\System32\drivers\aswMonFlt.sys [159120 2018-06-10] (AVAST Software)
              S3 aswRdr; C:\Windows\System32\drivers\aswRdr2.sys [111360 2018-06-10] (AVAST Software)
              R0 aswRvrt; C:\Windows\System32\drivers\aswRvrt.sys [85968 2018-06-10] (AVAST Software)
              S3 aswSnx; C:\Windows\System32\drivers\aswSnx.sys [1027720 2018-06-10] (AVAST Software)
              R1 aswSP; C:\Windows\System32\drivers\aswSP.sys [460520 2018-06-10] (AVAST Software)
              S3 aswStm; C:\Windows\System32\drivers\aswStm.sys [205976 2018-06-10] (AVAST Software)
              S3 aswVmm; C:\Windows\System32\drivers\aswVmm.sys [381552 2018-06-10] (AVAST Software)
              2018-06-10 10:41 - 2018-06-10 10:41 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\AVAST Software
              2018-06-10 10:30 - 2018-06-10 10:40 - 000000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\AVAST Software
              2018-06-10 10:28 - 2018-06-10 10:28 - 000000000 ____D C:\Program Files\Common Files\AVAST Software
              2018-06-10 10:28 - 2018-06-10 10:27 - 001027720 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSnx.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000460520 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSP.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000381552 _____ (AVAST Software) C:\Windows\system32\Drivers\aswVmm.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000376536 _____ (AVAST Software) C:\Windows\system32\aswBoot.exe
              2018-06-10 10:28 - 2018-06-10 10:27 - 000343752 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbloga.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000234560 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHdsKe.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000227504 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsdrivera.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000205976 _____ (AVAST Software) C:\Windows\system32\Drivers\aswStm.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000199440 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsha.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000196640 _____ (AVAST Software) C:\Windows\system32\Drivers\aswArPot.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000159120 _____ (AVAST Software) C:\Windows\system32\Drivers\aswMonFlt.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000111360 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRdr2.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000085968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRvrt.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000057680 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbuniva.sys
              2018-06-10 10:28 - 2018-06-10 10:27 - 000046968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHwid.sys
              2018-06-10 10:26 - 2018-06-10 12:21 - 000000000 ____D C:\ProgramData\AVAST Software
              2018-06-10 10:26 - 2018-06-10 10:26 - 000000000 ____D C:\Program Files\AVAST Software
              ShellIconOverlayIdentifiers: [00asw] -> {472083B0-C522-11CF-8763-00608CC02F24} => C:\Program Files\AVAST Software\Avast\ashShA64.dll [2018-06-10] (AVAST Software)
              Task: {C80EBC05-8E12-4122-A661-9511ED2282C0} - \Avast Emergency Update -> Geen bestand <==== AANDACHT
              EmptyTemp:
              Reboot:
              end
              
              Ga naar Bestand - Opslaan als.
              Kies als locatie bureaublad.
              Bij "Bestandsnaam" zet je:fixlist.txt
              Bij "Opslaan als type" selecteer je: Alle bestanden.

              Als het goed is staat er nu een text bestand op je bureaublad?

              Start de Farbar Recovery Scan Tool.
              Als het programma is geopend klik Yes (Ja) bij de disclaimer. (indien nodig)
              Druk op de Fix knop.
              Er zal u een logbestand aangemaakt worden (fixlog.txt) op dezelfde plaats vanwaar de 'tool' is gestart.
              Kopieer en plak de inhoud van de logbestanden in je het volgende bericht.
              Groeten abbs
              Afbeelding
              Member of UNITE (Unified Network of Instructors and Trained Eliminators)
                Citeer
                WillyV Startte dit onderwerp 15 jun 2018, 14:47 2030 Antwerpen 645 berichten
                abbs,

                Hier het logje van fixlog.txt :

                Fix resultaat van Farbar Recovery Scan Tool (x64) Versie: 06.06.2018 01
                Gestart door Gebruiker (15-06-2018 14:35:11) Run:1
                Gestart vanaf C:\Users\Gebruiker\Desktop
                Geladen Profielen: Gebruiker (Beschikbare Profielen: Gebruiker)
                Boot Modus: Normal
                ==============================================fixlist inhoud:
                *****************
                start
                 CreateRestorePoint:
                 (AVAST Software) C:\Program Files\AVAST Software\Avast\AvastUI.exe
                 HKLM\...\Run: [AvastUI.exe] => C:\Program Files\AVAST Software\Avast\AvLaunch.exe [242904 2018-06-10] (AVAST Software)
                 SearchScopes: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> DefaultScope {AFBCB7E0-F91A-4951-9F31-58FEE57A25C4} URL =
                 BHO: avast! Online Security -> {8E5E2654-AD2D-48bf-AC2D-D17F00898D06} -> C:\Program Files\AVAST Software\Avast\aswWebRepIE64.dll [2018-06-10] (AVAST Software)
                 BHO-x32: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
                 BHO: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
                 Toolbar: HKLM - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
                 Toolbar: HKLM-x32 - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
                 CHR HKLM-x32\...\Chrome\Extension: [nneajnkjbffgblleaoojgaacokifdkhm] - <geen Path/update_url>
                 S3 aswbIDSAgent; C:\Program Files\AVAST Software\Avast\x64\aswidsagenta.exe [7620096 2018-06-10] (AVAST Software)
                 R2 avast! Antivirus; C:\Program Files\AVAST Software\Avast\AvastSvc.exe [317280 2018-06-10] (AVAST Software)
                 U5 AppMgmt; C:\Windows\system32\svchost.exe [27136 2009-07-14] (Microsoft Corporation) <==== AANDACHT (geen ServiceDLL)
                 S3 aswArPot; C:\Windows\System32\drivers\aswArPot.sys [196640 2018-06-10] (AVAST Software)
                 S3 aswbidsdriver; C:\Windows\System32\drivers\aswbidsdrivera.sys [227504 2018-06-10] (AVAST Software)
                 S3 aswbidsh; C:\Windows\System32\drivers\aswbidsha.sys [199440 2018-06-10] (AVAST Software)
                 S3 aswblog; C:\Windows\System32\drivers\aswbloga.sys [343752 2018-06-10] (AVAST Software)
                 S3 aswbuniv; C:\Windows\System32\drivers\aswbuniva.sys [57680 2018-06-10] (AVAST Software)
                 R1 aswHdsKe; C:\Windows\System32\drivers\aswHdsKe.sys [234560 2018-06-10] (AVAST Software)
                 S3 aswHwid; C:\Windows\System32\drivers\aswHwid.sys [46968 2018-06-10] (AVAST Software)
                 R2 aswMonFlt; C:\Windows\System32\drivers\aswMonFlt.sys [159120 2018-06-10] (AVAST Software)
                 S3 aswRdr; C:\Windows\System32\drivers\aswRdr2.sys [111360 2018-06-10] (AVAST Software)
                 R0 aswRvrt; C:\Windows\System32\drivers\aswRvrt.sys [85968 2018-06-10] (AVAST Software)
                 S3 aswSnx; C:\Windows\System32\drivers\aswSnx.sys [1027720 2018-06-10] (AVAST Software)
                 R1 aswSP; C:\Windows\System32\drivers\aswSP.sys [460520 2018-06-10] (AVAST Software)
                 S3 aswStm; C:\Windows\System32\drivers\aswStm.sys [205976 2018-06-10] (AVAST Software)
                 S3 aswVmm; C:\Windows\System32\drivers\aswVmm.sys [381552 2018-06-10] (AVAST Software)
                 2018-06-10 10:41 - 2018-06-10 10:41 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\AVAST Software
                 2018-06-10 10:30 - 2018-06-10 10:40 - 000000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\AVAST Software
                 2018-06-10 10:28 - 2018-06-10 10:28 - 000000000 ____D C:\Program Files\Common Files\AVAST Software
                 2018-06-10 10:28 - 2018-06-10 10:27 - 001027720 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSnx.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000460520 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSP.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000381552 _____ (AVAST Software) C:\Windows\system32\Drivers\aswVmm.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000376536 _____ (AVAST Software) C:\Windows\system32\aswBoot.exe
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000343752 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbloga.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000234560 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHdsKe.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000227504 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsdrivera.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000205976 _____ (AVAST Software) C:\Windows\system32\Drivers\aswStm.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000199440 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsha.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000196640 _____ (AVAST Software) C:\Windows\system32\Drivers\aswArPot.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000159120 _____ (AVAST Software) C:\Windows\system32\Drivers\aswMonFlt.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000111360 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRdr2.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000085968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRvrt.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000057680 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbuniva.sys
                 2018-06-10 10:28 - 2018-06-10 10:27 - 000046968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHwid.sys
                 2018-06-10 10:26 - 2018-06-10 12:21 - 000000000 ____D C:\ProgramData\AVAST Software
                 2018-06-10 10:26 - 2018-06-10 10:26 - 000000000 ____D C:\Program Files\AVAST Software
                 ShellIconOverlayIdentifiers: [00asw] -> {472083B0-C522-11CF-8763-00608CC02F24} => C:\Program Files\AVAST Software\Avast\ashShA64.dll [2018-06-10] (AVAST Software)
                 Task: {C80EBC05-8E12-4122-A661-9511ED2282C0} - \Avast Emergency Update -> Geen bestand <==== AANDACHT
                 EmptyTemp:
                 Reboot:
                 end
                *****************Herstelpunt is succesvol gemaakt.
                C:\Program Files\AVAST Software\Avast\AvastUI.exe => Kon het proces niet afsluiten
                "HKLM\Software\Microsoft\Windows\CurrentVersion\Run\\AvastUI.exe" => kon niet worden verwijderd
                "HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\SOFTWARE\Microsoft\Internet Explorer\SearchScopes\\DefaultScope" => is succesvol verwijderd
                "HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{8E5E2654-AD2D-48bf-AC2D-D17F00898D06}" => is succesvol verwijderd
                "HKLM\Software\Classes\CLSID\{8E5E2654-AD2D-48bf-AC2D-D17F00898D06}" => is succesvol verwijderd
                "HKLM\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{AA58ED58-01DD-4d91-8333-CF10577473F7}" => is succesvol verwijderd
                "HKLM\Software\Wow6432Node\Classes\CLSID\{AA58ED58-01DD-4d91-8333-CF10577473F7}" => is succesvol verwijderd
                "HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{AA58ED58-01DD-4d91-8333-CF10577473F7}" => is succesvol verwijderd
                "HKLM\Software\Classes\CLSID\{AA58ED58-01DD-4d91-8333-CF10577473F7}" => is succesvol verwijderd
                "HKLM\SOFTWARE\Microsoft\Internet Explorer\Toolbar\\{2318C2B1-4965-11d4-9B18-009027A5CD4F}" => is succesvol verwijderd
                "HKLM\Software\Classes\CLSID\{2318C2B1-4965-11d4-9B18-009027A5CD4F}" => is succesvol verwijderd
                "HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Toolbar\\{2318C2B1-4965-11d4-9B18-009027A5CD4F}" => is succesvol verwijderd
                "HKLM\Software\Wow6432Node\Classes\CLSID\{2318C2B1-4965-11d4-9B18-009027A5CD4F}" => is succesvol verwijderd
                "HKLM\SOFTWARE\Wow6432Node\Google\Chrome\Extensions\nneajnkjbffgblleaoojgaacokifdkhm" => is succesvol verwijderd
                HKLM\System\CurrentControlSet\Services\aswbIDSAgent => kon niet worden verwijderd, sleutel kan beschermd zijn
                avast! Antivirus => Kon service niet stoppen.
                HKLM\System\CurrentControlSet\Services\avast! Antivirus => kon niet worden verwijderd, sleutel kan beschermd zijn
                "HKLM\System\CurrentControlSet\Services\AppMgmt" => is succesvol verwijderd
                AppMgmt => dienst is succesvol verwijderd
                HKLM\System\CurrentControlSet\Services\aswArPot => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswbidsdriver => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswbidsh => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswblog => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswbuniv => kon niet worden verwijderd, sleutel kan beschermd zijn
                aswHdsKe => Kon service niet stoppen.
                "HKLM\System\CurrentControlSet\Services\aswHdsKe" => is succesvol verwijderd
                aswHdsKe => dienst is succesvol verwijderd
                HKLM\System\CurrentControlSet\Services\aswHwid => kon niet worden verwijderd, sleutel kan beschermd zijn
                aswMonFlt => Kon service niet stoppen.
                HKLM\System\CurrentControlSet\Services\aswMonFlt => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswRdr => kon niet worden verwijderd, sleutel kan beschermd zijn
                aswRvrt => Service succesvol gestopt.
                HKLM\System\CurrentControlSet\Services\aswRvrt => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswSnx => kon niet worden verwijderd, sleutel kan beschermd zijn
                aswSP => Kon service niet stoppen.
                HKLM\System\CurrentControlSet\Services\aswSP => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswStm => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswVmm => kon niet worden verwijderd, sleutel kan beschermd zijn"C:\Users\Gebruiker\AppData\Roaming\AVAST Software" map verplaatsing:Kon niet verplaatsen "C:\Users\Gebruiker\AppData\Roaming\AVAST Software" => Gepland om te verplaatsen bij herstart.C:\ProgramData\Microsoft\Windows\Start Menu\Programs\AVAST Software => is succesvol verplaatst
                C:\Program Files\Common Files\AVAST Software => is succesvol verplaatst
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswSnx.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswSP.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswVmm.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\aswBoot.exe" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswbloga.sys" => Gepland om te verplaatsen bij herstart.
                C:\Windows\system32\Drivers\aswHdsKe.sys => is succesvol verplaatst
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswbidsdrivera.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswStm.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswbidsha.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswArPot.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswMonFlt.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswRdr2.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswRvrt.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswbuniva.sys" => Gepland om te verplaatsen bij herstart.
                Kon niet verplaatsen "C:\Windows\system32\Drivers\aswHwid.sys" => Gepland om te verplaatsen bij herstart."C:\ProgramData\AVAST Software" map verplaatsing:Kon niet verplaatsen "C:\ProgramData\AVAST Software" => Gepland om te verplaatsen bij herstart.
                "C:\Program Files\AVAST Software" map verplaatsing:Kon niet verplaatsen "C:\Program Files\AVAST Software" => Gepland om te verplaatsen bij herstart."HKLM\Software\Microsoft\Windows\CurrentVersion\Explorer\ShellIconOverlayIdentifiers\00asw" => is succesvol verwijderd
                "HKLM\Software\Classes\CLSID\{472083B0-C522-11CF-8763-00608CC02F24}" => is succesvol verwijderd
                "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Boot\{C80EBC05-8E12-4122-A661-9511ED2282C0}" => is succesvol verwijderd
                "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{C80EBC05-8E12-4122-A661-9511ED2282C0}" => is succesvol verwijderd
                "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Avast Emergency Update" => is succesvol verwijderd=========== EmptyTemp: ==========BITS transfer queue => 8388608 B
                DOMStore, IE Recovery, AppCache, Feeds Cache, Thumbcache, IconCache => 10252067 B
                Java, Flash, Steam htmlcache => 524 B
                Windows/system/drivers => 557000 B
                Edge => 0 B
                Chrome => 0 B
                Firefox => 0 B
                Opera => 0 BTemp, IE cache, history, cookies, recent:
                Users => 0 B
                Default => 0 B
                Public => 0 B
                ProgramData => 0 B
                systemprofile => 0 B
                systemprofile32 => 128 B
                LocalService => 0 B
                NetworkService => 0 B
                Gebruiker => 6123371 BRecycleBin => 113325 B
                EmptyTemp: => 24.3 MB tijdelijke gegevens verwijderd.================================Resultaat van geplande bestanden te verplaatsen (Boot Modus: Normal) (Datum&Tijd: 15-06-2018 14:38:17)C:\Users\Gebruiker\AppData\Roaming\AVAST Software => is succesvol verplaatst
                C:\Windows\system32\Drivers\aswSnx.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswSP.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswVmm.sys => Kon niet verplaatsen
                C:\Windows\system32\aswBoot.exe => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswbloga.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswbidsdrivera.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswStm.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswbidsha.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswArPot.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswMonFlt.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswRdr2.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswRvrt.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswbuniva.sys => Kon niet verplaatsen
                C:\Windows\system32\Drivers\aswHwid.sys => Kon niet verplaatsen
                C:\ProgramData\AVAST Software => is succesvol verplaatst
                C:\Program Files\AVAST Software => is succesvol verplaatstResultaat van geplande sleutels te verwijderen na herstart:HKLM\System\CurrentControlSet\Services\aswbIDSAgent => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\avast! Antivirus => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswArPot => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswbidsdriver => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswbidsh => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswblog => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswbuniv => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswHwid => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswMonFlt => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswRdr => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswRvrt => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswSnx => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswSP => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswStm => kon niet worden verwijderd, sleutel kan beschermd zijn
                HKLM\System\CurrentControlSet\Services\aswVmm => kon niet worden verwijderd, sleutel kan beschermd zijn==== Eind van Fixlog 14:38:17 ====

                N.B.: Ik zit nog altijd met het probleem ,dat wanneer ik iets wil typen mijn blad steeds naar onder scrolt en ik daardoor niet kan zien wat ik type.

                mvg,

                WillyV
                Intel Core i5-661/3,33GHz ; 2x2GB ; Windows 7 Home Premium 64 bit ; Microsoft Office 2010 Professional Plus ; HD1=500GB ; HD2=160GB ; Norton Security 5 ; CCleaner ; Malwarebytes Anti-Malware ;Windows Live Mail 2012.
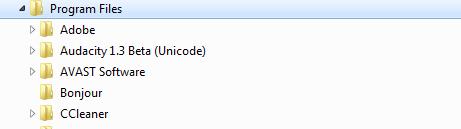
                  Citeer
                  abbs 16 jun 2018, 10:14 Leidschendam 1.589 berichten
                  N.B.: Ik zit nog altijd met het probleem ,dat wanneer ik iets wil typen mijn blad steeds naar onder scrolt en ik
                  daardoor niet kan zien wat ik type.
                  Is dit ook als je een Word document maakt of alleen als je via een browser werkt

                  Start Windows eens op in veilige modus https://nl.ccm.net/faq/19-windows-opsta ... lige-modus
                  Voer dan de fix met FRST tool nog eens uit zoals mik eerder had beschreven.
                  Groeten abbs
                  Afbeelding
                  Member of UNITE (Unified Network of Instructors and Trained Eliminators)
                    Citeer
                    WillyV Startte dit onderwerp 16 jun 2018, 17:42 2030 Antwerpen 645 berichten
                    abbs,

                    Met Word zijn er geen problemen.Het gebeurt enkel als ik via de browser werk.Met het schrijven van dit bericht veloopt alles normaal ; het scrollen gebeurt wanneer ik met de tekst op het einde van dit blad ben en verder type.

                    Wat bedoel je eigenlijk met :
                    Voer dan de fix met FRST tool nog eens uit zoals mik eerder had beschreven.
                    Wie is mik?En moet ik de fix uitvoeren in de veilige modus of nadat ik de PC terug heb opgestart?
                    N.B.: Sorry,maar Ik heb nog nooit in veilige modus gewerkt.Moet ik nadien de PC terug opstarten en start die dan terug normaal op?

                    WillyV
                    Intel Core i5-661/3,33GHz ; 2x2GB ; Windows 7 Home Premium 64 bit ; Microsoft Office 2010 Professional Plus ; HD1=500GB ; HD2=160GB ; Norton Security 5 ; CCleaner ; Malwarebytes Anti-Malware ;Windows Live Mail 2012.
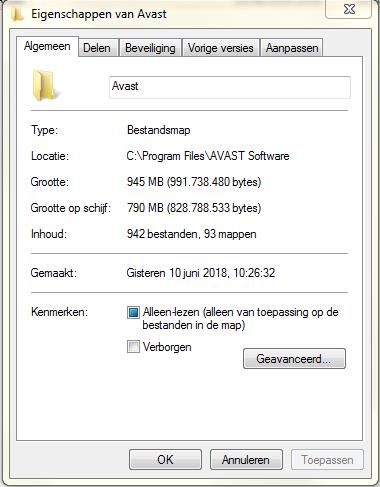
                      Citeer
                      abbs 16 jun 2018, 18:35 Leidschendam 1.589 berichten
                      WillyV schreef:abbs,

                      Met Word zijn er geen problemen.Het gebeurt enkel als ik via de browser werk.Met het schrijven van dit bericht veloopt alles normaal ; het scrollen gebeurt wanneer ik met de tekst op het einde van dit blad ben en verder type.
                      Is dit een laptop of desktop pc?
                      Heb je al eens een andere browser geprobeert of daar ook het probleem met scrollen is?
                      Voer dan de fix met FRST tool nog eens uit zoals mik eerder had beschreven.
                      Wie is mik?En moet ik de fix uitvoeren in de veilige modus of nadat ik de PC terug heb opgestart?
                      N.B.: Sorry,maar Ik heb nog nooit in veilige modus gewerkt.Moet ik nadien de PC terug opstarten en start die dan terug normaal op?
                      Liever vragen als fouten maken, mik moet ik zijn type fout.

                      Je moet opstarten in veilige modus en voer dan dan weer FRST zo uit:


                      Lees eerst de handleiding en voer daarna de fix uit Handleiding Fix

                      Note: Dit script is speciaal bedoeld voor deze computer, gebruik dit dan ook niet op andere computers met een gelijkaardig probleem.

                      Klik Windows knop plus R tegelijk in. Afbeelding
                      "Uitvoeren" opent vul daar Notepad in en klik daarna op "OK", Kladblok opent.
                      Kopieer onderstaande code en plak dat in "Kladblok"

                      Code: Selecteer alles

                      start
                      CreateRestorePoint:
                      (AVAST Software) C:\Program Files\AVAST Software\Avast\AvastUI.exe
                      HKLM\...\Run: [AvastUI.exe] => C:\Program Files\AVAST Software\Avast\AvLaunch.exe [242904 2018-06-10] (AVAST Software)
                      SearchScopes: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> DefaultScope {AFBCB7E0-F91A-4951-9F31-58FEE57A25C4} URL =
                      BHO: avast! Online Security -> {8E5E2654-AD2D-48bf-AC2D-D17F00898D06} -> C:\Program Files\AVAST Software\Avast\aswWebRepIE64.dll [2018-06-10] (AVAST Software)
                      BHO-x32: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
                      BHO: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
                      Toolbar: HKLM - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
                      Toolbar: HKLM-x32 - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
                      CHR HKLM-x32\...\Chrome\Extension: [nneajnkjbffgblleaoojgaacokifdkhm] - <geen Path/update_url>
                      S3 aswbIDSAgent; C:\Program Files\AVAST Software\Avast\x64\aswidsagenta.exe [7620096 2018-06-10] (AVAST Software)
                      R2 avast! Antivirus; C:\Program Files\AVAST Software\Avast\AvastSvc.exe [317280 2018-06-10] (AVAST Software)
                      U5 AppMgmt; C:\Windows\system32\svchost.exe [27136 2009-07-14] (Microsoft Corporation) <==== AANDACHT (geen ServiceDLL)
                      S3 aswArPot; C:\Windows\System32\drivers\aswArPot.sys [196640 2018-06-10] (AVAST Software)
                      S3 aswbidsdriver; C:\Windows\System32\drivers\aswbidsdrivera.sys [227504 2018-06-10] (AVAST Software)
                      S3 aswbidsh; C:\Windows\System32\drivers\aswbidsha.sys [199440 2018-06-10] (AVAST Software)
                      S3 aswblog; C:\Windows\System32\drivers\aswbloga.sys [343752 2018-06-10] (AVAST Software)
                      S3 aswbuniv; C:\Windows\System32\drivers\aswbuniva.sys [57680 2018-06-10] (AVAST Software)
                      R1 aswHdsKe; C:\Windows\System32\drivers\aswHdsKe.sys [234560 2018-06-10] (AVAST Software)
                      S3 aswHwid; C:\Windows\System32\drivers\aswHwid.sys [46968 2018-06-10] (AVAST Software)
                      R2 aswMonFlt; C:\Windows\System32\drivers\aswMonFlt.sys [159120 2018-06-10] (AVAST Software)
                      S3 aswRdr; C:\Windows\System32\drivers\aswRdr2.sys [111360 2018-06-10] (AVAST Software)
                      R0 aswRvrt; C:\Windows\System32\drivers\aswRvrt.sys [85968 2018-06-10] (AVAST Software)
                      S3 aswSnx; C:\Windows\System32\drivers\aswSnx.sys [1027720 2018-06-10] (AVAST Software)
                      R1 aswSP; C:\Windows\System32\drivers\aswSP.sys [460520 2018-06-10] (AVAST Software)
                      S3 aswStm; C:\Windows\System32\drivers\aswStm.sys [205976 2018-06-10] (AVAST Software)
                      S3 aswVmm; C:\Windows\System32\drivers\aswVmm.sys [381552 2018-06-10] (AVAST Software)
                      2018-06-10 10:41 - 2018-06-10 10:41 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\AVAST Software
                      2018-06-10 10:30 - 2018-06-10 10:40 - 000000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\AVAST Software
                      2018-06-10 10:28 - 2018-06-10 10:28 - 000000000 ____D C:\Program Files\Common Files\AVAST Software
                      2018-06-10 10:28 - 2018-06-10 10:27 - 001027720 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSnx.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000460520 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSP.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000381552 _____ (AVAST Software) C:\Windows\system32\Drivers\aswVmm.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000376536 _____ (AVAST Software) C:\Windows\system32\aswBoot.exe
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000343752 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbloga.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000234560 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHdsKe.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000227504 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsdrivera.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000205976 _____ (AVAST Software) C:\Windows\system32\Drivers\aswStm.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000199440 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsha.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000196640 _____ (AVAST Software) C:\Windows\system32\Drivers\aswArPot.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000159120 _____ (AVAST Software) C:\Windows\system32\Drivers\aswMonFlt.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000111360 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRdr2.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000085968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRvrt.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000057680 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbuniva.sys
                      2018-06-10 10:28 - 2018-06-10 10:27 - 000046968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHwid.sys
                      2018-06-10 10:26 - 2018-06-10 12:21 - 000000000 ____D C:\ProgramData\AVAST Software
                      2018-06-10 10:26 - 2018-06-10 10:26 - 000000000 ____D C:\Program Files\AVAST Software
                      ShellIconOverlayIdentifiers: [00asw] -> {472083B0-C522-11CF-8763-00608CC02F24} => C:\Program Files\AVAST Software\Avast\ashShA64.dll [2018-06-10] (AVAST Software)
                      Task: {C80EBC05-8E12-4122-A661-9511ED2282C0} - \Avast Emergency Update -> Geen bestand <==== AANDACHT
                      EmptyTemp:
                      Reboot:
                      end
                      
                      Ga naar Bestand - Opslaan als.
                      Kies als locatie bureaublad.
                      Bij "Bestandsnaam" zet je:fixlist.txt
                      Bij "Opslaan als type" selecteer je: Alle bestanden.

                      Als het goed is staat er nu een text bestand op je bureaublad?

                      Start de Farbar Recovery Scan Tool.
                      Als het programma is geopend klik Yes (Ja) bij de disclaimer. (indien nodig)
                      Druk op de Fix knop.
                      Er zal u een logbestand aangemaakt worden (fixlog.txt) op dezelfde plaats vanwaar de 'tool' is gestart.
                      Kopieer en plak de inhoud van de logbestanden in je het volgende bericht.


                      Hierna mag de pc in normale modus weer opstarten.
                      Groeten abbs
                      Afbeelding
                      Member of UNITE (Unified Network of Instructors and Trained Eliminators)
                        Citeer
                        WillyV Startte dit onderwerp 17 jun 2018, 11:28 2030 Antwerpen 645 berichten
                        abbs,

                        Mijn PC is een desktop.
                        Ik heb nog nooit met een andere browser geëxperimenteerd ; heb nog nooit last gehad met I.E. 11. Heb jij een suggestie welke browser ik zou kunnen installeren en hoe moet ik dat doen?
                        Wanneer ik in veilige modus opstart,krijg ik volgende melding : Uw PC heeft geen verbinding met het netwerk.
                        Daardoor kan ik Sennet niet openen en ook geen andere items die langs I.E. openen.


                        Afbeelding

                        In de normale modus is alles nochtans normaal.

                        WillyV
                        Intel Core i5-661/3,33GHz ; 2x2GB ; Windows 7 Home Premium 64 bit ; Microsoft Office 2010 Professional Plus ; HD1=500GB ; HD2=160GB ; Norton Security 5 ; CCleaner ; Malwarebytes Anti-Malware ;Windows Live Mail 2012.
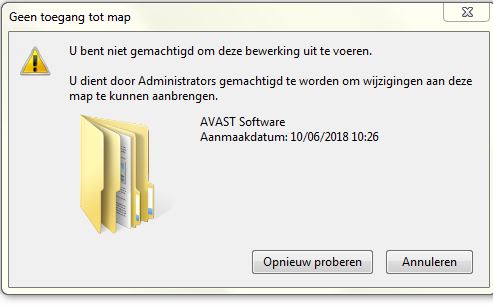
                          Citeer
                          abbs 17 jun 2018, 19:05 Leidschendam 1.589 berichten
                          Hallo,

                          We gaan stap voor stap doen.

                          Stap 1.


                          Klik Windows knop plus R tegelijk in. Afbeelding
                          "Uitvoeren" opent vul daar Notepad in en klik daarna op "OK", Kladblok opent.
                          Kopieer onderstaande code en plak dat in "Kladblok"

                          Code: Selecteer alles

                          start
                          CreateRestorePoint:
                          (AVAST Software) C:\Program Files\AVAST Software\Avast\AvastUI.exe
                          HKLM\...\Run: [AvastUI.exe] => C:\Program Files\AVAST Software\Avast\AvLaunch.exe [242904 2018-06-10] (AVAST Software)
                          SearchScopes: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> DefaultScope {AFBCB7E0-F91A-4951-9F31-58FEE57A25C4} URL =
                          BHO: avast! Online Security -> {8E5E2654-AD2D-48bf-AC2D-D17F00898D06} -> C:\Program Files\AVAST Software\Avast\aswWebRepIE64.dll [2018-06-10] (AVAST Software)
                          BHO-x32: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
                          BHO: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
                          Toolbar: HKLM - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
                          Toolbar: HKLM-x32 - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
                          CHR HKLM-x32\...\Chrome\Extension: [nneajnkjbffgblleaoojgaacokifdkhm] - <geen Path/update_url>
                          S3 aswbIDSAgent; C:\Program Files\AVAST Software\Avast\x64\aswidsagenta.exe [7620096 2018-06-10] (AVAST Software)
                          R2 avast! Antivirus; C:\Program Files\AVAST Software\Avast\AvastSvc.exe [317280 2018-06-10] (AVAST Software)
                          U5 AppMgmt; C:\Windows\system32\svchost.exe [27136 2009-07-14] (Microsoft Corporation) <==== AANDACHT (geen ServiceDLL)
                          S3 aswArPot; C:\Windows\System32\drivers\aswArPot.sys [196640 2018-06-10] (AVAST Software)
                          S3 aswbidsdriver; C:\Windows\System32\drivers\aswbidsdrivera.sys [227504 2018-06-10] (AVAST Software)
                          S3 aswbidsh; C:\Windows\System32\drivers\aswbidsha.sys [199440 2018-06-10] (AVAST Software)
                          S3 aswblog; C:\Windows\System32\drivers\aswbloga.sys [343752 2018-06-10] (AVAST Software)
                          S3 aswbuniv; C:\Windows\System32\drivers\aswbuniva.sys [57680 2018-06-10] (AVAST Software)
                          R1 aswHdsKe; C:\Windows\System32\drivers\aswHdsKe.sys [234560 2018-06-10] (AVAST Software)
                          S3 aswHwid; C:\Windows\System32\drivers\aswHwid.sys [46968 2018-06-10] (AVAST Software)
                          R2 aswMonFlt; C:\Windows\System32\drivers\aswMonFlt.sys [159120 2018-06-10] (AVAST Software)
                          S3 aswRdr; C:\Windows\System32\drivers\aswRdr2.sys [111360 2018-06-10] (AVAST Software)
                          R0 aswRvrt; C:\Windows\System32\drivers\aswRvrt.sys [85968 2018-06-10] (AVAST Software)
                          S3 aswSnx; C:\Windows\System32\drivers\aswSnx.sys [1027720 2018-06-10] (AVAST Software)
                          R1 aswSP; C:\Windows\System32\drivers\aswSP.sys [460520 2018-06-10] (AVAST Software)
                          S3 aswStm; C:\Windows\System32\drivers\aswStm.sys [205976 2018-06-10] (AVAST Software)
                          S3 aswVmm; C:\Windows\System32\drivers\aswVmm.sys [381552 2018-06-10] (AVAST Software)
                          2018-06-10 10:41 - 2018-06-10 10:41 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\AVAST Software
                          2018-06-10 10:30 - 2018-06-10 10:40 - 000000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\AVAST Software
                          2018-06-10 10:28 - 2018-06-10 10:28 - 000000000 ____D C:\Program Files\Common Files\AVAST Software
                          2018-06-10 10:28 - 2018-06-10 10:27 - 001027720 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSnx.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000460520 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSP.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000381552 _____ (AVAST Software) C:\Windows\system32\Drivers\aswVmm.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000376536 _____ (AVAST Software) C:\Windows\system32\aswBoot.exe
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000343752 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbloga.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000234560 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHdsKe.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000227504 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsdrivera.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000205976 _____ (AVAST Software) C:\Windows\system32\Drivers\aswStm.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000199440 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsha.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000196640 _____ (AVAST Software) C:\Windows\system32\Drivers\aswArPot.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000159120 _____ (AVAST Software) C:\Windows\system32\Drivers\aswMonFlt.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000111360 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRdr2.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000085968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRvrt.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000057680 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbuniva.sys
                          2018-06-10 10:28 - 2018-06-10 10:27 - 000046968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHwid.sys
                          2018-06-10 10:26 - 2018-06-10 12:21 - 000000000 ____D C:\ProgramData\AVAST Software
                          2018-06-10 10:26 - 2018-06-10 10:26 - 000000000 ____D C:\Program Files\AVAST Software
                          ShellIconOverlayIdentifiers: [00asw] -> {472083B0-C522-11CF-8763-00608CC02F24} => C:\Program Files\AVAST Software\Avast\ashShA64.dll [2018-06-10] (AVAST Software)
                          Task: {C80EBC05-8E12-4122-A661-9511ED2282C0} - \Avast Emergency Update -> Geen bestand <==== AANDACHT
                          EmptyTemp:
                          Reboot:
                          end
                          
                          Ga naar Bestand - Opslaan als.
                          Kies als locatie bureaublad.
                          Bij "Bestandsnaam" zet je:fixlist.txt
                          Bij "Opslaan als type" selecteer je: Alle bestanden.

                          Als het goed is staat er nu een text bestand op je bureaublad?


                          Stap 2.
                          Start Windows eens op in veilige modus https://nl.ccm.net/faq/19-windows-opsta ... lige-modus
                          Je heb geen netwerk nodig om de fix uit te voeren.


                          Stap 3.
                          Start de Farbar Recovery Scan Tool.
                          Als het programma is geopend klik Yes (Ja) bij de disclaimer. (indien nodig)
                          Druk op de Fix knop.
                          Er zal u een logbestand aangemaakt worden (fixlog.txt) op dezelfde plaats vanwaar de 'tool' is gestart.
                          Kopieer en plak de inhoud van de logbestanden in je het volgende bericht.


                          Hierna mag de pc in normale modus weer opstarten.
                          Groeten abbs
                          Afbeelding
                          Member of UNITE (Unified Network of Instructors and Trained Eliminators)
                            Citeer
                            WillyV Startte dit onderwerp 18 jun 2018, 14:40 2030 Antwerpen 645 berichten
                            abbs,

                            Hier het gevraagde fixlog.txt bestand , gemaakt in veilige modus :

                            Fix resultaat van Farbar Recovery Scan Tool (x64) Versie: 06.06.2018 01
                            Gestart door Gebruiker (18-06-2018 14:31:28) Run:3
                            Gestart vanaf C:\Users\Gebruiker\Desktop
                            Geladen Profielen: Gebruiker (Beschikbare Profielen: Gebruiker)
                            Boot Modus: Safe Mode (minimal)
                            ==============================================fixlist inhoud:
                            *****************
                            Code:
                            start
                             CreateRestorePoint:
                             (AVAST Software) C:\Program Files\AVAST Software\Avast\AvastUI.exe
                             HKLM\...\Run: [AvastUI.exe] => C:\Program Files\AVAST Software\Avast\AvLaunch.exe [242904 2018-06-10] (AVAST Software)
                             SearchScopes: HKU\S-1-5-21-3233923740-3587472772-2755484448-1000 -> DefaultScope {AFBCB7E0-F91A-4951-9F31-58FEE57A25C4} URL =
                             BHO: avast! Online Security -> {8E5E2654-AD2D-48bf-AC2D-D17F00898D06} -> C:\Program Files\AVAST Software\Avast\aswWebRepIE64.dll [2018-06-10] (AVAST Software)
                             BHO-x32: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
                             BHO: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
                             Toolbar: HKLM - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2017-08-25] (Google Inc.)
                             Toolbar: HKLM-x32 - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2017-08-25] (Google Inc.)
                             CHR HKLM-x32\...\Chrome\Extension: [nneajnkjbffgblleaoojgaacokifdkhm] - <geen Path/update_url>
                             S3 aswbIDSAgent; C:\Program Files\AVAST Software\Avast\x64\aswidsagenta.exe [7620096 2018-06-10] (AVAST Software)
                             R2 avast! Antivirus; C:\Program Files\AVAST Software\Avast\AvastSvc.exe [317280 2018-06-10] (AVAST Software)
                             U5 AppMgmt; C:\Windows\system32\svchost.exe [27136 2009-07-14] (Microsoft Corporation) <==== AANDACHT (geen ServiceDLL)
                             S3 aswArPot; C:\Windows\System32\drivers\aswArPot.sys [196640 2018-06-10] (AVAST Software)
                             S3 aswbidsdriver; C:\Windows\System32\drivers\aswbidsdrivera.sys [227504 2018-06-10] (AVAST Software)
                             S3 aswbidsh; C:\Windows\System32\drivers\aswbidsha.sys [199440 2018-06-10] (AVAST Software)
                             S3 aswblog; C:\Windows\System32\drivers\aswbloga.sys [343752 2018-06-10] (AVAST Software)
                             S3 aswbuniv; C:\Windows\System32\drivers\aswbuniva.sys [57680 2018-06-10] (AVAST Software)
                             R1 aswHdsKe; C:\Windows\System32\drivers\aswHdsKe.sys [234560 2018-06-10] (AVAST Software)
                             S3 aswHwid; C:\Windows\System32\drivers\aswHwid.sys [46968 2018-06-10] (AVAST Software)
                             R2 aswMonFlt; C:\Windows\System32\drivers\aswMonFlt.sys [159120 2018-06-10] (AVAST Software)
                             S3 aswRdr; C:\Windows\System32\drivers\aswRdr2.sys [111360 2018-06-10] (AVAST Software)
                             R0 aswRvrt; C:\Windows\System32\drivers\aswRvrt.sys [85968 2018-06-10] (AVAST Software)
                             S3 aswSnx; C:\Windows\System32\drivers\aswSnx.sys [1027720 2018-06-10] (AVAST Software)
                             R1 aswSP; C:\Windows\System32\drivers\aswSP.sys [460520 2018-06-10] (AVAST Software)
                             S3 aswStm; C:\Windows\System32\drivers\aswStm.sys [205976 2018-06-10] (AVAST Software)
                             S3 aswVmm; C:\Windows\System32\drivers\aswVmm.sys [381552 2018-06-10] (AVAST Software)
                             2018-06-10 10:41 - 2018-06-10 10:41 - 000000000 ____D C:\Users\Gebruiker\AppData\Roaming\AVAST Software
                             2018-06-10 10:30 - 2018-06-10 10:40 - 000000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\AVAST Software
                             2018-06-10 10:28 - 2018-06-10 10:28 - 000000000 ____D C:\Program Files\Common Files\AVAST Software
                             2018-06-10 10:28 - 2018-06-10 10:27 - 001027720 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSnx.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000460520 _____ (AVAST Software) C:\Windows\system32\Drivers\aswSP.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000381552 _____ (AVAST Software) C:\Windows\system32\Drivers\aswVmm.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000376536 _____ (AVAST Software) C:\Windows\system32\aswBoot.exe
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000343752 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbloga.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000234560 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHdsKe.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000227504 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsdrivera.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000205976 _____ (AVAST Software) C:\Windows\system32\Drivers\aswStm.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000199440 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbidsha.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000196640 _____ (AVAST Software) C:\Windows\system32\Drivers\aswArPot.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000159120 _____ (AVAST Software) C:\Windows\system32\Drivers\aswMonFlt.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000111360 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRdr2.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000085968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswRvrt.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000057680 _____ (AVAST Software) C:\Windows\system32\Drivers\aswbuniva.sys
                             2018-06-10 10:28 - 2018-06-10 10:27 - 000046968 _____ (AVAST Software) C:\Windows\system32\Drivers\aswHwid.sys
                             2018-06-10 10:26 - 2018-06-10 12:21 - 000000000 ____D C:\ProgramData\AVAST Software
                             2018-06-10 10:26 - 2018-06-10 10:26 - 000000000 ____D C:\Program Files\AVAST Software
                             ShellIconOverlayIdentifiers: [00asw] -> {472083B0-C522-11CF-8763-00608CC02F24} => C:\Program Files\AVAST Software\Avast\ashShA64.dll [2018-06-10] (AVAST Software)
                             Task: {C80EBC05-8E12-4122-A661-9511ED2282C0} - \Avast Emergency Update -> Geen bestand <==== AANDACHT
                             EmptyTemp:
                             Reboot:
                             end
                             
                            *****************Code: => Fout: Geen automatische fix gevonden voor dit item.
                            Fout: Herstelpunt kan alleen worden gemaakt in normale modus.
                            C:\Program Files\AVAST Software\Avast\AvastUI.exe => Kon het proces niet afsluiten
                            "HKLM\Software\Microsoft\Windows\CurrentVersion\Run\\AvastUI.exe" => niet gevonden
                            "HKU\S-1-5-21-3233923740-3587472772-2755484448-1000\SOFTWARE\Microsoft\Internet Explorer\SearchScopes\\DefaultScope" => niet gevonden
                            HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{8E5E2654-AD2D-48bf-AC2D-D17F00898D06} => niet gevonden
                            HKLM\Software\Classes\CLSID\{8E5E2654-AD2D-48bf-AC2D-D17F00898D06} => niet gevonden
                            HKLM\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{AA58ED58-01DD-4d91-8333-CF10577473F7} => niet gevonden
                            HKLM\Software\Wow6432Node\Classes\CLSID\{AA58ED58-01DD-4d91-8333-CF10577473F7} => niet gevonden
                            HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{AA58ED58-01DD-4d91-8333-CF10577473F7} => niet gevonden
                            HKLM\Software\Classes\CLSID\{AA58ED58-01DD-4d91-8333-CF10577473F7} => niet gevonden
                            "HKLM\SOFTWARE\Microsoft\Internet Explorer\Toolbar\\{2318C2B1-4965-11d4-9B18-009027A5CD4F}" => niet gevonden
                            HKLM\Software\Classes\CLSID\{2318C2B1-4965-11d4-9B18-009027A5CD4F} => niet gevonden
                            "HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Toolbar\\{2318C2B1-4965-11d4-9B18-009027A5CD4F}" => niet gevonden
                            HKLM\Software\Wow6432Node\Classes\CLSID\{2318C2B1-4965-11d4-9B18-009027A5CD4F} => niet gevonden
                            HKLM\SOFTWARE\Wow6432Node\Google\Chrome\Extensions\nneajnkjbffgblleaoojgaacokifdkhm => niet gevonden
                            aswbIDSAgent => dienst niet gevonden.
                            avast! Antivirus => dienst niet gevonden.
                            AppMgmt => dienst niet gevonden.
                            aswArPot => dienst niet gevonden.
                            aswbidsdriver => dienst niet gevonden.
                            aswbidsh => dienst niet gevonden.
                            aswblog => dienst niet gevonden.
                            aswbuniv => dienst niet gevonden.
                            aswHdsKe => dienst niet gevonden.
                            aswHwid => dienst niet gevonden.
                            aswMonFlt => dienst niet gevonden.
                            aswRdr => dienst niet gevonden.
                            aswRvrt => dienst niet gevonden.
                            aswSnx => dienst niet gevonden.
                            aswSP => dienst niet gevonden.
                            aswStm => dienst niet gevonden.
                            aswVmm => dienst niet gevonden.
                            "C:\Users\Gebruiker\AppData\Roaming\AVAST Software" => niet gevonden
                            "C:\ProgramData\Microsoft\Windows\Start Menu\Programs\AVAST Software" => niet gevonden
                            "C:\Program Files\Common Files\AVAST Software" => niet gevonden
                            "C:\Windows\system32\Drivers\aswSnx.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswSP.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswVmm.sys" => niet gevonden
                            "C:\Windows\system32\aswBoot.exe" => niet gevonden
                            "C:\Windows\system32\Drivers\aswbloga.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswHdsKe.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswbidsdrivera.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswStm.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswbidsha.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswArPot.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswMonFlt.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswRdr2.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswRvrt.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswbuniva.sys" => niet gevonden
                            "C:\Windows\system32\Drivers\aswHwid.sys" => niet gevonden
                            "C:\ProgramData\AVAST Software" => niet gevonden
                            "C:\Program Files\AVAST Software" => niet gevonden
                            HKLM\Software\Microsoft\Windows\CurrentVersion\Explorer\ShellIconOverlayIdentifiers\00asw => niet gevonden
                            HKLM\Software\Classes\CLSID\{472083B0-C522-11CF-8763-00608CC02F24} => niet gevonden
                            HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{C80EBC05-8E12-4122-A661-9511ED2282C0} => niet gevonden
                            HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Avast Emergency Update => niet gevonden=========== EmptyTemp: ==========BITS transfer queue => 0 B
                            DOMStore, IE Recovery, AppCache, Feeds Cache, Thumbcache, IconCache => 1051928 B
                            Java, Flash, Steam htmlcache => 0 B
                            Windows/system/drivers => 0 B
                            Edge => 0 B
                            Chrome => 0 B
                            Firefox => 0 B
                            Opera => 0 BTemp, IE cache, history, cookies, recent:
                            Users => 0 B
                            Default => 0 B
                            Public => 0 B
                            ProgramData => 0 B
                            systemprofile => 0 B
                            systemprofile32 => 0 B
                            LocalService => 0 B
                            NetworkService => 0 B
                            Gebruiker => 0 BRecycleBin => 0 B
                            EmptyTemp: => 1027 KB tijdelijke gegevens verwijderd.================================
                            Het systeem moest herstart worden.==== Eind van Fixlog 14:31:42 ====

                            WillyV
                            Intel Core i5-661/3,33GHz ; 2x2GB ; Windows 7 Home Premium 64 bit ; Microsoft Office 2010 Professional Plus ; HD1=500GB ; HD2=160GB ; Norton Security 5 ; CCleaner ; Malwarebytes Anti-Malware ;Windows Live Mail 2012.
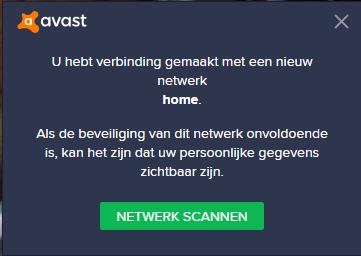
                              Citeer
                              abbs 18 jun 2018, 15:05 Leidschendam 1.589 berichten
                              Hallo,

                              Het logje zegt niks meer van avast gevonden ben kijk eens of je avast nog ziet op je pc?
                              Groeten abbs
                              Afbeelding
                              Member of UNITE (Unified Network of Instructors and Trained Eliminators)
                                Citeer

                                Schrijf gerust een antwoord

                                Om te antwoorden heb je een gratis account nodig. Heb je al een account, klik dan op "Aanmelden". Via "Gratis account maken" maak je er eenvoudig een in enkele minuten.