Hallo,
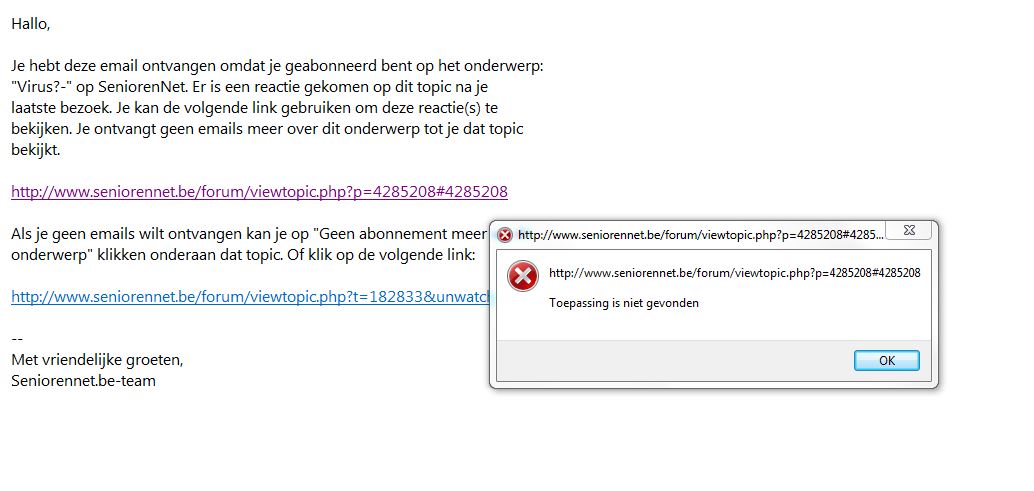
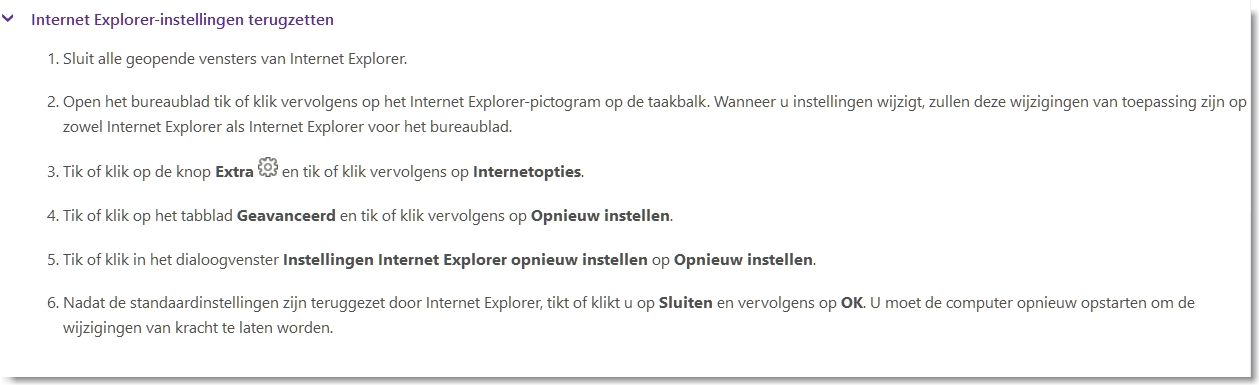
Ik hoop dat iemand mij kan helpen. Waarschijnlijk heb ik een virus op mijn PC. Genaamd Oosteran Browser. Wie weet ik daar van af kan komen. Kan geen eigen startpagina meer maken. en er komen alllerlei vervelende dingen op mijn scherm.
Logfile of Trend Micro HijackThis v2.0.4
Scan saved at 18:53:52, on 20-12-2014
Platform: Windows 7 SP1 (WinNT 6.00.3505)
MSIE: Internet Explorer v11.0 (11.00.9600.17496)
Boot mode: Normal
Running processes:
C:\Program Files (x86)\NVIDIA Corporation\Update Core\NvBackend.exe
C:\Program Files (x86)\Common Files\Ahead\Lib\NMBgMonitor.exe
C:\Users\MartinSr\AppData\Roaming\uTorrent\uTorrent.exe
C:\Program Files (x86)\HP\Digital Imaging\bin\hpqtra08.exe
C:\Program Files (x86)\Intel\Intel(R) Rapid Storage Technology\IAStorIcon.exe
C:\Program Files (x86)\Renesas Electronics\USB 3.0 Host Controller Driver\Application\nusb3mon.exe
C:\Program Files (x86)\CyberLink\Power2Go\CLMLSvc.exe
C:\Program Files (x86)\HP\HP Software Update\hpwuschd2.exe
C:\Program Files (x86)\Panda Security\Panda Security Protection\PSUAMain.exe
C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe
C:\Program Files (x86)\DigiHelp\bin\DigiHelp.BrowserAdapter.exe
C:\Program Files (x86)\DigiHelp\bin\DigiHelp.expext.exe
C:\Program Files (x86)\DigiHelp\bin\DigiHelp.BOASHelper.exe
C:\Program Files (x86)\HP\Digital Imaging\bin\hpqSTE08.exe
C:\Program Files (x86)\HP\Digital Imaging\bin\hpqbam08.exe
C:\Program Files (x86)\HP\Digital Imaging\bin\hpqgpc01.exe
C:\Program Files (x86)\HP\Digital Imaging\smart web printing\hpswp_clipbook.exe
C:\Program Files (x86)\Internet Explorer\IEXPLORE.EXE
C:\Program Files (x86)\DigiHelp\bin\DigiHelp.BOASPRT.exe
C:\Program Files (x86)\DigiHelp\bin\DigiHelp.BOAS.exe
C:\Users\MartinSr\Desktop\HijackThis.exe
R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://Vosteran.com/?f=1&a=vst_coinis_1 ... 327979&ir=
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/p/?LinkId=255141
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/p/?LinkId=255141
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Local Page = C:\Windows\SysWOW64\blank.htm
F2 - REG:system.ini: UserInit=C:\Windows\SysWOW64\userinit.exe,
O2 - BHO: HP Print Enhancer - {0347C33E-8762-4905-BF09-768834316C61} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_printenhancer.dll
O2 - BHO: DigiHelp 1.0.0.6 - {5bee7be9-df29-4c14-a18e-2bdd06205e29} - C:\Program Files (x86)\DigiHelp\DigiHelpbho.dll
O2 - BHO: Java(tm) Plug-In SSV Helper - {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} - C:\Program Files (x86)\Java\jre7\bin\ssv.dll
O2 - BHO: Aanmeldhulp voor Windows Live ID - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: Google Toolbar Helper - {AA58ED58-01DD-4d91-8333-CF10577473F7} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O2 - BHO: Java(tm) Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files (x86)\Java\jre7\bin\jp2ssv.dll
O2 - BHO: HP Smart BHO Class - {FFFFFFFF-CF4E-4F2B-BDC2-0E72E116A856} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_BHO.dll
O3 - Toolbar: Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O4 - HKLM\..\Run: [IAStorIcon] C:\Program Files (x86)\Intel\Intel(R) Rapid Storage Technology\IAStorIcon.exe
O4 - HKLM\..\Run: [NUSB3MON] "C:\Program Files (x86)\Renesas Electronics\USB 3.0 Host Controller Driver\Application\nusb3mon.exe"
O4 - HKLM\..\Run: [Microsoft Default Manager] "C:\Program Files (x86)\Microsoft\Search Enhancement Pack\Default Manager\DefMgr.exe" -resume
O4 - HKLM\..\Run: [CLMLServer] "C:\Program Files (x86)\CyberLink\Power2Go\CLMLSvc.exe"
O4 - HKLM\..\Run: [HP Software Update] C:\Program Files (x86)\HP\HP Software Update\HPWuSchd2.exe
O4 - HKLM\..\Run: [PSUAMain] "C:\Program Files (x86)\Panda Security\Panda Security Protection\PSUAMain.exe" /LaunchSysTray
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe"
O4 - HKLM\..\Run: [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
O4 - HKCU\..\Run: [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
O4 - HKCU\..\Run: [BgMonitor_{79662E04-7C6C-4d9f-84C7-88D8A56B10AA}] "C:\Program Files (x86)\Common Files\Ahead\Lib\NMBgMonitor.exe"
O4 - HKCU\..\Run: [uTorrent] "C:\Users\MartinSr\AppData\Roaming\uTorrent\uTorrent.exe" /MINIMIZED
O4 - HKCU\..\Run: [CCleaner Monitoring] "C:\Program Files\CCleaner\CCleaner64.exe" /MONITOR
O4 - HKCU\..\Run: [GoogleChromeAutoLaunch_A9CF17DBB2D93122F63C411A50CE9E45] "C:\Users\MartinSr\AppData\Local\Vosteran\Application\vosteran.exe" --auto-launch-at-startup --profile-directory="Default"
O4 - HKCU\..\RunOnce: [Adobe Speed Launcher] 1419097102
O4 - HKUS\S-1-5-19\..\Run: [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun (User 'LOCAL SERVICE')
O4 - HKUS\S-1-5-19\..\RunOnce: [mctadmin] C:\Windows\System32\mctadmin.exe (User 'LOCAL SERVICE')
O4 - HKUS\S-1-5-20\..\Run: [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun (User 'NETWORK SERVICE')
O4 - HKUS\S-1-5-20\..\RunOnce: [mctadmin] C:\Windows\System32\mctadmin.exe (User 'NETWORK SERVICE')
O4 - Startup: OpenOffice.org 3.3 .lnk = C:\Program Files (x86)\OpenOffice.org 3\program\quickstart.exe
O4 - Global Startup: HP Digital Imaging Monitor.lnk = C:\Program Files (x86)\HP\Digital Imaging\bin\hpqtra08.exe
O4 - Global Startup: Microsoft Office.lnk = C:\Program Files (x86)\Microsoft Office\Office\OSA9.EXE
O8 - Extra context menu item: E&xporteren naar Microsoft Excel - res://C:\PROGRA~2\MICROS~2\Office12\EXCEL.EXE/3000
O9 - Extra button: @C:\Program Files (x86)\Windows Live\Writer\WindowsLiveWriterShortcuts.dll,-1004 - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files (x86)\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra 'Tools' menuitem: @C:\Program Files (x86)\Windows Live\Writer\WindowsLiveWriterShortcuts.dll,-1003 - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files (x86)\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra button: Add to VideoGet - {88CFA58B-A63F-4A94-9C54-0C7A58E3333E} - C:\PROGRA~2\NUCLEA~1\VideoGet\Plugins\VIDEOG~1.DLL
O9 - Extra 'Tools' menuitem: Add to &VideoGet - {88CFA58B-A63F-4A94-9C54-0C7A58E3333E} - C:\PROGRA~2\NUCLEA~1\VideoGet\Plugins\VIDEOG~1.DLL
O9 - Extra button: Toon of verberg HP Smart Web Printing - {DDE87865-83C5-48c4-8357-2F5B1AA84522} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_BHO.dll
O10 - Unknown file in Winsock LSP: c:\program files (x86)\common files\microsoft shared\windows live\wlidnsp.dll
O10 - Unknown file in Winsock LSP: c:\program files (x86)\common files\microsoft shared\windows live\wlidnsp.dll
O11 - Options group: [ACCELERATED_GRAPHICS] Accelerated graphics
O16 - DPF: {28B66320-9687-4B13-8757-36F901887AB5} (CanvasX Class) - http://foto.blokker.nl/ips-opdata/layou ... anvasx.cab
O16 - DPF: {9191F686-7F0A-441D-8A98-2FE3AC1BD913} (ActiveScan 2.0 Installer Class) - http://acs.pandasoftware.com/activescan ... stubie.cab
O18 - Protocol: wlpg - {E43EF6CD-A37A-4A9B-9E6F-83F89B8E6324} - C:\Program Files (x86)\Windows Live\Photo Gallery\AlbumDownloadProtocolHandler.dll
O20 - AppInit_DLLs: C:/PROGRA~3/{66DE8~1/deta.dll
O23 - Service: Adobe Acrobat Update Service (AdobeARMservice) - Adobe Systems Incorporated - C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe
O23 - Service: Adobe Flash Player Update Service (AdobeFlashPlayerUpdateSvc) - Adobe Systems Incorporated - C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe
O23 - Service: @%SystemRoot%\system32\Alg.exe,-112 (ALG) - Unknown owner - C:\Windows\System32\alg.exe (file missing)
O23 - Service: AMD External Events Utility - Unknown owner - C:\Windows\system32\atiesrxx.exe (file missing)
O23 - Service: ASGT - Unknown owner - C:\Windows\SysWOW64\ASGT.exe
O23 - Service: @%SystemRoot%\system32\efssvc.dll,-100 (EFS) - Unknown owner - C:\Windows\System32\lsass.exe (file missing)
O23 - Service: @%systemroot%\system32\fxsresm.dll,-118 (Fax) - Unknown owner - C:\Windows\system32\fxssvc.exe (file missing)
O23 - Service: Freemake Improver - Freemake - C:\ProgramData\Freemake\FreemakeUtilsService\FreemakeUtilsService.exe
O23 - Service: NVIDIA GeForce Experience Service (GfExperienceService) - NVIDIA Corporation - C:\Program Files\NVIDIA Corporation\GeForce Experience Service\GfExperienceService.exe
O23 - Service: Google Updateservice (gupdate) (gupdate) - Google Inc. - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
O23 - Service: Google Update-service (gupdatem) (gupdatem) - Google Inc. - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
O23 - Service: Google Software Updater (gusvc) - Google - C:\Program Files (x86)\Google\Common\Google Updater\GoogleUpdaterService.exe
O23 - Service: Intel(R) Rapid Storage Technology (IAStorDataMgrSvc) - Intel Corporation - C:\Program Files (x86)\Intel\Intel(R) Rapid Storage Technology\IAStorDataMgrSvc.exe
O23 - Service: @%SystemRoot%\system32\ieetwcollectorres.dll,-1000 (IEEtwCollectorService) - Unknown owner - C:\Windows\system32\IEEtwCollector.exe (file missing)
O23 - Service: @keyiso.dll,-100 (KeyIso) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: Mozilla Maintenance Service (MozillaMaintenance) - Mozilla Foundation - C:\Program Files (x86)\Mozilla Maintenance Service\maintenanceservice.exe
O23 - Service: @comres.dll,-2797 (MSDTC) - Unknown owner - C:\Windows\System32\msdtc.exe (file missing)
O23 - Service: Panda Internet Security 2015 Service (NanoServiceMain) - Panda Security, S.L. - C:\Program Files (x86)\Panda Security\Panda Security Protection\PSANHost.exe
O23 - Service: NBService - Nero AG - C:\Program Files (x86)\Nero\Nero 7\Nero BackItUp\NBService.exe
O23 - Service: @%SystemRoot%\System32\netlogon.dll,-102 (Netlogon) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: NMIndexingService - Nero AG - C:\Program Files (x86)\Common Files\Ahead\Lib\NMIndexingService.exe
O23 - Service: NVIDIA Network Service (NvNetworkService) - NVIDIA Corporation - C:\Program Files (x86)\NVIDIA Corporation\NetService\NvNetworkService.exe
O23 - Service: NVIDIA Streamer Service (NvStreamSvc) - NVIDIA Corporation - C:\Program Files\NVIDIA Corporation\NvStreamSrv\nvstreamsvc.exe
O23 - Service: NVIDIA Display Driver Service (nvsvc) - Unknown owner - C:\Windows\system32\nvvsvc.exe (file missing)
O23 - Service: Panda Devices Agent (PandaAgent) - Panda Security, S.L. - C:\Program Files (x86)\Panda Security\Panda Devices Agent\AgentSvc.exe
O23 - Service: @%systemroot%\system32\psbase.dll,-300 (ProtectedStorage) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: Protexis Licensing V2 (PSI_SVC_2) - Protexis Inc. - c:\Program Files (x86)\Common Files\Protexis\License Service\PsiService_2.exe
O23 - Service: Panda Product Service (PSUAService) - Panda Security, S.L. - C:\Program Files (x86)\Panda Security\Panda Security Protection\PSUAService.exe
O23 - Service: Cyberlink RichVideo Service(CRVS) (RichVideo) - Unknown owner - C:\Program Files (x86)\CyberLink\Shared files\RichVideo.exe
O23 - Service: @%systemroot%\system32\Locator.exe,-2 (RpcLocator) - Unknown owner - C:\Windows\system32\locator.exe (file missing)
O23 - Service: @%SystemRoot%\system32\samsrv.dll,-1 (SamSs) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\snmptrap.exe,-3 (SNMPTRAP) - Unknown owner - C:\Windows\System32\snmptrap.exe (file missing)
O23 - Service: @%systemroot%\system32\spoolsv.exe,-1 (Spooler) - Unknown owner - C:\Windows\System32\spoolsv.exe (file missing)
O23 - Service: @%SystemRoot%\system32\sppsvc.exe,-101 (sppsvc) - Unknown owner - C:\Windows\system32\sppsvc.exe (file missing)
O23 - Service: NVIDIA Stereoscopic 3D Driver Service (Stereo Service) - NVIDIA Corporation - C:\Program Files (x86)\NVIDIA Corporation\3D Vision\nvSCPAPISvr.exe
O23 - Service: @%SystemRoot%\system32\ui0detect.exe,-101 (UI0Detect) - Unknown owner - C:\Windows\system32\UI0Detect.exe (file missing)
O23 - Service: Update DigiHelp - Unknown owner - C:\Program Files (x86)\DigiHelp\updateDigiHelp.exe
O23 - Service: Util DigiHelp - Unknown owner - C:\Program Files (x86)\DigiHelp\bin\utilDigiHelp.exe
O23 - Service: @%SystemRoot%\system32\vaultsvc.dll,-1003 (VaultSvc) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\vds.exe,-100 (vds) - Unknown owner - C:\Windows\System32\vds.exe (file missing)
O23 - Service: @%systemroot%\system32\vssvc.exe,-102 (VSS) - Unknown owner - C:\Windows\system32\vssvc.exe (file missing)
O23 - Service: @%SystemRoot%\system32\Wat\WatUX.exe,-601 (WatAdminSvc) - Unknown owner - C:\Windows\system32\Wat\WatAdminSvc.exe (file missing)
O23 - Service: @%systemroot%\system32\wbengine.exe,-104 (wbengine) - Unknown owner - C:\Windows\system32\wbengine.exe (file missing)
O23 - Service: @%Systemroot%\system32\wbem\wmiapsrv.exe,-110 (wmiApSrv) - Unknown owner - C:\Windows\system32\wbem\WmiApSrv.exe (file missing)
O23 - Service: @%PROGRAMFILES%\Windows Media Player\wmpnetwk.exe,-101 (WMPNetworkSvc) - Unknown owner - C:\Program Files (x86)\Windows Media Player\wmpnetwk.exe (file missing)
--
End of file - 14126 bytes
Alvast hartelijk dank.
MartinSr
Medion Akoya ,Windows 10 / Intel Pentium G6960 processor. AMD Radeon HD 6670 / 512 MB DDRS geheugen. 4 GB werkgeheugen. 1.5 TB harde schijf. /Microsoft Edge /Windows Live Mail/ Windows Defender / Nero DVD/CD Brander/HP ENVY 4500

 SeniorenNet