Sony,
hierbij hjt log, en adw log na de clean..
die pc tunekrijg ik nog altijd...
grten
ghis
Logfile of Trend Micro HijackThis v2.0.5
Scan saved at 9:49:48, on 29/08/2016
Platform: Windows 7 SP1 (WinNT 6.00.3505)
MSIE: Internet Explorer v10.0 (10.00.9200.16635)
Boot mode: Normal
Running processes:
C:\Program Files (x86)\Intel\Intel Matrix Storage Manager\IAAnotif.exe
C:\Program Files (x86)\EgisTec MyWinLocker\x86\mwlDaemon.exe
C:\Program Files (x86)\Acer\Hotkey Utility\HotkeyUtility.exe
C:\Program Files (x86)\epson\Creativity Suite\Event Manager\EEventManager.exe
C:\Program Files (x86)\Microsoft Office\Office12\ONENOTEM.EXE
C:\Program Files (x86)\Internet Explorer\IEXPLORE.EXE
C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbarUser_32.exe
C:\Users\Georges\Desktop\HijackThis.exe
R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Bar = Preserve
R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Page =
http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page =
https://www.google.be/
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL =
http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Local Page = C:\Windows\SysWOW64\blank.htm
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = *.local
R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
F2 - REG:system.ini: UserInit=userinit.exe,
O2 - BHO: Google Toolbar Helper - {AA58ED58-01DD-4d91-8333-CF10577473F7} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O3 - Toolbar: Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O4 - HKLM\..\Run: [Hotkey Utility] C:\Program Files (x86)\Acer\Hotkey Utility\HotkeyUtility.exe
O4 - HKLM\..\Run: [GrooveMonitor] "C:\Program Files (x86)\Microsoft Office\Office12\GrooveMonitor.exe"
O4 - HKLM\..\Run: [EEventManager] C:\Program Files (x86)\EPSON\Creativity Suite\Event Manager\EEventManager.exe
O4 - HKLM\..\Run: [AVG_UI] "C:\Program Files (x86)\AVG\Av\avuirunnerx.exe" C:\Program Files (x86)\AVG\Av\avgui.exe
O4 - HKLM\..\Run: [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
O4 - HKCU\..\Run: [Google Update] "C:\Users\Georges\AppData\Local\Google\Update\GoogleUpdate.exe" /c
O4 - HKUS\S-1-5-19\..\Run: [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun (User 'LOCAL SERVICE')
O4 - HKUS\S-1-5-19\..\RunOnce: [mctadmin] C:\Windows\System32\mctadmin.exe (User 'LOCAL SERVICE')
O4 - HKUS\S-1-5-20\..\Run: [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun (User 'NETWORK SERVICE')
O4 - HKUS\S-1-5-20\..\RunOnce: [mctadmin] C:\Windows\System32\mctadmin.exe (User 'NETWORK SERVICE')
O4 - Startup: OneNote 2007 Schermopname en Snel starten.lnk = C:\Program Files (x86)\Microsoft Office\Office12\ONENOTEM.EXE
O9 - Extra button: In weblog opnemen - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files (x86)\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra 'Tools' menuitem: &In weblog opnemen met Windows Live Writer - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files (x86)\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra button: Verzenden naar OneNote - {2670000A-7350-4f3c-8081-5663EE0C6C49} - C:\PROGRA~2\MICROS~2\Office12\ONBttnIE.dll
O9 - Extra 'Tools' menuitem: Verz&enden naar OneNote - {2670000A-7350-4f3c-8081-5663EE0C6C49} - C:\PROGRA~2\MICROS~2\Office12\ONBttnIE.dll
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~2\MICROS~2\Office12\REFIEBAR.DLL
O11 - Options group: [ACCELERATED_GRAPHICS] Accelerated graphics
O16 - DPF: {19D6A3D5-EA50-4C3B-88F0-79627C325570} (IlosoftMultipleImageCtrl Class) -
http://iloapp.fotoclub-kiknu-wervik.be/ ... Upload.dll
O18 - Protocol: grooveLocalGWS - {88FED34C-F0CA-4636-A375-3CB6248B04CD} - C:\Program Files (x86)\Microsoft Office\Office12\GrooveSystemServices.dll
O23 - Service: Adobe Version Cue CS3 {nl_NL} (Adobe Version Cue CS3) - Adobe Systems Incorporated - C:\Program Files (x86)\Common Files\Adobe\Adobe Version Cue CS3\Server\bin\VersionCueCS3.exe
O23 - Service: Adobe Acrobat Update Service (AdobeARMservice) - Adobe Systems Incorporated - C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe
O23 - Service: Adobe Flash Player Update Service (AdobeFlashPlayerUpdateSvc) - Adobe Systems Incorporated - C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe
O23 - Service: @%SystemRoot%\system32\Alg.exe,-112 (ALG) - Unknown owner - C:\Windows\System32\alg.exe (file missing)
O23 - Service: AvgAMPS - AVG Technologies CZ, s.r.o. - C:\Program Files (x86)\AVG\Av\avgamps.exe
O23 - Service: AVGIDSAgent - AVG Technologies CZ, s.r.o. - C:\Program Files (x86)\AVG\Av\avgidsagenta.exe
O23 - Service: AVG Service (avgsvc) - AVG Technologies CZ, s.r.o. - C:\Program Files (x86)\AVG\Framework\Common\avgsvca.exe
O23 - Service: AVG WatchDog (avgwd) - AVG Technologies CZ, s.r.o. - C:\Program Files (x86)\AVG\Av\avgwdsvca.exe
O23 - Service: Canon Camera Access Library 8 (CCALib8) - Canon Inc. - C:\Program Files (x86)\Canon\CAL\CALMAIN.exe
O23 - Service: @%SystemRoot%\system32\efssvc.dll,-100 (EFS) - Unknown owner - C:\Windows\System32\lsass.exe (file missing)
O23 - Service: @%systemroot%\system32\fxsresm.dll,-118 (Fax) - Unknown owner - C:\Windows\system32\fxssvc.exe (file missing)
O23 - Service: FLEXnet Licensing Service - Macrovision Europe Ltd. - C:\Program Files (x86)\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe
O23 - Service: GRegService (Greg_Service) - Acer Incorporated - C:\Program Files (x86)\Acer\Registration\GregHSRW.exe
O23 - Service: Google Updateservice (gupdate) (gupdate) - Google Inc. - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
O23 - Service: Google Update-service (gupdatem) (gupdatem) - Google Inc. - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
O23 - Service: Google Software Updater (gusvc) - Google - C:\Program Files (x86)\Google\Common\Google Updater\GoogleUpdaterService.exe
O23 - Service: Intel(R) Matrix Storage Event Monitor (IAANTMON) - Intel Corporation - C:\Program Files (x86)\Intel\Intel Matrix Storage Manager\IAANTMon.exe
O23 - Service: @keyiso.dll,-100 (KeyIso) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @comres.dll,-2797 (MSDTC) - Unknown owner - C:\Windows\System32\msdtc.exe (file missing)
O23 - Service: MyWinLocker Service (MWLService) - Egis Technology Inc. - C:\Program Files (x86)\EgisTec MyWinLocker\x86\MWLService.exe
O23 - Service: Nero BackItUp Scheduler 4.0 - Nero AG - C:\Program Files (x86)\Common Files\Nero\Nero BackItUp 4\NBService.exe
O23 - Service: @%SystemRoot%\System32\netlogon.dll,-102 (Netlogon) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%systemroot%\system32\psbase.dll,-300 (ProtectedStorage) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: Cyberlink RichVideo Service(CRVS) (RichVideo) - Unknown owner - C:\Program Files (x86)\Cyberlink\Shared files\RichVideo.exe
O23 - Service: @%systemroot%\system32\Locator.exe,-2 (RpcLocator) - Unknown owner - C:\Windows\system32\locator.exe (file missing)
O23 - Service: @%SystemRoot%\system32\samsrv.dll,-1 (SamSs) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\snmptrap.exe,-3 (SNMPTRAP) - Unknown owner - C:\Windows\System32\snmptrap.exe (file missing)
O23 - Service: @%systemroot%\system32\spoolsv.exe,-1 (Spooler) - Unknown owner - C:\Windows\System32\spoolsv.exe (file missing)
O23 - Service: @%SystemRoot%\system32\sppsvc.exe,-101 (sppsvc) - Unknown owner - C:\Windows\system32\sppsvc.exe (file missing)
O23 - Service: @%SystemRoot%\system32\ui0detect.exe,-101 (UI0Detect) - Unknown owner - C:\Windows\system32\UI0Detect.exe (file missing)
O23 - Service: Updater Service - Acer Group - C:\Program Files\Acer\Acer Updater\UpdaterService.exe
O23 - Service: @%SystemRoot%\system32\vaultsvc.dll,-1003 (VaultSvc) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\vds.exe,-100 (vds) - Unknown owner - C:\Windows\System32\vds.exe (file missing)
O23 - Service: @%systemroot%\system32\vssvc.exe,-102 (VSS) - Unknown owner - C:\Windows\system32\vssvc.exe (file missing)
O23 - Service: @%SystemRoot%\system32\Wat\WatUX.exe,-601 (WatAdminSvc) - Unknown owner - C:\Windows\system32\Wat\WatAdminSvc.exe (file missing)
O23 - Service: @%systemroot%\system32\wbengine.exe,-104 (wbengine) - Unknown owner - C:\Windows\system32\wbengine.exe (file missing)
O23 - Service: @%Systemroot%\system32\wbem\wmiapsrv.exe,-110 (wmiApSrv) - Unknown owner - C:\Windows\system32\wbem\WmiApSrv.exe (file missing)
O23 - Service: @%PROGRAMFILES%\Windows Media Player\wmpnetwk.exe,-101 (WMPNetworkSvc) - Unknown owner - C:\Program Files (x86)\Windows Media Player\wmpnetwk.exe (file missing)
--
End of file - 9276 bytes
# AdwCleaner v6.010 - Logfile created 29/08/2016 at 10:11:31
# Updated on 12/08/2016 by ToolsLib
# Database : 2016-08-28.2 [Server]
# Operating System : Windows 7 Home Premium Service Pack 1 (X64)
# Username : Georges - GEORGES-PC
# Running from : C:\Users\Georges\Desktop\adwcleaner_6.010.exe
# Mode: Clean
# Support :
https://toolslib.net/forum
***** [ Services ] *****
***** [ Folders ] *****
***** [ Files ] *****
***** [ DLL ] *****
***** [ WMI ] *****
***** [ Shortcuts ] *****
***** [ Scheduled Tasks ] *****
***** [ Registry ] *****
***** [ Web browsers ] *****
*************************
:: "Tracing" keys deleted
:: Winsock settings cleared
*************************
C:\AdwCleaner\AdwCleaner[C1].txt - [3533 Bytes] - [16/05/2016 17:14:14]
C:\AdwCleaner\AdwCleaner[C2].txt - [1364 Bytes] - [26/08/2016 11:41:28]
C:\AdwCleaner\AdwCleaner[C3].txt - [1425 Bytes] - [28/08/2016 15:18:00]
C:\AdwCleaner\AdwCleaner[C4].txt - [982 Bytes] - [29/08/2016 10:11:31]
C:\AdwCleaner\AdwCleaner[S1].txt - [3332 Bytes] - [16/05/2016 17:06:07]
C:\AdwCleaner\AdwCleaner[S2].txt - [1450 Bytes] - [26/08/2016 11:27:04]
C:\AdwCleaner\AdwCleaner[S3].txt - [1447 Bytes] - [28/08/2016 14:52:46]
C:\AdwCleaner\AdwCleaner[S4].txt - [1520 Bytes] - [28/08/2016 15:08:53]
C:\AdwCleaner\AdwCleaner[S5].txt - [1593 Bytes] - [28/08/2016 15:17:45]
C:\AdwCleaner\AdwCleaner[S6].txt - [1739 Bytes] - [29/08/2016 10:10:40]
########## EOF - C:\AdwCleaner\AdwCleaner[C4].txt - [1492 Bytes] ##########
#





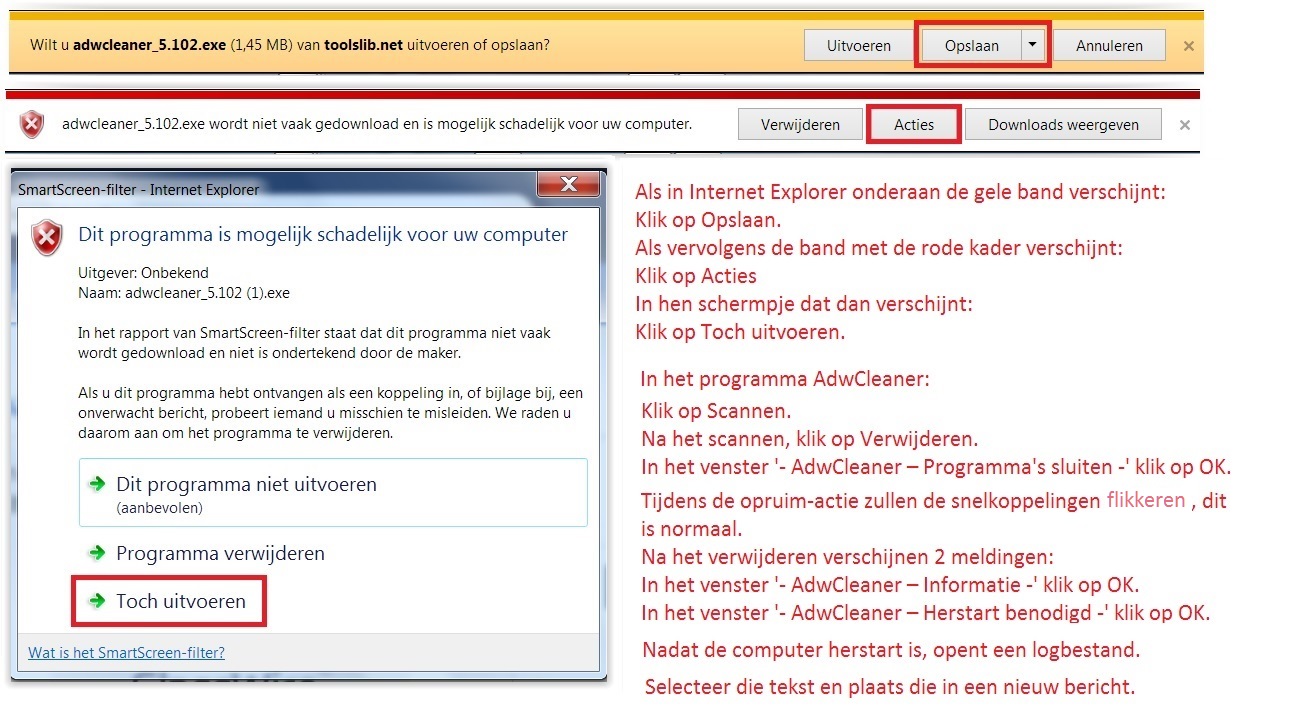


 Downloaden en opslaan niet installeren
 Deze downloaden en uitvoeren.